How to Configure Brotli Compression in Nginx & Apache (Better than Gzip)
Quick Technical Answer: To activate Brotli compression on Ubuntu Nginx: Install the official Google Brotli module with sudo apt install -y libnginx-mod-brotli. Inside your http {} block in /etc/nginx/nginx.conf, add brotli on;, brotli_comp_level 6;, brotli_static on;, and declare text MIME types using brotli_types text/plain text/css application/javascript application/json image/svg+xml;. Test live activation with curl -I -H … Read more
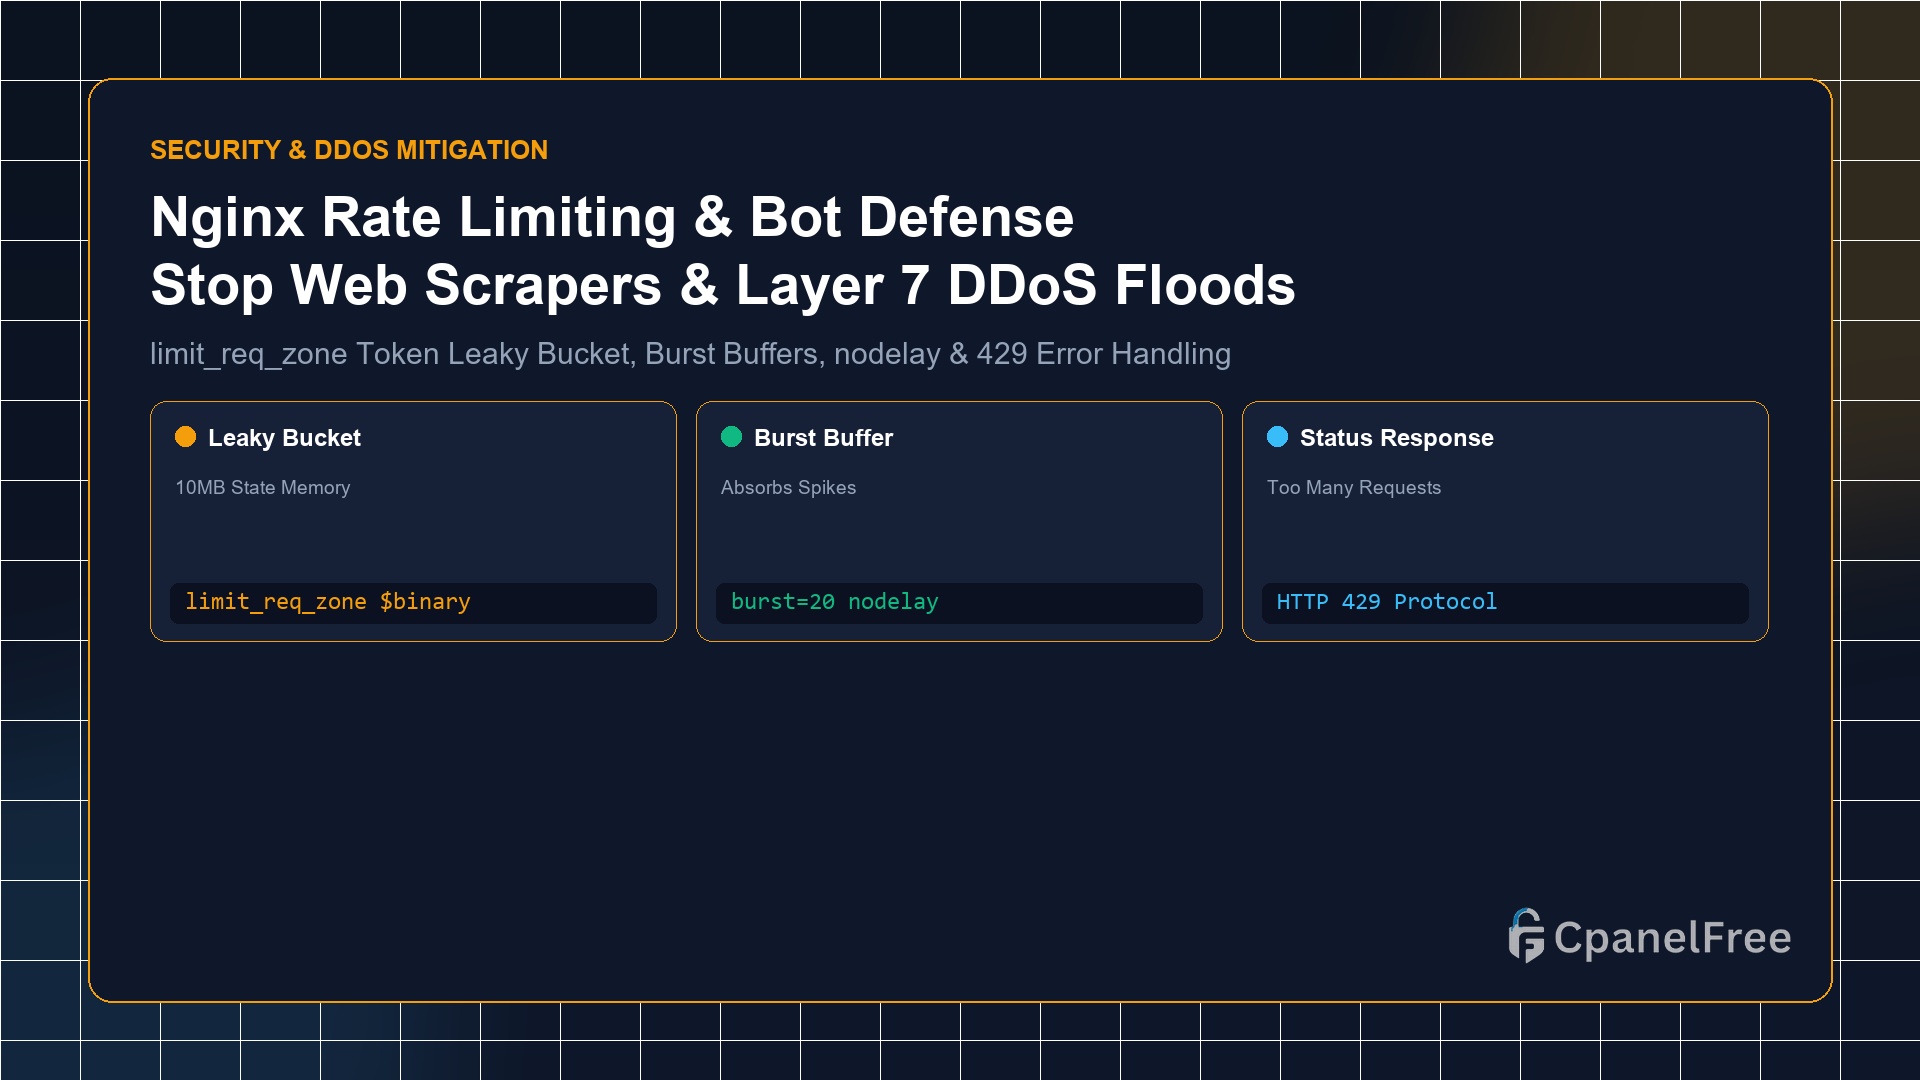
How to Set Up Nginx Rate Limiting to Stop Scrapers, Bots and Application Layer DDoS

Quick Technical Answer: To enforce rate limiting in Nginx: In the http {} block of /etc/nginx/nginx.conf, define a shared memory zone: limit_req_zone $binary_remote_addr zone=api_limit:10m rate=10r/s;. Then apply it to sensitive endpoints (such as wp-login.php or /api/) inside your server {} block: limit_req zone=api_limit burst=20 nodelay; and configure limit_req_status 429;. This buffers legitimate user spikes while … Read more

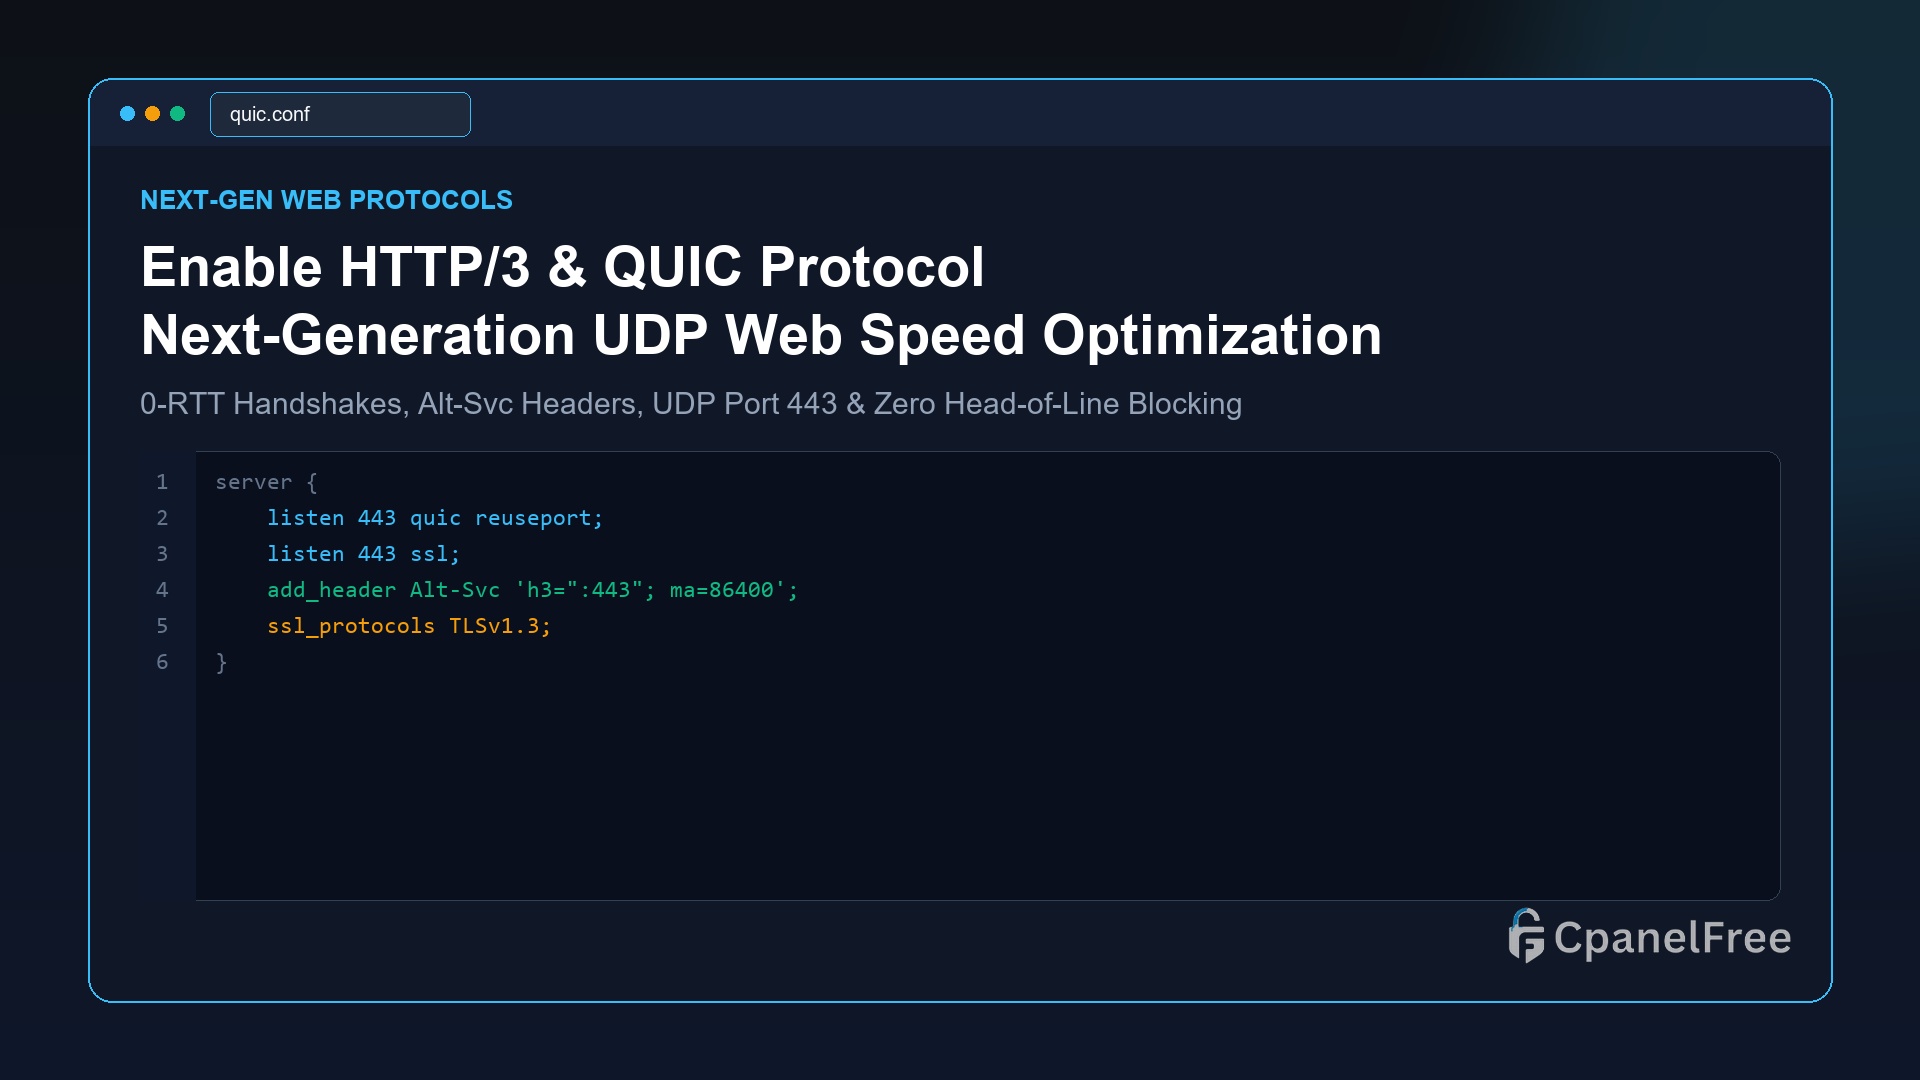
How to Enable HTTP/3 (QUIC) on Nginx and OpenLiteSpeed for Blazing Mobile Speeds

Quick Technical Answer: To activate HTTP/3 (QUIC) on Nginx (v1.25+): Add listen 443 quic reuseport; alongside standard SSL, enable ssl_protocols TLSv1.3;, and broadcast QUIC capability to browsers using add_header Alt-Svc ‘h3=”:443″; ma=86400’;. Open UDP port 443 in your firewall (sudo ufw allow 443/udp). On OpenLiteSpeed, HTTP/3 is compiled natively and can be enabled with one … Read more

How to Set Up HAProxy as a Layer 7 Load Balancer for High-Availability Web Apps

Quick Technical Answer: To deploy HAProxy as an HTTP/HTTPS Layer 7 load balancer on Ubuntu: Install with sudo apt install -y haproxy. Edit /etc/haproxy/haproxy.cfg to define a frontend http_front listening on port 80/443 and a backend web_servers containing your application node IP addresses with balance roundrobin and check enabled for continuous health monitoring. Enable the … Read more

How to Configure Traefik as a Dynamic Reverse Proxy for Docker Containers

Quick Technical Answer: To configure Traefik v3 as a dynamic Docker reverse proxy: Deploy Traefik via Docker Compose, mounting /var/run/docker.sock and listening on ports 80 and 443. Enable the Docker provider (–providers.docker=true) and ACME resolver. For any application container (e.g. Nextcloud, WordPress, or Node.js), simply attach Docker labels: traefik.enable=true, traefik.http.routers.myapp.rule=Host(`myapp.yourdomain.com`), and traefik.http.routers.myapp.tls.certresolver=myresolver. Traefik auto-discovers the … Read more

Caddy Web Server vs Nginx: Which is Better for Modern Web Hosting in 2026?

Quick Technical Answer: Choose Caddy if you want zero-configuration automated HTTPS (Let’s Encrypt/ZeroSSL certificates generated and renewed by default), modern HTTP/3 QUIC out of the box, and a clean 3-line Caddyfile reverse proxy configuration. Choose Nginx if you require maximum raw concurrent connection throughput (50,000+ requests/sec), strict low-RAM footprint (<10MB physical RAM in C), legacy … Read more

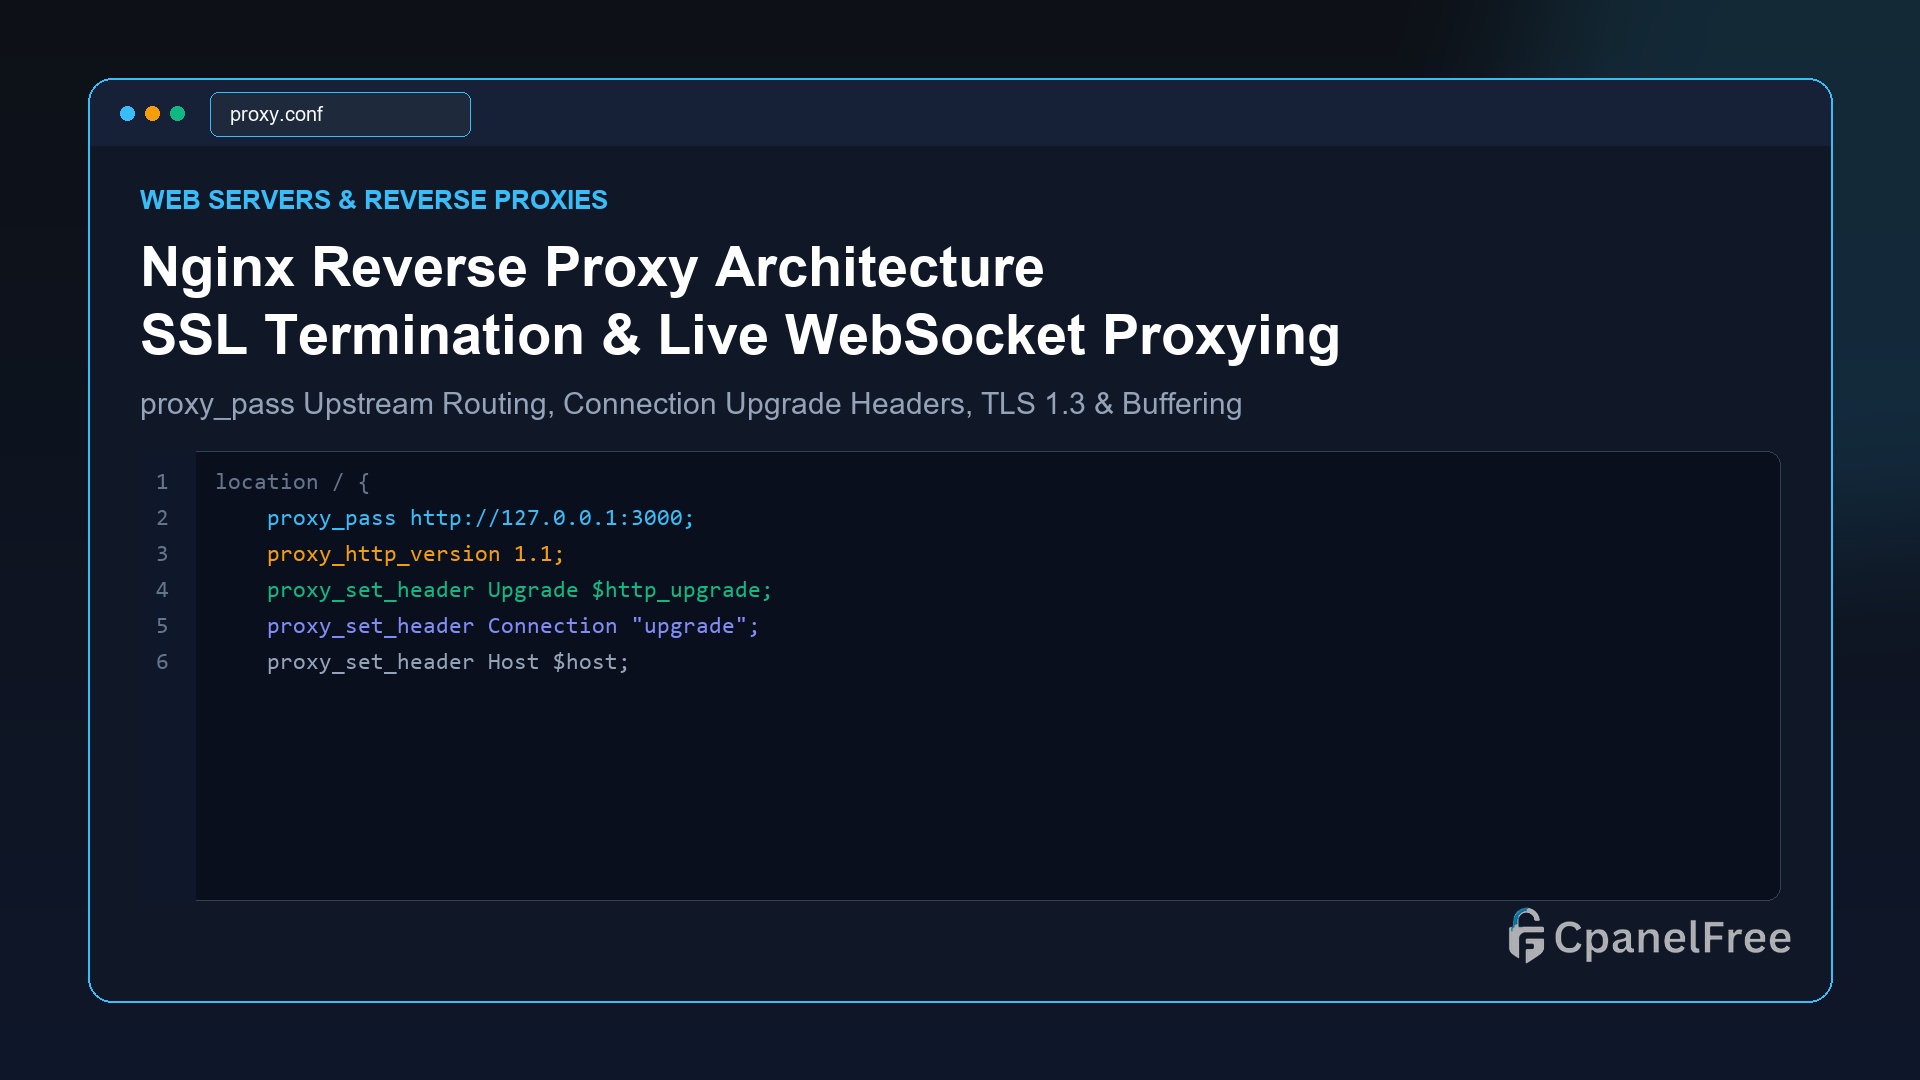
How to Configure Nginx as a Reverse Proxy with SSL Termination & WebSockets

Quick Technical Answer: To route incoming traffic to backend applications (Node.js, Python FastAPI, Go, or Docker) with Nginx: Define an upstream block or use proxy_pass http://127.0.0.1:3000; inside your location / block. Always forward client IP headers using proxy_set_header X-Real-IP $remote_addr; and proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;. For WebSockets, add proxy_http_version 1.1;, proxy_set_header Upgrade $http_upgrade;, and proxy_set_header Connection … Read more

How to Manage Linux User Groups, Sudoers Privileges & Audit Sudo History

Quick Technical Answer: To safely delegate administrative rights without sharing root passwords: Create a dedicated user with sudo adduser devops, and append them to the administrative sudo group using sudo usermod -aG sudo devops. To grant granular permission for specific commands (e.g. restarting Nginx) without password prompts, create a file at /etc/sudoers.d/devops using sudo visudo … Read more

How to Set Up ZFS or Btrfs on Linux VPS for Snapshot Backups and Compression

Quick Technical Answer: To deploy ZFS on an attached block volume on Ubuntu: Install tools with sudo apt install -y zfsutils-linux, create a pool using sudo zpool create mypool /dev/sdX, and enable transparent compression with sudo zfs set compression=zstd mypool. To take an instant sub-second snapshot before doing maintenance, run sudo zfs snapshot mypool/data@pre-update. If … Read more

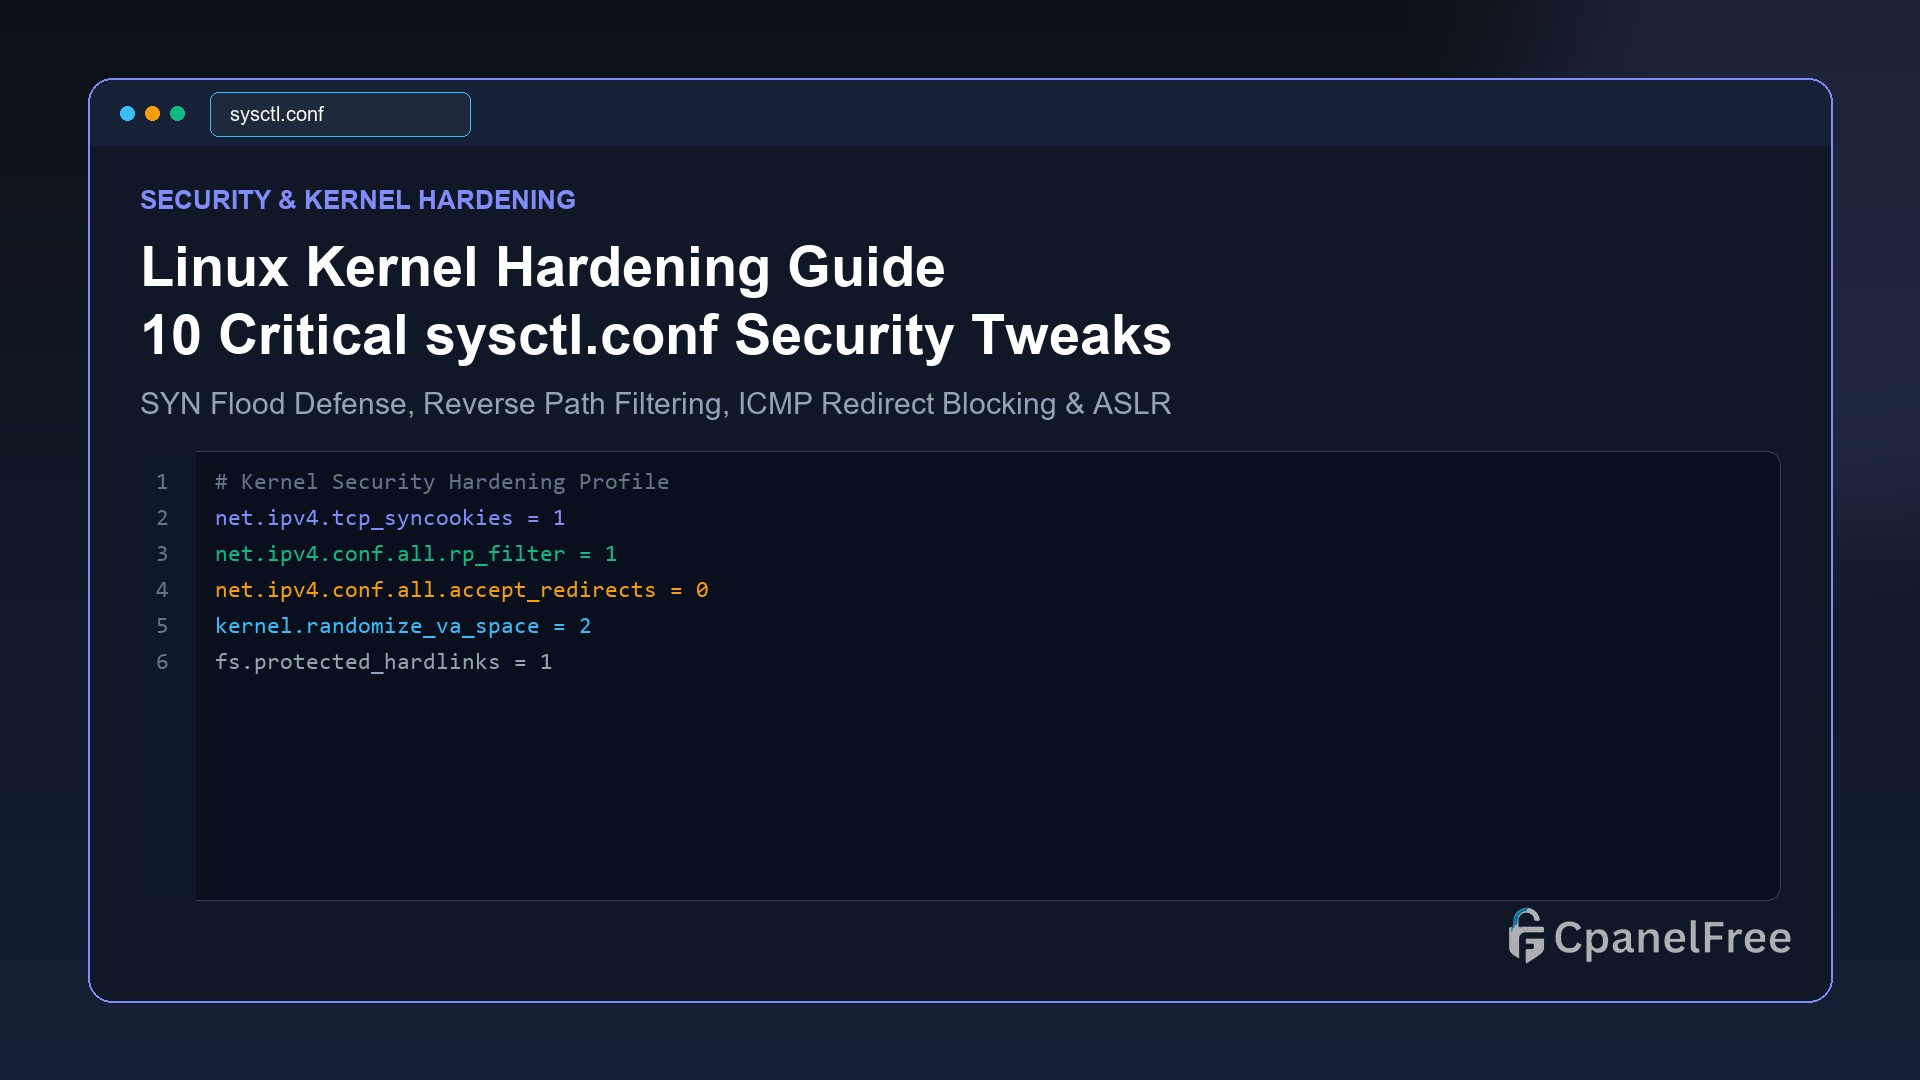
Linux Kernel Hardening: 10 Critical sysctl.conf Tweaks to Prevent SYN Floods & Spoofing

Quick Technical Answer: To harden the Linux kernel against network attacks, edit /etc/sysctl.d/99-security.conf. Enable TCP SYN cookies with net.ipv4.tcp_syncookies = 1 to survive SYN floods, enable reverse path filtering with net.ipv4.conf.all.rp_filter = 1 to block IP spoofing, disable ICMP redirects (accept_redirects = 0), and maximize ASLR memory protection with kernel.randomize_va_space = 2. Apply immediately with … Read more