
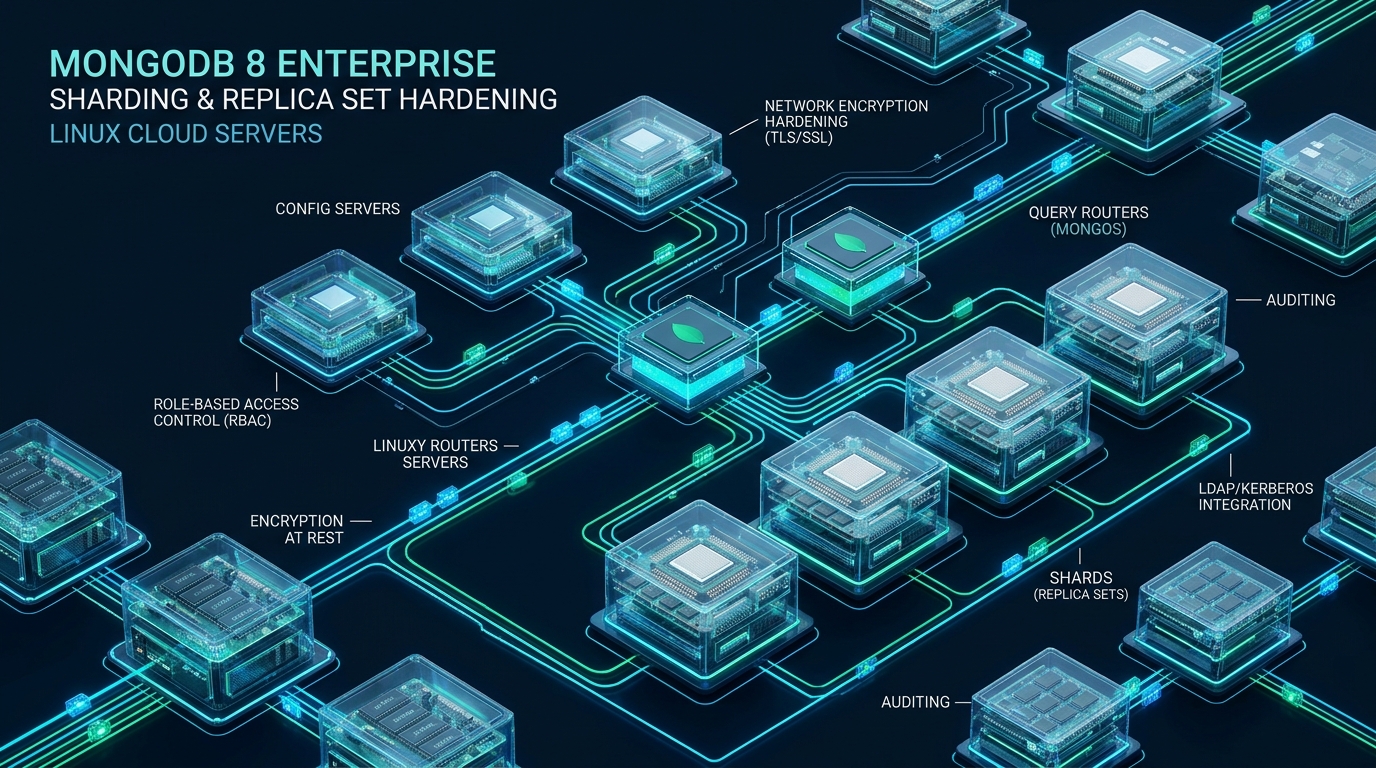
Operating mission-critical database clusters at enterprise scale requires rigorous isolation, deterministic I/O scheduling, and robust cryptographic defenses across the entire network fabric. As workloads expand beyond single-node throughput limits, running unhardened distributed databases on public cloud infrastructure exposes production systems to severe lock contention, runaway memory fragmentation, and unauthorized data exfiltration. By deploying hardened MongoDB 8 sharded clusters and replica sets on optimized cloud infrastructure from CpanelFree, systems architects can achieve sub-millisecond query latencies, seamless automated failover, and bulletproof operational security.
Direct Answer: Hardening MongoDB 8 Sharding & Replica Sets
MongoDB 8 Architectural Evolution & Cluster Topologies
MongoDB 8 introduces substantial architectural refinements to the WiredTiger storage engine, dynamic query planning, and sharded time-series collections. In high-concurrency environments, sharding distributes horizontal write loads across autonomous replica sets, coordinated by a dedicated Config Database Replica Set (CSRS) and routed through stateless mongos daemon instances. However, scaling horizontally magnifies underlying operating system misconfigurations and latency differentials between cluster members.
A resilient MongoDB 8 architecture consists of three fundamental layers:
- Config Server Replica Set (CSRS): A dedicated three-node replica set storing cluster metadata, chunk distribution tables, and routing catalogs. High availability and durability on this layer are non-negotiable.
- Stateless Query Routers (mongos): Gateways that cache cluster metadata and route client operations directly to target shards. Routers run behind local software load balancers or reside on application host nodes to eliminate additional network hops.
- Data Shards (Replica Sets): Independent primary-secondary-secondary replica sets storing discrete chunks of partitioned collections. Each replica set maintains its own consensus quorum and local oplog.
Linux Kernel & Subsystem Hardening for WiredTiger
The WiredTiger storage engine interacts heavily with Linux memory management subsystems. Default Linux distributions are tuned for general-purpose batch processing and desktop interactivity, resulting in aggressive memory compaction, page swap churn, and process preemption that degrade MongoDB throughput.
1. Disabling Transparent Huge Pages (THP)
Transparent Huge Pages allocate memory in 2MB blocks instead of standard 4KB pages. While advantageous for sequential workloads, database memory allocators like jemalloc and WiredTiger suffer extreme memory bloat, aggressive latency spikes during page defragmentation (khugepaged CPU saturation), and severe lock contention under high-velocity random I/O. THP must be completely disabled at boot.
2. Memory Swappiness and Dirty Page Flush Tuning
Setting vm.swappiness=1 instructs the kernel to exhaust anonymous memory pages only when physical RAM is critically depleted, avoiding premature eviction of active WiredTiger cache pages. Concurrently, tuning vm.dirty_ratio and vm.dirty_background_ratio ensures continuous, background flushing of dirty blocks to NVMe storage, preventing write stalls caused by synchronous kernel flush bottlenecks.
Performance & Security Comparison Matrix
Below is a comparative breakdown evaluating a standard unhardened MongoDB 8 deployment against a production-hardened sharded cluster configured in compliance with enterprise security and systems standards.
Production Configuration Files & Implementation
Deploy the following system-level and daemon configuration files across all physical or virtual Linux nodes participating in the MongoDB 8 cluster.
1. Systemd Unit: Transparent Huge Pages Disabler
Save this service unit to /etc/systemd/system/disable-transparent-huge-pages.service to permanently disable THP across system reboots:
[Unit]
Description=Disable Transparent Huge Pages (THP) for MongoDB 8
DefaultDependencies=no
After=sysinit.target local-fs.target
Before=mongod.service

[Service]
Type=oneshot
ExecStart=/bin/sh -c 'echo never > /sys/kernel/mm/transparent_hugepage/enabled && echo never > /sys/kernel/mm/transparent_hugepage/defrag'

[Install]
WantedBy=basic.target
2. Linux Kernel Sysctl Optimization
Save the following parameters to /etc/sysctl.d/99-mongodb-hardened.conf and apply them with sysctl --system:
# /etc/sysctl.d/99-mongodb-hardened.conf
# Minimize kernel swapping aggression
vm.swappiness = 1

# Maximize memory mapping areas for WiredTiger
vm.max_map_count = 262144

# Flush dirty memory pages to disk smoothly without latency spikes
vm.dirty_background_ratio = 5
vm.dirty_ratio = 10

# Network socket backlog and connection scaling
net.core.somaxconn = 65535
net.ipv4.tcp_max_syn_backlog = 65535
net.ipv4.tcp_fin_timeout = 15
net.ipv4.tcp_keepalive_time = 300
net.ipv4.tcp_keepalive_intvl = 60
net.ipv4.tcp_keepalive_probes = 5

# Ephemeral port range
net.ipv4.ip_local_port_range = 1024 65535
3. User Limits Security Configuration
Prevent socket exhaustion and thread starvation by persisting limits to /etc/security/limits.d/99-mongodb.conf:
# /etc/security/limits.d/99-mongodb.conf
mongod soft nofile 64000
mongod hard nofile 64000
mongod soft nproc 64000
mongod hard nproc 64000
mongod soft memlock unlimited
mongod hard memlock unlimited
4. Hardened MongoDB 8 Shard Daemon Configuration
Apply this security-hardened configuration template to /etc/mongod.conf on each shard replica set member:
# /etc/mongod.conf - MongoDB 8 Hardened Shard Node
storage:
  dbPath: /var/lib/mongodb
  journal:
    enabled: true
  wiredTiger:
    engineConfig:
      cacheSizeGB: 14
      directoryForIndexes: true
    collectionConfig:
      blockCompressor: zstd
    indexConfig:
      prefixCompression: true

systemLog:
  destination: file
  logAppend: true
  path: /var/log/mongodb/mongod.log
  verbosity: 1

net:
  port: 27018
  bindIp: 10.240.0.12,127.0.0.1
  maxIncomingConnections: 32000
  tls:
    mode: requireTLS
    certificateKeyFile: /etc/ssl/mongodb/shard01.pem
    CAFile: /etc/ssl/mongodb/ca.crt
    clusterFile: /etc/ssl/mongodb/cluster-internal.pem
    allowConnectionsWithoutCertificates: false
    disabledProtocols: TLS1_0,TLS1_1,TLS1_2

processManagement:
  timeZoneInfo: /usr/share/zoneinfo
  fork: false

security:
  authorization: enabled
  clusterAuthMode: x509

replication:
  replSetName: shard01-rs
  oplogSizeMB: 51200

sharding:
clusterRole: shardsvrdisabledProtocols: TLS1_0,TLS1_1,TLS1_2 mandates TLS 1.3 exclusively. Combined with mutual x.509 certificate authentication (clusterAuthMode: x509), every internal cluster node cryptographically authenticates its peer against an internal private Certificate Authority (CA) before establishing replication or chunk migration streams.
Cluster Initialization & Sharding Strategy
Once the kernel and configuration files are applied across all nodes, initialize the cluster in strict operational order:
Step 1: Initialize the Config Server Replica Set
Connect to the primary CSRS node via mongosh using TLS credentials:
rs.initiate({
  _id: "csrs",
  configsvr: true,
  members: [
    { _id: 0, host: "10.240.0.10:27019", priority: 2 },
    { _id: 1, host: "10.240.0.11:27019", priority: 1 },
    { _id: 2, host: "10.240.0.12:27019", priority: 1 }
  ]
});
Step 2: Initialize Shard Replica Sets & Register with Mongos
After initiating the shard replica set on shard01-rs, connect to the stateless router daemon (mongos) on port 27017 to add the shard:
sh.addShard("shard01-rs/10.240.0.20:27018,10.240.0.21:27018,10.240.0.22:27018");
sh.addShard("shard02-rs/10.240.0.30:27018,10.240.0.31:27018,10.240.0.32:27018");
Step 3: Selecting Optimal Shard Keys
Selecting an improper shard key is the leading cause of unrecoverable database bottlenecks. Monotonically increasing keys (such as raw ObjectId or timestamps) funnel 100% of write throughput into a single shard, triggering continuous chunk splits and balancing overhead. Employ a compound hashed shard key to ensure even write dispersion across shards while retaining targeted range queries on secondary attributes:
// Enable sharding on the target database
sh.enableSharding("telemetry_db");

// Create compound index: hashed tenant_id + ascending created_at
db.events.createIndex({ tenant_id: "hashed", created_at: 1 });

// Shard the collection using the compound key
sh.shardCollection("telemetry_db.events", { tenant_id: "hashed", created_at: 1 });Frequently Asked Questions
Why must Transparent Huge Pages (THP) be disabled for MongoDB 8?
Transparent Huge Pages allocate memory in 2MB blocks instead of standard 4KB pages. In databases utilizing memory-mapped files and internal caching (WiredTiger), 2MB allocations lead to severe memory fragmentation, aggressive CPU spikes from the kernel khugepaged compaction thread, and unpredictable query latency stalls under high-concurrency workloads.
How does x.509 certificate authentication improve cluster security over keyfiles?
Shared keyfiles rely on symmetric shared secrets that are vulnerable to credential theft if a single node is compromised. Mutual x.509 authentication uses asymmetric public-key cryptography where each node possesses its own distinct private key and certificate signed by an internal CA, ensuring cryptographic non-repudiation and enabling instant certificate revocation without cluster-wide key rotation.
What is the optimal WiredTiger cache size formula on dedicated Linux servers?
The recommended production calculation is 50% of (Total RAM - 1 GB). Setting the cache higher leaves insufficient headroom for filesystem cache (which WiredTiger depends on for uncompressed read acceleration), connection overhead, and Linux kernel networking buffers, which risks triggering the Linux Out-Of-Memory (OOM) killer.
Can range sharding and hashed sharding be combined in MongoDB 8?
Yes, MongoDB 8 fully supports compound shard keys that combine a hashed prefix with range-based fields (e.g., { tenant_id: "hashed", timestamp: 1 }). This provides the optimal balance by distributing incoming write load evenly across all shards via the hash while maintaining efficient range queries for chronological data within an individual tenant.
Ready to Deploy High-Performance Infrastructure?
Experience blazing-fast NVMe storage, unmetered bandwidth, and enterprise LiteSpeed caching on CpanelFree.