
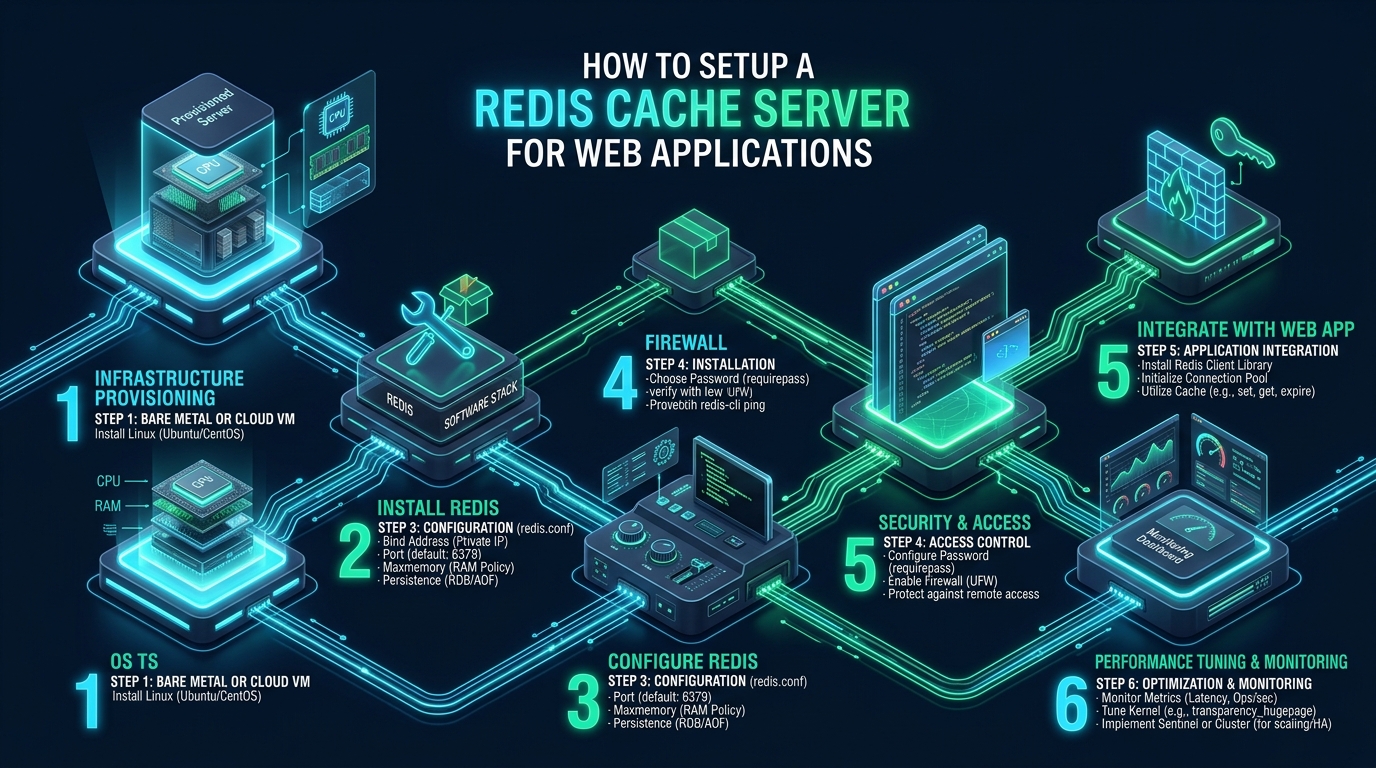
In high-concurrency web architectures, relational database bottlenecks represent the primary catalyst for severe response latency, application thread starvation, and cascading connection pool exhaustion under heavy traffic spikes. Offloading repetitive SQL query results, compiled template fragments, and transient session states to an in-memory key-value data store eliminates disk I/O penalties and transforms dynamic request throughput, whether managing developer staging environments on CpanelFree or scaling multi-tenant cluster tiers. Mastering a production-ready redis server setup linux deployment requires configuring precise kernel parameters, memory management bounds, connection pooling, and hardened network isolation to safeguard deterministic, sub-millisecond data retrieval.
Quick Answer: Setting Up a Redis Cache Server on Linux
maxmemory with an allkeys-lru eviction policy, disable Linux Transparent Huge Pages (THP), set vm.overcommit_memory = 1 in sysctl, and enforce robust ACL authentication with Unix domain sockets for minimal latency.Architectural Role of In-Memory Caching in Modern Web Stacks
Modern dynamic web applications—ranging from headless eCommerce architectures and microservices to WordPress, Drupal, and Laravel frameworks—execute dozens to hundreds of relational database queries for every HTTP request. Even with query caching and indexed columns in MySQL, MariaDB, or PostgreSQL, the overhead of connection handshakes, query parsing, table locks, and disk synchronization imposes a tangible latency floor, typically between 15ms and 80ms per dynamic page view.
Redis (Remote Dictionary Server) operates as an in-memory, single-threaded (with multi-threaded asynchronous I/O threads since Redis 6) key-value data structure store. Because working sets reside entirely in volatile RAM, read and write operations typically complete in less than 200 microseconds (0.2 milliseconds). When integrated as an application object cache, Redis intercepts database requests: identical queries hit memory instantly, bypassing the underlying relational database and reducing CPU load on database instances by up to 85%.
Beyond simple key-value lookups, Redis provides native data structures—including Hashes, Sets, Sorted Sets, Bitmaps, and HyperLogLogs—allowing developers to execute atomic counters, rate limiters, session stores, and real-time leaderboard computations without incurring relational schema overhead.
Production Matrix: Default vs. Enterprise Tuned Redis Setup
Out-of-the-box Redis installations on standard Linux distributions are tuned for general-purpose development rather than high-throughput production workloads. Deploying defaults into high-traffic environments frequently leads to packet dropping, latency spikes during memory allocation, and kernel out-of-memory (OOM) process termination.
| Feature / Metric | Standard / Default | Tuned / Production |
|---|---|---|
| Latency / Overhead | Baseline (1.2ms – 2.8ms TCP) | Optimal (0.15ms – 0.35ms Unix Socket) |
| Kernel Memory Overcommit | 0 (Heuristic Overcommit) | 1 (Always Overcommit / No BGSAVE OOM) |
| TCP Listen Backlog (somaxconn) | 128 / 511 | 65535 (Eliminates SYN Queue Drops) |
| Transparent Huge Pages (THP) | Always Enabled (High Latency Spikes) | Disabled (Eliminates Copy-on-Write Latency) |
| Memory Eviction Strategy | noeviction (Throws OOM errors when full) | allkeys-lru / volatile-lru (Automatic Pruning) |
| Disk I/O Write Amplification | RDB Snapshots + AOF Every Second | Disabled / Zero Disk I/O (Pure Volatile Cache) |
| Security & Access Control | No Password, Bind 127.0.0.1 only | Granular ACLs, requirepass, Dangerous Renames |
Step 1: Linux Operating System Kernel Tuning
Before installing Redis, the Linux kernel must be tuned to prevent memory allocation panics, slow socket handshakes, and jitter during snapshotting operations. Redis interacts directly with virtual memory via fork() and copy-on-write mechanisms; an untuned kernel will aggressively throttle or terminate Redis under heavy concurrent load.
1. Enable Memory Overcommit and Increase Socket Backlog
Create a dedicated sysctl configuration file at /etc/sysctl.d/99-redis.conf to ensure these network and virtual memory parameters persist across server reboots:
# /etc/sysctl.d/99-redis.conf - Production Kernel Parameters for Redis
# Set overcommit_memory to 1 to allow fork() copy-on-write allocations
vm.overcommit_memory = 1

# Increase system-wide socket listen queue backlog from default 128/511
net.core.somaxconn = 65535

# Increase maximum file descriptors and connection limits
fs.file-max = 2097152

# TCP buffer optimization for high-concurrency throughput
net.ipv4.tcp_max_syn_backlog = 65535
net.ipv4.tcp_fin_timeout = 15
net.ipv4.tcp_tw_reuse = 1
Apply the sysctl parameters immediately without rebooting the server:
sudo sysctl --systemArchitecture Note: Why is
vm.overcommit_memory = 1essential? When Redis performs background operations, it forks a child process. The Linux kernel uses copy-on-write (COW) memory virtualization. If overcommit is set to default (0), the kernel checks if enough free physical RAM exists to duplicate the entire Redis process. If your server has 16GB RAM and Redis consumes 10GB, the fork will fail with out-of-memory errors even if only 200MB of pages actually change during the operation.
2. Disable Linux Transparent Huge Pages (THP)
Transparent Huge Pages (THP) is an operating system feature that groups standard 4KB memory pages into 2MB memory blocks. While beneficial for certain batch processing workloads, THP is catastrophic for Redis. When Redis modifies a single key in memory during copy-on-write, the kernel must duplicate an entire 2MB huge page rather than a 4KB standard page, dramatically amplifying memory consumption and introducing latency spikes exceeding 50ms.
Create a dedicated systemd service to reliably disable THP during the boot sequence:
# /etc/systemd/system/disable-thp.service
[Unit]
Description=Disable Linux Transparent Huge Pages (THP) for Redis
DefaultDependencies=no
After=sysinit.target local-fs.target
Before=redis.service redis-server.service

[Service]
Type=oneshot
ExecStart=/bin/sh -c 'echo never > /sys/kernel/mm/transparent_hugepage/enabled && echo never > /sys/kernel/mm/transparent_hugepage/defrag'

[Install]
WantedBy=basic.target
Reload systemd, enable, and execute the service:
sudo systemctl daemon-reload
sudo systemctl enable --now disable-thp.service
cat /sys/kernel/mm/transparent_hugepage/enabled
# Expected output: always madvise [never]
Step 2: Installing Redis from Official Repositories
Default package managers in older Linux LTS versions often ship outdated Redis builds. For security patches, thread performance, and ACL capabilities, always install Redis from official upstream package repositories.
Installation on Ubuntu / Debian
sudo apt-get update
sudo apt-get install -y lsb-release curl gpg
curl -fsSL https://packages.redis.io/gpg | sudo gpg --dearmor -o /usr/share/keyrings/redis-archive-keyring.gpg
echo "deb [signed-by=/usr/share/keyrings/redis-archive-keyring.gpg] https://packages.redis.io/deb $(lsb_release -cs) main" | sudo tee /etc/apt/sources.list.d/redis.list
sudo apt-get update
sudo apt-get install -y redis-server
Installation on RHEL / Rocky Linux / AlmaLinux
sudo dnf install -y epel-release
sudo dnf install -y redis
sudo systemctl enable redis
Step 3: Hardened Production Redis Configuration
Open the primary configuration file located at /etc/redis/redis.conf (or /etc/redis.conf on Enterprise Linux). We will configure memory limits, eviction algorithms, network listening interfaces, security tokens, and disable persistence for pure volatile cache operation.
# ==============================================================================
# Enterprise Redis Production Cache Configuration (/etc/redis/redis.conf)
# ==============================================================================

# --- NETWORK & CONNECTION BOUNDS ---
# Listen strictly on localhost and private interface (NEVER 0.0.0.0 publicly)
bind 127.0.0.1 ::1
port 6379
protected-mode yes
tcp-backlog 65535
timeout 300
tcp-keepalive 300

# High-Performance Local Inter-Process Communication via Unix Domain Socket
unixsocket /var/run/redis/redis-server.sock
unixsocketperm 770

# --- PROCESS & SYSTEMD SUPERVISION ---
daemonize no
supervised systemd
pidfile /var/run/redis/redis-server.pid
loglevel notice
logfile /var/log/redis/redis-server.log

# --- MEMORY MANAGEMENT & EVICTION ---
# Set maximum memory limit (allocate ~65% to 75% of available server RAM)
maxmemory 4gb

# Evict the least recently used keys out of all keys when memory hits maxmemory
maxmemory-policy allkeys-lru
maxmemory-samples 7

# --- DISK PERSISTENCE OPTIMIZATION FOR PURE CACHING ---
# Disable RDB background snapshots to eliminate disk I/O write amplification
save ""

# Disable Append Only File (AOF) for pure volatile caching workloads
appendonly no

# --- SECURITY & COMMAND HARDENING ---
# Enforce a strong cryptographically generated password
requirepass 9f4a8b72c3d1e6f5a0b9c8d7e6f5a4b3c2d1e0f9a8b7c6d5e4f3a2b1c0d9e8f7

# Disable dangerous administrative commands that can freeze or wipe memory
rename-command FLUSHALL ""
rename-command FLUSHDB  ""
rename-command CONFIG   ""
rename-command KEYS     ""
rename-command SHUTDOWN "SYSADMIN_SHUTDOWN_98234"
rename-command DEBUG    ""
Security Advisory: Leaving Redis accessible on public IP addresses (0.0.0.0) without password protection is a critical vulnerability. Threat actors scan port 6379 continuously to exploit Redis via rogue modules, write unauthorized SSH public keys to the filesystem, or execute cryptocurrency miners. Always set
protected-mode yes, restrict binds to localhost/private VPC, configure a 64-characterrequirepass, and rename volatile commands.
Configure Unix Socket Permissions for Web Servers
If your web server (Nginx, Apache, or LiteSpeed) resides on the same physical host or virtual machine as Redis, communicating over a Unix domain socket reduces request latency by approximately 25% to 40% compared to TCP loopback (127.0.0.1:6379) by eliminating TCP connection establishment, packet headers, and loopback kernel socket routing.
Add your web server user (such as www-data or nobody) to the redis group:
# Add web server user to the redis group
sudo usermod -aG redis www-data

# Ensure runtime directory permissions permit socket creation
sudo mkdir -p /var/run/redis
sudo chown -R redis:redis /var/run/redis
sudo chmod 770 /var/run/redis

# Restart Redis to apply changes
sudo systemctl restart redis-server
sudo systemctl status redis-server
Step 4: Systemd Service Limit Overrides
Linux distributions limit the number of open file descriptors and concurrent processes per service. Redis requires high file descriptor limits to handle thousands of concurrent client connections without dropping sockets.
Create a systemd service drop-in override:
# Create directory for systemd override
sudo mkdir -p /etc/systemd/system/redis-server.service.d/

# Write file descriptor and resource overrides
cat << 'EOF' | sudo tee /etc/systemd/system/redis-server.service.d/override.conf
[Service]
LimitNOFILE=65536
LimitNPROC=65536
EOF

# Reload systemd and restart service
sudo systemctl daemon-reload
sudo systemctl restart redis-server
Step 5: Web Application and CMS Integration
Once your Redis cache server is tuned and running, integrate it with your web application layer to intercept expensive queries and store compiled objects.
1. PHP and WordPress Object Cache Integration
Install the native PHP Redis extension for maximum C-level execution speed:
sudo apt-get install -y php-redis
# Or via PECL: pecl install redis
sudo systemctl restart php8.3-fpm
For WordPress installations, install the Redis Object Cache plugin (or LiteSpeed Cache Object Cache module). Configure wp-config.php to communicate over the Unix domain socket for lowest latency:
// wp-config.php - Redis Object Cache Configuration
define('WP_REDIS_SCHEME', 'unix');
define('WP_REDIS_PATH', '/var/run/redis/redis-server.sock');
define('WP_REDIS_PASSWORD', '9f4a8b72c3d1e6f5a0b9c8d7e6f5a4b3c2d1e0f9a8b7c6d5e4f3a2b1c0d9e8f7');
define('WP_REDIS_DATABASE', 0);
define('WP_REDIS_TIMEOUT', 1);
define('WP_REDIS_READ_TIMEOUT', 1);
define('WP_CACHE_KEY_SALT', 'cpanelfree_prod_');
define('WP_REDIS_MAXTTL', 86400);
2. Python and Node.js Connection Pooling
When connecting microservices written in Node.js or Python to Redis, always initialize a persistent connection pool rather than opening and closing sockets per request:
// Node.js ioredis Connection with Retry Strategy and Sockets
const Redis = require('ioredis');

const redis = new Redis({
  path: '/var/run/redis/redis-server.sock',
  password: '9f4a8b72c3d1e6f5a0b9c8d7e6f5a4b3c2d1e0f9a8b7c6d5e4f3a2b1c0d9e8f7',
  maxRetriesPerRequest: 3,
  enableReadyCheck: true,
  lazyConnect: false,
  retryStrategy(times) {
    const delay = Math.min(times * 50, 2000);
    return delay;
  }
});

redis.on('connect', () => {
  console.log('Secure Redis Unix Socket connection established.');
});
When managing enterprise web applications with high concurrency, pairing an optimized Redis cache server with high-performance bare metal or dedicated virtual instances delivers unbeatable responsiveness. For production environments requiring dedicated resource allocation, zero noisy-neighbor interference, and predictable hosting expenses, deploying on MeraHost Enterprise Cloud guarantees LiteSpeed Web Server optimization, blazing-fast NVMe storage arrays, and perpetual price lock protection with Same Renewal Price, Always.
Step 6: Production Benchmarks and Diagnostic Monitoring
Validate your configuration and measure throughput using the native redis-benchmark utility. This tests pipeline efficiency, command latency, and concurrency under simulated stress.
# Benchmark 100,000 requests across 50 concurrent clients via Unix socket
redis-benchmark -s /var/run/redis/redis-server.sock -a 9f4a8b72c3d1e6f5a0b9c8d7e6f5a4b3c2d1e0f9a8b7c6d5e4f3a2b1c0d9e8f7 -q -n 100000 -c 50 -P 16
On tuned enterprise Linux infrastructure, pipeline operations (-P 16) typically achieve between 350,000 and 650,000 requests per second with 99.9th percentile latencies under 0.3 milliseconds.
Essential Diagnostic Commands
Monitor your active Redis instance using these real-time CLI commands:
# Inspect real-time memory usage and fragmentation ratio
redis-cli -a <password> info memory

# Check cache hit/miss ratio (hits / (hits + misses))
redis-cli -a <password> info stats | grep -E "keyspace_hits|keyspace_misses"

# Measure continuous latency anomalies
redis-cli -a <password> --latency-history

# Identify slow queries exceeding the execution threshold
redis-cli -a <password> slowlog get 10
Operational Metric: Keep an eye on
mem_fragmentation_ratioininfo memory. A healthy ratio sits between 1.05 and 1.40. If the ratio climbs above 1.70, memory allocator fragmentation is occurring, indicating that Redis should run an active memory defragmentation pass (activedefrag yesinredis.conf).
Frequently Asked Questions
Why does Redis report a critical warning about Transparent Huge Pages (THP)?
Transparent Huge Pages (THP) group standard 4KB physical pages into 2MB blocks. When Redis forks during background tasks or memory snapshots, copy-on-write modifies single keys, forcing the Linux kernel to allocate and copy full 2MB pages. This leads to massive memory inflation and introduces latency spikes of 30ms to 80ms. Disabling THP via systemd restores microsecond-level determinism.
Should I enable RDB snapshots or AOF persistence if Redis is used purely as a cache?
No. When Redis acts strictly as an ephemeral cache for database query results and compiled sessions, disk persistence introduces unnecessary storage I/O write amplification, fork latency overhead, and NVMe wear. Disabling RDB (save "") and AOF (appendonly no) frees system memory and allows Redis to operate purely as an ultra-fast in-memory cache.
What is the latency advantage of Unix domain sockets over TCP loopback?
Unix domain sockets bypass the kernel’s network stack entirely, avoiding TCP handshake overhead, checksum calculations, packet header encapsulation, and loopback routing. For web applications hosted on the same server as Redis, Unix sockets typically improve throughput by 25% to 40% and shave 0.3ms to 0.7ms off individual request latencies.
Which maxmemory-policy should I choose for web application caching?
For standard web caching (such as WordPress object caching, API responses, and HTML fragments), allkeys-lru (Least Recently Used) is the industry standard. It automatically evicts the oldest, least accessed keys when memory reaches the maxmemory threshold. If your Redis instance mixes persistent user sessions with transient caches, consider volatile-lru and set TTLs strictly on cache objects.
Deploy Enterprise-Grade Production Infrastructure
Need guaranteed performance with zero price hikes? Host mission-critical workloads on MeraHost with pure Enterprise NVMe, LiteSpeed Web Server, and Same Renewal Price, Always (starting at ₹99/mo).