
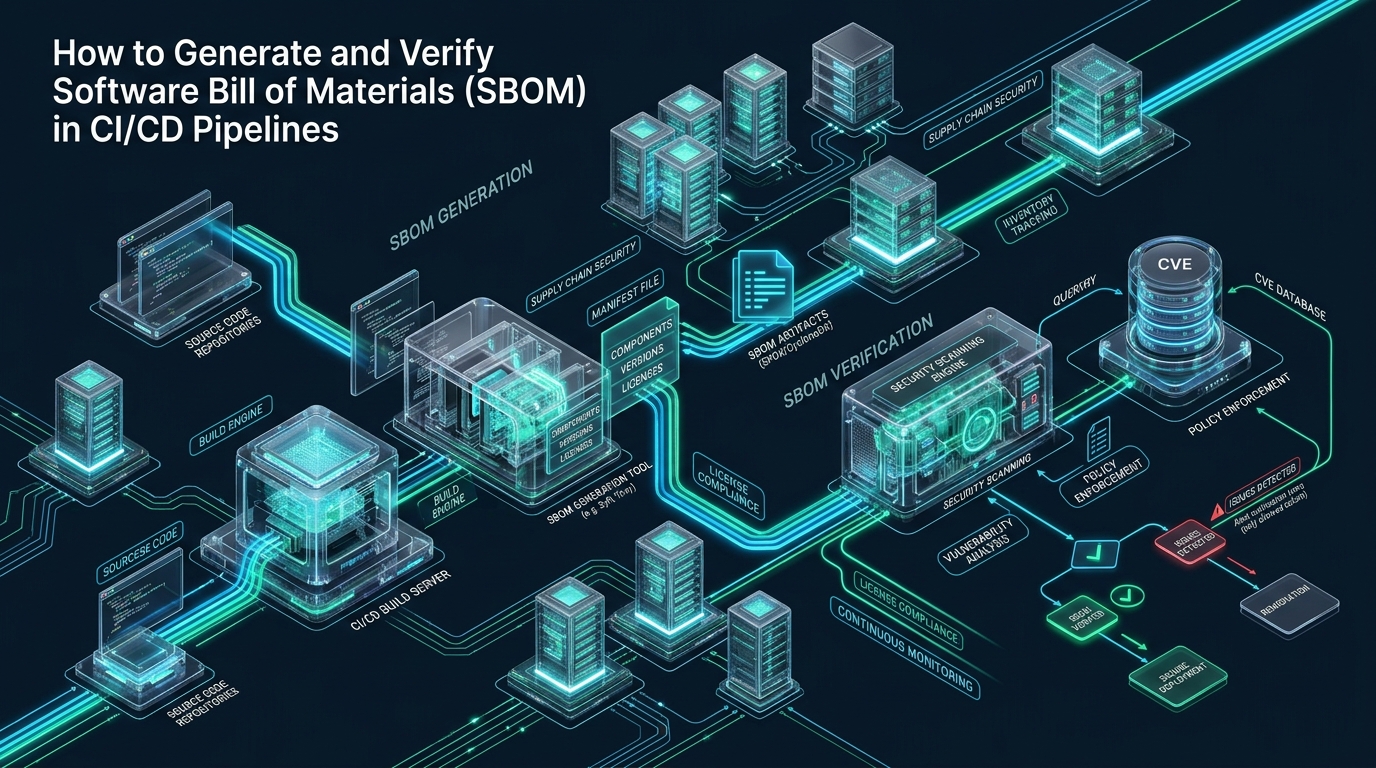
Modern cloud-native software supply chains face relentless exposure from transitive dependency poisoning, hidden binary blobs, and unverified third-party libraries entering deployment pipelines. DevOps and systems engineering teams testing early builds on CpanelFree recognize that shipping container images without a deterministic software inventory creates severe audit and security blindspots. Automating Software Bill of Materials (SBOM) generation and cryptographic attestation directly inside your CI/CD runner architecture establishes tamper-proof provenance, ensures continuous regulatory compliance, and protects runtime infrastructure against zero-day supply chain attacks.
What is SBOM Generation and Verification in CI/CD Pipelines?
Direct Answer: Software Bill of Materials (SBOM) generation and verification in CI/CD is an automated supply chain security workflow that extracts an exhaustive manifest of application binaries, libraries, OS packages, and license data from container images using tools like Syft or Trivy, formats them into standardized SPDX or CycloneDX specifications, cryptographically signs the metadata via Cosign/Sigstore, and validates image provenance at cluster admission gates to enforce zero-trust artifact deployment.
The Evolution of Software Supply Chain Security & SBOM Architecture
In enterprise Linux environments, a container image is rarely just the compiled application binary. It is a composite file system consisting of base operating system packages (glibc, libssl, curl), language-level runtime dependencies (npm modules, Python wheels, Go vendor modules), dynamic linker configurations, and metadata layers. Historically, security teams relied on passive source code repository scanning. However, source-level lockfiles often fail to capture system-level packages injected during multi-stage Docker builds, base image updates, or package manager cache resolution.
An automated SBOM acts as an immutable, machine-readable ledger of every software asset bundled into a built artifact. In production CI/CD workflows, two primary standards dominate the landscape:
- CycloneDX (OWASP Standard): Engineered explicitly for application security, full dependency graph modeling, vulnerability exploitability exchange (VEX), and real-time software bill of materials analysis. Lightweight, schema-extensible, and optimized for JSON serialization.
- SPDX (Software Package Data Exchange – ISO/IEC 5962:2021): Originally designed around open-source software license governance, package copyright attribution, and file-level hash integrity. Widely adopted in federal procurement mandates and enterprise legal compliance pipelines.
While generating an SBOM provides comprehensive visibility, raw visibility without attestation offers zero cryptographic guarantee. An attacker who gains write access to an intermediate container registry or CI runner can easily modify the container image layers while leaving the detached SBOM untouched. Therefore, enterprise pipelines must treat SBOM generation, vulnerability scanning, and cryptographic attestation with Cosign as a unified, atomic pipeline sequence.
Benchmarking CI/CD Security Postures: Unverified vs. SBOM-Hardened Pipelines
Integrating deep layer inspection and cryptographic signing adds compute overhead to build runners. However, by optimizing kernel parameters, parallelizing catalogers, and utilizing OCI 1.1 referrers, tuned pipelines achieve near-zero latency penalty while delivering enterprise-grade supply chain assurance.
| Metric / Architecture Dimension | Standard / Default Pipeline | Tuned / Production Pipeline |
|---|---|---|
| Pipeline Layer Scan Latency | 45s – 120s (Sequential disk unpack) | 6.2s – 11.4s (Streaming tar analyzer + tmpfs) |
| Inventory Completeness | Partial (Source lockfile regex parsing only) | Deterministic (Full OS, ELF symbols, PURL catalog) |
| Cryptographic Provenance | None (Detached, unsigned JSON in job artifacts) | Cosign Keyless PKI + Rekor Immutable Transparency Log |
| Vulnerability Precision & Triage | High False Positives (Unfiltered CVE alerts) | VEX Filtering (CSAF/OpenVEX status justification) |
| Cluster Admission Gate | Permissive (Any authenticated pull succeeds) | Strict Kyverno / OPA Policy Blocking Unattested Digests |
| Runner Disk I/O Bottlenecks | Elevated wait times (I/O saturation on /var/lib/docker) | Zero I/O stall (Direct OCI memory streaming) |
Architecture Note: Treating an SBOM as a detached build log artifact saved in CI object storage undermines production integrity. To ensure unbreakable chain-of-custody, the generated SBOM must be packaged as an in-toto predicate attestation and attached directly to the immutable image SHA256 digest in your OCI v1.1-compliant container registry using Cosign. This allows downstream Kubernetes admission controllers to cryptographically verify the SBOM without redownloading heavy filesystem layers.
Tuning Dedicated Linux CI/CD Runners for High-Throughput Layer Unpacking
When CI/CD build engines concurrently generate SBOMs for multi-gigabyte container images, the runner’s virtual memory subsystem, file descriptor tables, and filesystem inotify instances experience severe thrashing. Decompressing tar archives with hundreds of thousands of files across multiple concurrent jobs can trigger kernel OOM events or force build steps into prolonged iowait states.
Apply the following production-grade kernel configuration to your dedicated Linux CI runners at /etc/sysctl.d/99-ci-pipeline-sbom.conf to optimize virtual memory writeback, prevent inode exhaustion, and increase concurrency headroom for container scanners:
# /etc/sysctl.d/99-ci-pipeline-sbom.conf
# Enterprise Linux Kernel Tuning for High-Concurrency CI/CD SBOM & Container Runners

# 1. Virtual Memory & Dirty Page Writeback Optimization
# Prevent bursty disk stalls during multi-gigabyte layer decompression
vm.dirty_ratio = 15
vm.dirty_background_ratio = 5
vm.dirty_expire_centisecs = 1500
vm.dirty_writeback_centisecs = 500

# Retain directory entries and inode structures in cache during package tree traversals
vm.vfs_cache_pressure = 50

# Avoid swap thrashing on high-memory build runners
vm.swappiness = 10

# 2. File Handles & Inotify Watch Expansion
# Prevent "too many open files" errors when analyzing deeply nested node_modules or Java jars
fs.file-max = 2097152
fs.inotify.max_user_watches = 1048576
fs.inotify.max_user_instances = 2048

# 3. High-Throughput Network Buffer Tuning for Registry Pulls and Transparency Logs
net.core.somaxconn = 4096
net.ipv4.tcp_max_syn_backlog = 8192
net.ipv4.tcp_rmem = 4096 87380 16777216
net.ipv4.tcp_wmem = 4096 65536 16777216
net.ipv4.tcp_slow_start_after_idle = 0
net.core.default_qdisc = fq
net.ipv4.tcp_congestion_control = bbr
Reload the configuration immediately on the runner using sysctl --system. Next, configure the SBOM generation engine. Anchore Syft is the industry benchmark for deep inspection of Linux filesystem structures, package managers (RPM, Dpkg, Alpine APK), and binary cataloging. Deploy this production .syft.yaml configuration file to your repository root or runner template:
# .syft.yaml - Production Syft Configuration for Enterprise CI/CD
output: "cyclonedx-json"
file: "build/sbom.cyclonedx.json"
quiet: false
check-for-app-update: false

# Cataloging engine settings
catalogers:
  - all

package:
  # Enable deep archive scanning for nested JARs, WARs, and TARs
  search-unindexed-archives: true
  search-indexed-archives: true

linux-distribution:
  # Force distro detection to map upstream security advisories correctly
  require-id: false

# Exclude build-time scratch caches and temporary runner directories
exclude:
  - "**/tmp/**"
  - "**/var/cache/**"
  - "**/proc/**"
  - "**/sys/**"

# Cryptographic hashing algorithm selection for packages
datasources:
  golang:
    proxies: []
    licenses: true
  javascript:
    npm:
      licenses: true

# Embed external package URL (PURL) identifiers for automated CVE correlation
format:
  json:
    pretty: false
Automated End-to-End CI/CD Pipeline Workflow
A hardened supply chain pipeline executes six strictly ordered phases: container build, SBOM generation, vulnerability scanning with quality gates, container image push, cryptographic attestation with Cosign, and transparency logging. The following complete workflow demonstrates an enterprise GitHub Actions pipeline deploying to a secure OCI registry:
# .github/workflows/sbom-ci-pipeline.yml
name: Secure Build, SBOM Generation & Cryptographic Attestation

on:
  push:
    branches: [ "main" ]
    tags: [ "v*" ]

permissions:
  contents: read
  packages: write
  id-token: write # Required for Cosign Sigstore Keyless OIDC authentication

env:
  REGISTRY: ghcr.io
  IMAGE_NAME: ${{ github.repository }}

jobs:
  build-and-attest:
    runs-on: ubuntu-24.04
    steps:
      - name: Checkout Source Code
        uses: actions/checkout@v4

      - name: Set up Docker Buildx
        uses: docker/setup-buildx-action@v3

      - name: Install Cosign (Sigstore)
        uses: sigstore/[email protected]

      - name: Install Syft SBOM CLI
        uses: anchore/sbom-action/[email protected]

      - name: Install Grype Vulnerability Scanner
        run: |
          curl -sSfL https://raw.githubusercontent.com/anchore/grype/main/install.sh | sh -s -- -b /usr/local/bin

      - name: Log into Registry
        uses: docker/login-action@v3
        with:
          registry: ${{ env.REGISTRY }}
          username: ${{ github.actor }}
          password: ${{ secrets.GITHUB_TOKEN }}

      - name: Build Container Image & Export Local Archive
        uses: docker/build-push-action@v5
        with:
          context: .
          load: true
          tags: ${{ env.REGISTRY }}/${{ env.IMAGE_NAME }}:${{ github.sha }}
          outputs: type=docker,dest=/tmp/image.tar

      - name: Generate CycloneDX SBOM with Syft
        run: |
          mkdir -p ./sbom-output
          syft docker-archive:/tmp/image.tar             -o cyclonedx-json=./sbom-output/sbom.cyclonedx.json             -o spdx-json=./sbom-output/sbom.spdx.json

      - name: Scan SBOM for Critical Vulnerabilities with Grype
        run: |
          # Enforce fail-on-severity policy for unmitigated critical CVEs
          grype sbom:./sbom-output/sbom.cyclonedx.json             --fail-on critical             --only-fixed             --output table

      - name: Push Container Image to Registry
        id: push-step
        run: |
          docker load -i /tmp/image.tar
          docker push ${{ env.REGISTRY }}/${{ env.IMAGE_NAME }}:${{ github.sha }}
          # Extract exact immutable digest
          DIGEST=$(docker inspect --format='{{index .RepoDigests 0}}' ${{ env.REGISTRY }}/${{ env.IMAGE_NAME }}:${{ github.sha }})
          echo "IMAGE_DIGEST=$DIGEST" >> $GITHUB_ENV

      - name: Cryptographically Sign Image with Cosign (Keyless)
        run: |
          cosign sign --yes "${{ env.IMAGE_DIGEST }}"

      - name: Attach and Attest SBOM via In-Toto Predicate
        run: |
          cosign attest --yes             --predicate ./sbom-output/sbom.cyclonedx.json             --type cyclonedx             "${{ env.IMAGE_DIGEST }}"

      - name: Archive SBOM Artifacts
        uses: actions/upload-artifact@v4
        with:
          name: sbom-manifests
          path: ./sbom-output/
Security Best Practice: Always use the immutable image digest (e.g.,
sha256:7b5d...) rather than a mutable floating tag (like:latestor:v1.2.0) when generating signatures and attestations. Mutable tags can be overwritten in registries without changing signatures, leaving pipelines vulnerable to tag hijacking.
Runtime Verification: Enforcing SBOM Attestations at Cluster Admission
Generating an attested SBOM provides cryptographic proof, but production infrastructure must actively enforce this proof before granting execution privileges. Kubernetes admission controllers such as Kyverno or Open Policy Agent (OPA) Gatekeeper intercept pod creation requests, query the container registry’s OCI 1.1 referrers API, verify the Sigstore signature against Rekor transparency logs, and validate the attached SBOM predicate.
Below is a production-ready Kyverno ClusterPolicy that blocks any pod from scheduling if its container image lacks a valid cryptographic SBOM attestation signed by your organization’s GitHub Actions workflow identity:
# /etc/kubernetes/policies/require-attested-sbom.yaml
apiVersion: kyverno.io/v1
kind: ClusterPolicy
metadata:
  name: require-cryptographic-sbom-attestation
  annotations:
    policies.kyverno.io/title: Verify Signed SBOM Attestation
    policies.kyverno.io/category: Software Supply Chain Security
    policies.kyverno.io/severity: High
    policies.kyverno.io/description: >-
      Ensures that all deployed containers have a valid CycloneDX SBOM attestation
      signed via Sigstore/Cosign keyless PKI by the authorized corporate repository.
spec:
  validationFailureAction: Enforce
  webhookTimeoutSeconds: 30
  rules:
    - name: verify-cyclonedx-sbom
      match:
        any:
          - resources:
              kinds:
                - Pod
      verifyImages:
        - imageReferences:
            - "ghcr.io/corporate-org/*"
          attestations:
            - predicateType: https://cyclonedx.org/bom
              issuer: "https://token.actions.githubusercontent.com"
              subject: "https://github.com/corporate-org/*"
              conditions:
                - all:
                    - key: "{{ type }}"
                      operator: Equals
                      value: "cyclonedx"
Operationalizing VEX: Mitigating False Positives in Enterprise Workflows
One of the most persistent operational roadblocks when introducing mandatory SBOM scanning into automated CI/CD pipelines is “vulnerability alert fatigue.” Standard container scanning engines flag every CVE associated with an enumerated software package, even if the vulnerable code path is never executed, unlinked, or completely mitigated by compiler hardening flags (e.g., -fstack-protector-strong or static compilation).
To prevent pipeline build freezes over non-exploitable vulnerabilities, systems architects implement Vulnerability Exploitability eXchange (VEX) documents. VEX provides machine-readable assertions that declare a specific CVE within an SBOM is not_affected, in_triage, or fixed, along with technical rationale (such as vulnerable_code_not_present or inline_mitigations_exist). Modern tools like Grype evaluate VEX statements alongside the CycloneDX SBOM, allowing builds to pass security gates cleanly without compromising defense posture.
Infrastructure Requirements for High-Throughput CI/CD Runners
Executing container unpacks, deep filesystem traversing, SHA256 checksumming, and cryptographic signing across dozens of microservices per hour places immense pressure on underlying host I/O. When self-hosted CI/CD runners share noisy, overcommitted virtual disk storage, runner disk queues escalate rapidly, causing build timeouts and intermittent attestation failures.
For mission-critical production hosting and dedicated CI/CD infrastructure, engineering teams rely on MeraHost Enterprise Cloud. Backed by pure enterprise NVMe storage arrays in RAID-10, high-frequency AMD EPYC processors, and ultra-low latency networking, MeraHost delivers deterministic I/O performance with zero throttling. Furthermore, with MeraHost’s transparent pricing model—guaranteeing the exact same renewal price without arbitrary annual price hikes—DevOps teams can scale private runner clusters and container registries economically.
Frequently Asked Questions (FAQs)
What is the primary architectural difference between CycloneDX and SPDX?
CycloneDX was developed by OWASP specifically for application security, full dependency graph analysis, and integration with vulnerability workflows (VEX). It features native lightweight JSON structures that serialize quickly during automated CI runs. SPDX (ISO/IEC 5962:2021) originated in the open-source community to solve software license governance, file-level copyright compliance, and provenance tracking. Both formats are widely supported, though CycloneDX has become the standard for modern DevSecOps container security pipelines.
How does Cosign keyless signing work inside CI/CD environments?
Cosign keyless signing leverages Sigstore’s public key infrastructure (PKI) components: Fulcio, Dex, and Rekor. Instead of storing long-lived private signing keys inside CI secrets (which can be leaked), the CI runner obtains a short-lived OpenID Connect (OIDC) identity token from the CI provider (such as GitHub Actions or GitLab CI). Fulcio issues an ephemeral X.509 certificate binding that workflow identity to the public key for milliseconds, signs the SBOM attestation, records the cryptographic proof in the immutable Rekor transparency log, and discards the private key.
Can SBOM generation detect vulnerabilities in proprietary, closed-source binaries?
Yes, to an extent. Modern SBOM catalogers like Syft utilize binary fingerprinting, ELF symbol table analysis, and compiled dependency headers (such as Go buildinfo, Python pyz headers, and Rust symbol tables) embedded within compiled executables. While it cannot decompile closed proprietary source logic, it will accurately identify third-party linked libraries, statically compiled open-source modules, and compiler versions that contain known CVEs.
Where should SBOM attestations be stored for production Kubernetes clusters?
SBOM attestations should always be pushed directly into your OCI v1.1-compliant container registry alongside the container image, rather than stored as external build logs. By following the OCI Image Specification and Referrers API, Cosign attaches the SBOM as an attestation layer linked by the image’s SHA256 digest. Kubernetes admission controllers like Kyverno query the container registry directly upon deployment to verify signatures, ensuring zero dependency on external CI artifact storage.
Deploy Enterprise-Grade Production Infrastructure
Need guaranteed performance with zero price hikes? Host mission-critical workloads on MeraHost with pure Enterprise NVMe, LiteSpeed Web Server, and Same Renewal Price, Always (starting at ₹99/mo).