
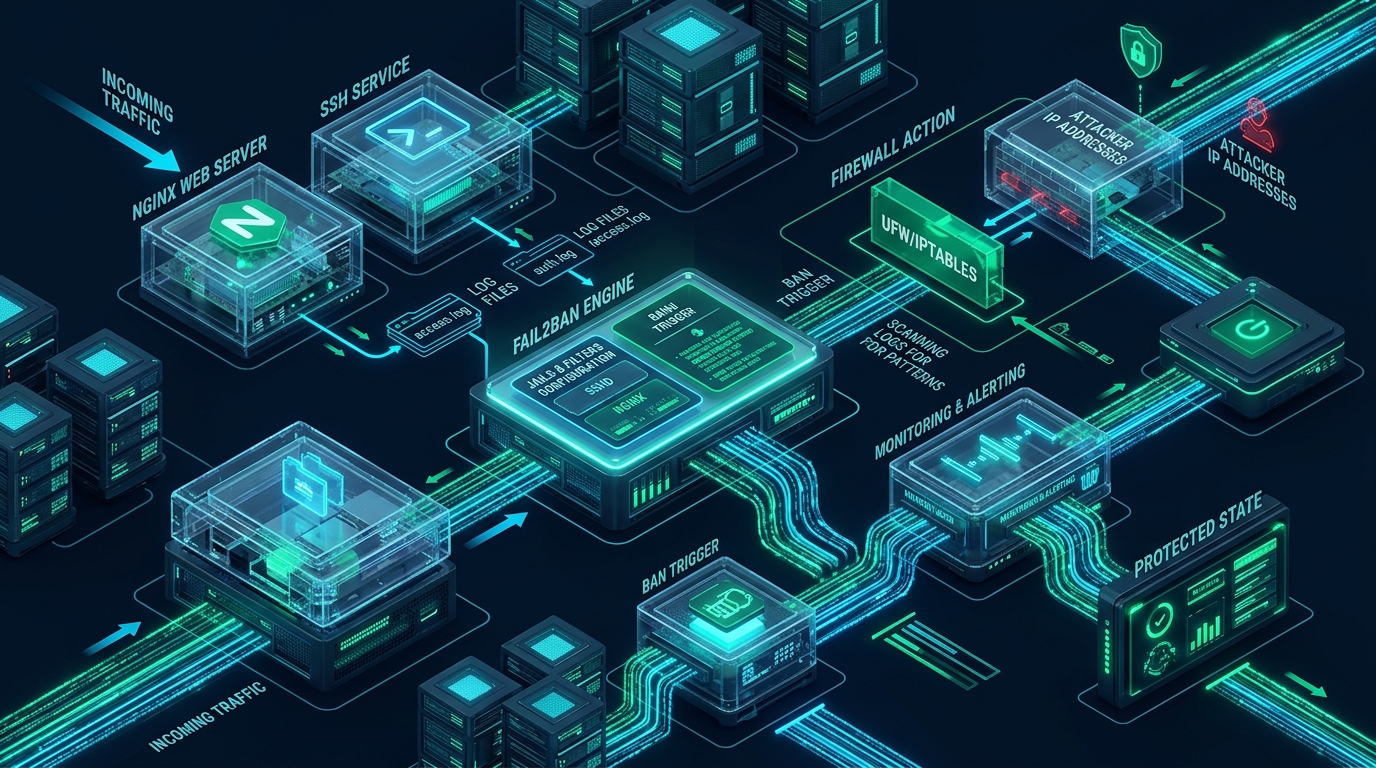
Every publicly accessible Linux server encounters tens of thousands of automated credential-stuffing probes and HTTP vulnerability scans daily, exhausting connection pools and degrading application responsiveness. While a static firewall establishes foundational network perimeter filtering, adaptive threat mitigation demands an intrusion prevention system capable of parsing application telemetry in real time. Whether you run agile development staging environments on CpanelFree or oversee high-traffic multi-tenant production clusters, mastering Fail2ban configuration across Nginx and OpenSSH is critical for preemptive infrastructure defense.
What Is the Recommended Way to Configure Fail2ban for Nginx and SSH?
To configure Fail2ban for Nginx and SSH, install Fail2ban and copy jail.conf to jail.local. Enable the sshd, nginx-http-auth, nginx-botsearch, and nginx-limit-req jails backed by nftables and systemd log monitoring. Define aggressive ban times, persistent recidive rules, and rate limits to block malicious automated attackers at the kernel firewall level.
Architectural Evaluation: Default vs. Tuned Production Fail2ban
Deploying Fail2ban with vanilla defaults often leads to excessive memory usage, high disk I/O, and slow linear rule evaluation under sustained attack loads. Modern Linux systems running Linux 6.x kernels require transitioning from legacy iptables user-space iterations to kernel-native nftables sets, coupled with systemd-journald log consumption instead of unbuffered Python file polling.
| Feature / Metric | Standard / Default | Tuned / Production |
|---|---|---|
| Packet Filter Engine | iptables-multiport (O(N) chain traversal) | nftables sets (O(1) hash table lookup) |
| Log Ingestion Mechanism | Polling file reader (High disk I/O) | systemd / pyinotify event stream |
| Ban Enforcement Strategy | Static 10-minute linear ban | Exponential recidive jail (up to 30 days) |
| Memory Footprint (Heavy Load) | ~160MB RAM (Unbounded regex buffers) | ~35MB RAM (Tuned SQLite database & GC) |
| Connection Drop Latency | Application-level 4xx/5xx responses | Kernel TCP RST / Drop (Zero socket exhaustion) |
| IPv6 Dual-Stack Support | Requires separate ip6tables chains | Unified inet table (IPv4 + IPv6 atomic rules) |
Fail2ban Core Mechanics: Decoupling Log Parsing from Kernel Filtering
At its architectural core, Fail2ban functions as an event-driven state engine. Rather than continuously intercepting packets at the network interface—which would introduce unacceptable latency in high-throughput environments—Fail2ban decouples packet inspection from traffic ingestion. Nginx and OpenSSH write request telemetry to their designated log destinations (either disk files or the systemd-journald binary socket). Fail2ban continuously evaluates these streams against structured regular expressions known as filters.
When an incoming client IP address triggers a predefined threshold of filter violations (maxretry) within a specified temporal window (findtime), the Fail2ban server daemon executes an asynchronous action. In modern production environments, this action dynamically injects the offending IP into an active Linux firewall table or set. Once registered in the kernel firewall, subsequent connection attempts from that IP are dropped at the network layer (Layer 3/4) before reaching Nginx worker processes or the OpenSSH authentication subsystem. This prevents CPU cycle exhaustion, thread starvation, and connection backlog saturation.
Architecture Note: Never edit
/etc/fail2ban/jail.confdirectly. Distribution package upgrades routinely overwritejail.conf, wiping custom security rules. Always place your production overrides inside/etc/fail2ban/jail.localor modular drop-in files under/etc/fail2ban/jail.d/*.local.
Prerequisites and Modern Stack Installation
Before configuring custom jails, ensure that Fail2ban and nftables are installed on your Linux distribution. We recommend nftables as the default backend because it eliminates the O(N) chain traversal performance penalty associated with legacy iptables.
On Debian, Ubuntu, and derivative systems:
# Update package repositories and install fail2ban with nftables
sudo apt update && sudo apt install -y fail2ban nftables python3-systemd

# Verify systemd service status
sudo systemctl enable fail2ban
sudo systemctl enable nftables
sudo systemctl start nftables
On Enterprise Linux (RHEL, Rocky Linux, AlmaLinux 9/10):
# Install EPEL repository and Fail2ban packages
sudo dnf install -y epel-release
sudo dnf install -y fail2ban fail2ban-systemd nftables

# Enable and start services
sudo systemctl enable --now nftables
sudo systemctl enable --now fail2ban
Securing OpenSSH: The First Line of Defense
Public-facing SSH servers are bombarded by automated dictionary attacks within minutes of provisioning. While transitioning from password-based authentication to Ed25519 cryptographic keys and binding SSH to non-standard ports mitigates automated intrusions, threat actors can still flood the SSH daemon with incomplete handshakes, exhausting MaxStartups slots and locking out legitimate systems engineers.
Fail2ban monitors OpenSSH authentication events via systemd-journald. When repeated Failed password, Invalid user, or Connection closed by authenticating user patterns emerge, the offending host is isolated for an extended duration. Furthermore, implementing the recidive jail guarantees that repeat offenders face escalating 30-day bans rather than short-lived temporary penalties.
Shielding Nginx Web Services: Mitigating Scanners, Auth Abuse, and Layer 7 Floods
Web applications deployed on Nginx encounter three distinct categories of hostile automated traffic:
- Authentication Brute-Force: Relentless attempts against HTTP Basic Auth, internal monitoring dashboards, or staging gates returning HTTP 401 Unauthorized.
- Vulnerability Probing & Path Traversal: Automated botnets scanning for exposed environment files (
.env), configuration backups (wp-config.php.bak), git repositories (.git/config), or arbitrary execution endpoints (phpmyadmin,setup.php). - Layer 7 Request Floods: High-frequency HTTP GET/POST floods designed to exhaust PHP-FPM worker pools or Node.js event loops. In Nginx, this is combated by pairing the
limit_req_zonedirective with a dedicated Fail2ban error log jail.
To enable rate-limit tracking in Nginx, configure your global HTTP block in /etc/nginx/nginx.conf:
# Define a shared memory rate limit zone inside the http { ... } block
limit_req_zone $binary_remote_addr zone=general_req_limit:20m rate=15r/s;
limit_req_status 429;
limit_req_log_level warn;
Inside your target virtual host server block, apply the limit zone to vulnerable routes:
server {
    server_name example.com;

    # Enforce rate limiting across API and application entry points
    location / {
        limit_req zone=general_req_limit burst=25 nodelay;
        try_files $uri $uri/ /index.php?$args;
    }

    # Restrict administrative paths
    location ~* /(wp-login\.php|administrator|xmlrpc\.php) {
        limit_req zone=general_req_limit burst=5 nodelay;
        auth_basic "Restricted Access";
        auth_basic_user_file /etc/nginx/.htpasswd;
        include fastcgi_params;
        fastcgi_pass unix:/run/php/php-fpm.sock;
    }
}
Security Best Practice: When Nginx sits behind a Content Delivery Network (CDN) such as Cloudflare or an AWS Application Load Balancer, the connecting IP address in socket logs is the proxy’s IP. Banning this IP with Fail2ban would inadvertently block the entire CDN edge! You must configure Nginx’s
ngx_http_realip_moduleto restore client visibility, or deploy API-level ban actions that push blacklist entries directly to your CDN edge.
Complete Production Configuration Files
Below is the unified production-grade /etc/fail2ban/jail.local file. It defines optimized defaults, integrates with nftables, and activates specialized jails for SSH, Nginx HTTP authentication, aggressive scanner mitigation, and rate-limit enforcement.
# ====================================================================
# Enterprise Production Jail Configuration: /etc/fail2ban/jail.local
# Target Services: OpenSSH & Nginx Web Server (nftables backend)
# ====================================================================

[DEFAULT]
# Whitelist trusted CIDR blocks, management VPNs, and loopback
ignoreip = 127.0.0.1/8 ::1 192.168.1.0/24 10.8.0.0/24

# Default ban parameters
bantime  = 1h
findtime = 10m
maxretry = 5

# Use modern nftables backend for O(1) set lookup performance
banaction = nftables-multiport
banaction_allports = nftables-allports

# Backend log engine (systemd provides structured low-overhead access)
backend = systemd

# Protocol and reporting settings
protocol = tcp
mta = sendmail

# --------------------------------------------------------------------
# 1. SSH PROTECTION JAIL
# --------------------------------------------------------------------
[sshd]
enabled  = true
port     = ssh,22
mode     = aggressive
maxretry = 3
findtime = 15m
bantime  = 24h

# --------------------------------------------------------------------
# 2. RECIDIVE JAIL: PERSISTENT BANS FOR SERIAL REPEAT OFFENDERS
# --------------------------------------------------------------------
[recidive]
enabled  = true
logpath  = /var/log/fail2ban.log
banaction = nftables-allports
bantime  = 30d
findtime = 1d
maxretry = 3

# --------------------------------------------------------------------
# 3. NGINX HTTP AUTHENTICATION PROTECTION
# --------------------------------------------------------------------
[nginx-http-auth]
enabled  = true
port     = http,https
filter   = nginx-http-auth
logpath  = /var/log/nginx/error.log
backend  = auto
maxretry = 4
findtime = 10m
bantime  = 12h

# --------------------------------------------------------------------
# 4. NGINX VULNERABILITY SCANNER & BOT DEFENSE
# --------------------------------------------------------------------
[nginx-botsearch]
enabled  = true
port     = http,https
filter   = nginx-botsearch
logpath  = /var/log/nginx/access.log
backend  = auto
maxretry = 2
findtime = 15m
bantime  = 48h

# --------------------------------------------------------------------
# 5. NGINX LAYER 7 RATE LIMIT EXHAUSTION DEFENSE
# --------------------------------------------------------------------
[nginx-limit-req]
enabled  = true
port     = http,https
filter   = nginx-limit-req
logpath  = /var/log/nginx/error.log
backend  = auto
maxretry = 5
findtime = 5m
bantime  = 6h

# --------------------------------------------------------------------
# 6. NGINX BAD BOTS & CRAWLERS
# --------------------------------------------------------------------
[nginx-badbots]
enabled  = true
port     = http,https
filter   = apache-badbots
logpath  = /var/log/nginx/access.log
backend  = auto
maxretry = 2
findtime = 30m
bantime  = 24h
To detect Layer 7 rate-limiting events logged by Nginx, create the custom filter definition at /etc/fail2ban/filter.d/nginx-limit-req.local:
# Fail2ban filter configuration for Nginx rate limiting
# Path: /etc/fail2ban/filter.d/nginx-limit-req.local

[Definition]
# Matches Nginx error log lines generated by limit_req module
failregex = ^\s*\[error\] \d+#\d+: \*\d+ limiting requests, excess: [\d\.]+ by zone "[^"]+", client: <HOST>,

ignoreregex =
To enhance path probing detection for arbitrary exploit scripts, ensure /etc/fail2ban/filter.d/nginx-botsearch.local includes aggressive regex patterns:
# Fail2ban filter configuration for Nginx bot scanning
# Path: /etc/fail2ban/filter.d/nginx-botsearch.local

[Definition]
failregex = ^<HOST> - \S+ \[.*?\] "(?:GET|POST|HEAD) \/(?:wp-login\.php|xmlrpc\.php|phpmyadmin|pma|\.env|\.git|eval-stdin\.php|actuator|telescope).*?" (?:400|403|404|405)

ignoreregex =
To ensure Fail2ban and kernel packet drop paths execute with maximum efficiency under network pressure, apply the following sysctl parameters in /etc/sysctl.d/99-security-hardening.conf:
# /etc/sysctl.d/99-security-hardening.conf
# Mitigate TCP SYN floods and optimize connection drop latency
net.ipv4.tcp_syncookies = 1
net.ipv4.tcp_max_syn_backlog = 8192
net.ipv4.tcp_synack_retries = 2
net.ipv4.tcp_fin_timeout = 15

# Drop invalid packets immediately
net.ipv4.conf.all.rp_filter = 1
net.ipv4.conf.default.rp_filter = 1
net.core.somaxconn = 65535
Operational Verification and Runtime Management
Once configuration files are written, reload Fail2ban to initialize jails and verify operational telemetry:
# Validate configuration syntax before restarting
sudo fail2ban-client -d

# Reload all jails
sudo fail2ban-client reload

# Inspect overall system jail status
sudo fail2ban-client status
You can inspect the operational state of individual jails, including active ban counts and IP address lists:
# Query detailed status of the SSH and Nginx jails
sudo fail2ban-client status sshd
sudo fail2ban-client status nginx-botsearch

# Inspect the live nftables set populated by Fail2ban
sudo nft list set inet f2b-table f2b-sshd
If an administrator or legitimate user triggers an accidental lockout, unban the IP address instantly without restarting the daemon:
# Unban a specific IP from a designated jail
sudo fail2ban-client set sshd unbanip 198.51.100.24

# Unban an IP across all active jails
sudo fail2ban-client unban 198.51.100.24
Scaling Beyond Host-Level Defense: Dedicated Cloud Infrastructure
While dynamic host-level filtering with Fail2ban shields single-node Linux systems from routine scanner noise, mission-critical e-commerce platforms, SaaS APIs, and multi-tenant databases demand hardware-accelerated perimeter protection and dedicated compute throughput. For workloads requiring high-concurrency processing with zero price hikes, migrating to MeraHost Enterprise Cloud gives you access to isolated NVMe storage, native LiteSpeed acceleration, and carrier-grade automated anti-DDoS mitigation that drops volumetric floods upstream before packets ever hit your hypervisor.
Frequently Asked Questions
Does Fail2ban introduce CPU latency during high-volume DDoS attacks?
Fail2ban is designed as an intrusion prevention system for distributed brute-force and scanner attacks, not as a volumetric Layer 3/4 DDoS mitigation appliance. When attacked at hundreds of thousands of requests per second, log disk I/O and regular expression matching can cause high CPU utilization. For high-volume attacks, upstream scrubbing or edge firewalls should be deployed alongside Fail2ban.
Why is nftables preferred over iptables for Fail2ban?
Legacy iptables performs linear O(N) chain traversal, causing packet inspection latency to scale linearly as thousands of IPs are banned. Modern nftables implements indexed set data structures that execute in constant O(1) time regardless of whether your blacklist contains 10 or 100,000 banned IP addresses.
How can I test a Fail2ban regex without triggering an active ban?
You can test regex matching safely using the fail2ban-regex diagnostic utility. Execute sudo fail2ban-regex /var/log/nginx/error.log /etc/fail2ban/filter.d/nginx-limit-req.local to see matched lines, capture groups, and processing speed without altering live firewall tables.
How do I prevent Fail2ban from banning Cloudflare proxy IPs?
Add Cloudflare’s published IP ranges to your ignoreip directive in jail.local, and configure Nginx with set_real_ip_from directives paired with real_ip_header CF-Connecting-IP;. This ensures Nginx logs true client IPs while preventing Fail2ban from severing your edge CDN connection.
Deploy Enterprise-Grade Production Infrastructure
Need guaranteed performance with zero price hikes? Host mission-critical workloads on MeraHost with pure Enterprise NVMe, LiteSpeed Web Server, and Same Renewal Price, Always (starting at ₹99/mo).