
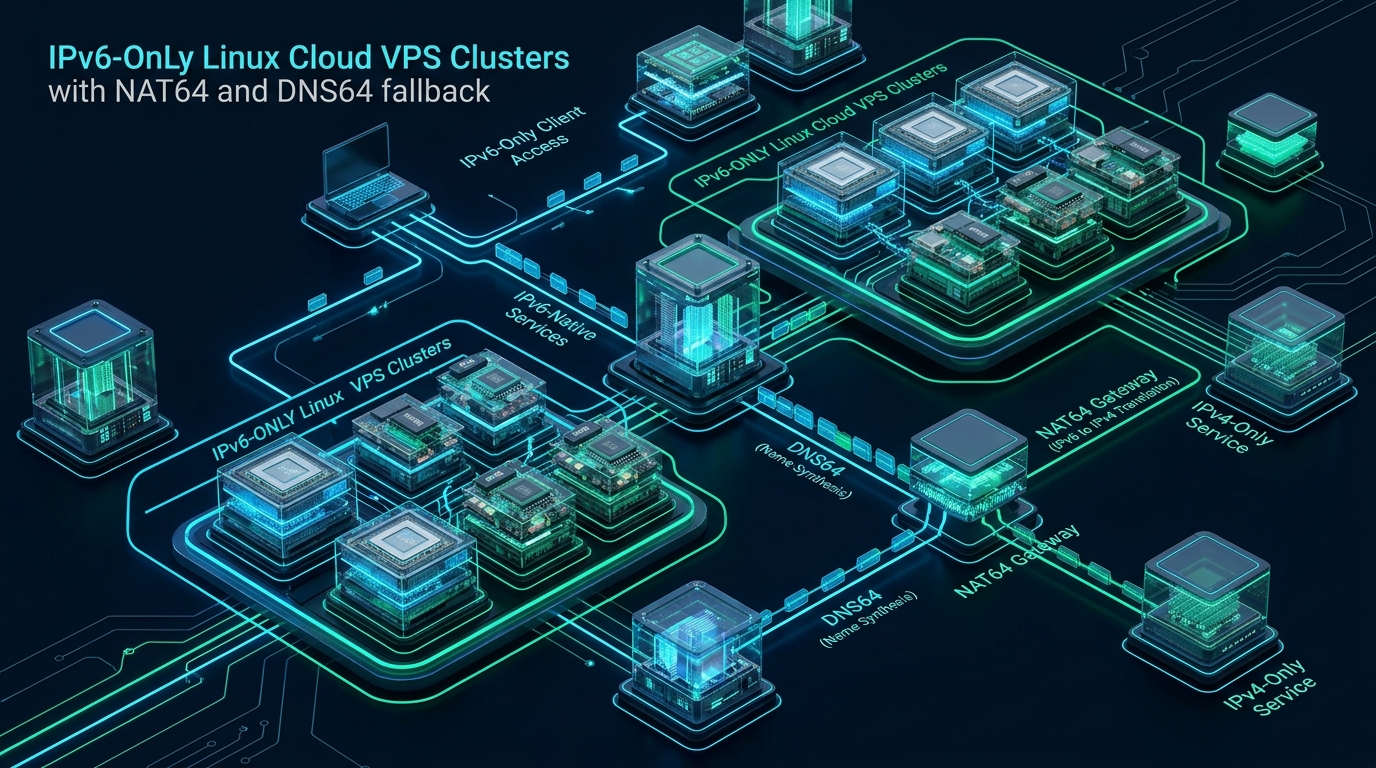
With public IPv4 addresses commanding steep recurring surcharges across hyperscalers and edge providers, modern cloud infrastructure engineering requires an architectural shift toward pure IPv6-only server deployments. Operating single-stack architectures drastically streamlines host routing tables, eliminates dual-stack state overhead, and mitigates complex ARP/ND table contention, but enterprise workloads inevitably require egress access to legacy IPv4 endpoints such as un-migrated package registries, proprietary third-party APIs, and external database mirrors. High-performance hosting platforms like CpanelFree demonstrate that pairing pure IPv6 VPS clusters with high-throughput stateful NAT64 translation and synthetic DNS64 resolution yields uncompromised outbound compatibility without paying the recurring IPv4 address tax.
Understanding IPv6-Only Architecture with NAT64 and DNS64
64:ff9b::/96 prefix) and translating transport-layer packets via an upstream stateful NAT64 gateway running kernel-level Jool or Tayga.
In traditional dual-stack environments, every virtual machine requires two distinct network protocol stacks, two firewall policies (iptables and ip6tables or dual nftables families), and two routing table lookups for every outbound socket. Beyond the financial cost of assigning a dedicated IPv4 address to each node, dual-stack nodes suffer from asymmetric pathing, Happy Eyeballs RFC 8305 latency penalties during connection races, and fragmented security audit logs.
By contrasting dual-stack with an IPv6-only cluster complemented by DNS64 and NAT64, infrastructure teams achieve architectural purity. Every container, virtual machine, and daemon binds exclusively to an IPv6 address. When a local process queries a remote service that lacks native IPv6 AAAA DNS records, the DNS64 resolver intercepts the lookup, requests the legacy IPv4 A record, and prepends the standardized Well-Known Prefix (WKP) 64:ff9b::/96. The client initiates a standard IPv6 TCP or UDP connection toward this synthesized address. When the packets hit the default gateway, the NAT64 translator dynamically rewrites the headers into standard IPv4 packets, mapping them to a shared pool of public IPv4 addresses.
Architectural Comparison: Dual-Stack vs. Pure IPv6 with NAT64/DNS64
Evaluating the trade-offs between dual-stack complexity, legacy IPv4-only configurations with Carrier-Grade NAT (CGNAT), and modern IPv6-only architectures with NAT64/DNS64 clarifies why infrastructure teams are migrating toward single-stack topologies:
/64 subnet per hypervisor or cluster segment. The NAT64 prefix does not need to be routed on the public Internet; it only requires internal routing between your VPS nodes and the NAT64 translation interface. The Well-Known Prefix 64:ff9b::/96 is standard, but enterprise deployments may also use a Network-Specific Prefix (NSP) carved from their own Provider-Independent (PI) IPv6 allocation.Step 1: Production Kernel Optimization for IPv6 VPS Nodes
Before establishing DNS64 and NAT64 routing, the Linux kernel network subsystem must be tuned to handle high-concurrency IPv6 traffic, optimized neighbor discovery caching, and TCP congestion control via BBR. Deploy the following configuration file on every cluster node.
Save the configuration to /etc/sysctl.d/99-ipv6-cluster-optimized.conf:
# /etc/sysctl.d/99-ipv6-cluster-optimized.conf
# Production Linux Kernel Network Hardening for IPv6-Only VPS Clusters

# Enable IPv6 Forwarding (Required on Gateway/Router Nodes, Optional on Worker Nodes)
net.ipv6.conf.all.forwarding = 0
net.ipv6.conf.default.forwarding = 0
net.ipv4.ip_forward = 0

# Disable IPv6 Autoconfiguration (SLAAC) on Static Server Infrastructure
net.ipv6.conf.all.autoconf = 0
net.ipv6.conf.default.autoconf = 0
net.ipv6.conf.all.accept_ra = 0
net.ipv6.conf.default.accept_ra = 0
net.ipv6.conf.all.use_tempaddr = 0
net.ipv6.conf.default.use_tempaddr = 0

# Scale Neighbor Discovery (NDP) Cache Limits for High-Density Microservices
net.ipv6.neigh.default.gc_thresh1 = 1024
net.ipv6.neigh.default.gc_thresh2 = 4096
net.ipv6.neigh.default.gc_thresh3 = 8192
net.ipv6.neigh.default.gc_interval = 30
net.ipv6.neigh.default.gc_stale_time = 60

# TCP Buffer Scaling and BBR Congestion Control
net.core.default_qdisc = fq
net.ipv4.tcp_congestion_control = bbr
net.core.rmem_max = 16777216
net.core.wmem_max = 16777216
net.ipv4.tcp_rmem = 4096 87380 16777216
net.ipv4.tcp_wmem = 4096 65536 16777216

# Mitigate Silent Path MTU Discovery Blackholes during NAT64 Translation
net.ipv4.tcp_mtu_probing = 1
net.ipv4.tcp_base_mss = 1024

# Protect Against SYN Flood and Local Ephemeral Exhaustion
net.ipv4.tcp_syncookies = 1
net.ipv4.tcp_tw_reuse = 1
net.ipv4.tcp_fin_timeout = 15
net.ipv4.ip_local_port_range = 10240 65535
Apply the parameters immediately without rebooting:
sudo sysctl --systemStep 2: Configuring High-Performance Local DNS64 via Unbound
DNS64 is the foundational naming mechanism that allows IPv6-only clients to initiate connections to IPv4-only domains. While public DNS64 resolvers exist (such as Google 2001:4860:4860::6464 or Cloudflare), latency, rate limiting, and lack of internal DNS resolution dictate that enterprise clusters run local or VPC-internal Unbound DNS64 instances.
Install Unbound on your dedicated resolver or cluster gateway:
sudo apt-get update && sudo apt-get install -y unboundDeploy the following production-grade configuration to /etc/unbound/unbound.conf.d/dns64.conf:
# /etc/unbound/unbound.conf.d/dns64.conf
# Production DNS64 Resolver with DNSSEC Validation and Cache Optimization

server:
    verbosity: 1
    interface: ::0
    interface-automatic: yes
    port: 53
    do-ip4: yes
    do-ip6: yes
    do-udp: yes
    do-tcp: yes

    # Access Control: Permit your internal IPv6 VPC prefix
    access-control: ::1/128 allow
    access-control: 2001:db8:1000::/48 allow
    access-control: fe80::/10 allow
    access-control: ::/0 refuse

    # Load Modules: Must include dns64 and validator
    module-config: "dns64 validator iterator"

    # Standard RFC 6052 Well-Known Prefix (WKP)
    dns64-prefix: 64:ff9b::/96
    dns64-synthall: no
    dns64-ignore-empty-ipv6: yes

    # Performance and Cache Optimization
    num-threads: 4
    msg-cache-slabs: 4
    rrset-cache-slabs: 4
    infra-cache-slabs: 4
    key-cache-slabs: 4
    rrset-cache-size: 256m
    msg-cache-size: 128m
    so-rcvbuf: 8m
    so-sndbuf: 8m

    # Prefetching and Stale Cache Serving for Uninterrupted Resolution
    prefetch: yes
    prefetch-key: yes
    serve-expired: yes
    serve-expired-ttl: 86400
    serve-expired-client-timeout: 1800

    # Hardening against Cache Poisoning
    harden-glue: yes
    harden-dnssec-stripped: yes
    harden-below-nxdomain: yes
    qname-minimisation: yes
    hide-identity: yes
    hide-version: yes

forward-zone:
    name: "."
    forward-addr: 2606:4700:4700::1111#cloudflare-dns.com
    forward-addr: 2606:4700:4700::1001#cloudflare-dns.com
    forward-addr: 2001:4860:4860::8888#dns.google
    forward-addr: 2001:4860:4860::8844#dns.google
Validate the syntax and restart the resolver daemon:
sudo unbound-checkconf /etc/unbound/unbound.conf.d/dns64.conf
sudo systemctl restart unbound
sudo systemctl enable unbound
Step 3: Stateful NAT64 Implementation with Jool Kernel Module
While user-space translation utilities like Tayga are functional for lightweight tasks, enterprise cloud clusters with high-throughput microservices require in-kernel packet translation. Jool is the industry standard Open Source SIIT and Stateful NAT64 implementation, running directly as a Linux kernel module with minimal CPU overhead.
On your cluster NAT64 gateway node (which possesses both a public IPv4 address and an internal/external IPv6 allocation), install the DKMS package:
sudo apt-get update
sudo apt-get install -y dkms jool-dkms jool-tools
Configure the stateful NAT64 instance in /etc/jool/jool.conf:
{
  "comment": "Enterprise Stateful NAT64 Gateway Configuration",
  "framework": "netfilter",
  "global": {
    "pool6": "64:ff9b::/96",
    "lowest-ipv6-mtu": 1280,
    "f-args": 16,
    "handle-rst-during-fin-rcv": true
  },
  "pool4": [
    {
      "protocol": "TCP",
      "prefix": "198.51.100.50/32",
      "port-range": "1024-65535"
    },
    {
      "protocol": "UDP",
      "prefix": "198.51.100.50/32",
      "port-range": "1024-65535"
    },
    {
      "protocol": "ICMP",
      "prefix": "198.51.100.50/32"
    }
  ]
}
To ensure Jool initializes reliably upon system boot, create a dedicated systemd service unit at /etc/systemd/system/jool-nat64.service:
[Unit]
Description=Jool Stateful NAT64 Kernel Translation Service
After=network.target network-online.target
Wants=network-online.target

[Service]
Type=oneshot
RemainAfterExit=yes
ExecStartPre=/sbin/modprobe jool
ExecStart=/usr/bin/jool file handle /etc/jool/jool.conf
ExecStop=/usr/bin/jool instance remove default
ExecStopPost=/sbin/modprobe -r jool

[Install]
WantedBy=multi-user.target
Enable and start the service:
sudo systemctl daemon-reload
sudo systemctl enable --now jool-nat64.service
Step 4: MSS Clamping and Firewall Hardening with nftables
Because IPv6 headers require 40 bytes while IPv4 headers require only 20 bytes, translating between protocols can cause packet expansion that exceeds standard Ethernet MTU (1500 bytes). If an upstream router drops packets with the Don’t Fragment (DF) bit set and fails to return ICMPv6 Packet Too Big messages (creating an ICMP blackhole), connections freeze during TLS handshakes.
Enforce strict TCP MSS clamping and stateful egress translation rules inside /etc/nftables.conf on the gateway:
#!/usr/sbin/nft -f
# /etc/nftables.conf - Gateway MSS Clamping and Traffic Isolation

flush ruleset

table inet filter {
    chain input {
        type filter hook input priority 0; policy drop;

        # Accept loopback traffic
        iif "lo" accept

        # Accept established and related connections
        ct state established,related accept

        # Accept ICMPv6 essentials (NDP, Echo Request, Packet Too Big)
        icmpv6 type { destination-unreachable, packet-too-big, time-exceeded, parameter-problem, echo-request, echo-reply, nd-router-solicit, nd-router-advert, nd-neighbor-solicit, nd-neighbor-advert } accept

        # Accept SSH on management port
        tcp dport 22 accept
    }

    chain forward {
        type filter hook forward priority 0; policy accept;

        # Enforce TCP MSS Clamping to prevent MTU blackholes during 6-to-4 translation
        tcp flags syn tcp option maxseg size set rt mtu
    }

    chain output {
        type filter hook output priority 0; policy accept;
    }
}
Activate the firewall policy:
sudo nft -f /etc/nftables.conf
sudo systemctl enable nftables/etc/docker/daemon.json) with "ipv6": true and assign a fixed "fixed-cidr-v6": "fd00:d0c::/64". Containers will transparently inherit the host’s DNS64 nameservers and route through NAT64 without requiring individual IPv4 bridges.Step 5: Verifying Real-World Resolution and Egress
With DNS64 and NAT64 active, verify the complete synthetic translation pipeline from an IPv6-only worker node. For this test, select a domain known to operate exclusively on IPv4 (such as ipv4.google.com or legacy package archives):
# 1. Query the AAAA record of an IPv4-only host
dig AAAA ipv4.google.com +short

# Expected Output: Synthesized address within RFC 6052 prefix
# 64:ff9b::d83a:d06e

# 2. Test ICMPv6 reachability through the NAT64 gateway
ping6 -c 3 64:ff9b::d83a:d06e

# 3. Test HTTP/TLS application payload fetching
curl -6 -Iv https://ipv4.google.com

# 4. Verify Jool NAT64 state table entries on the gateway
sudo jool session display --tcp
The output of jool session display displays active translation mappings, showing the source IPv6 GUA address converted to the shared pool IPv4 address and destination IPv4 address translated from the synthesized 64:ff9b:: token.
Frequently Asked Questions
Can IPv6-only VPS instances receive inbound traffic from legacy IPv4 clients?
Yes, but this requires reverse proxying or an ingress gateway. NAT64 is designed for outbound (egress) traffic initiated by the IPv6 host. For inbound traffic, deploy an edge reverse proxy (such as NGINX, HAProxy, Envoy, or Cloudflare) configured with dual-stack public listeners that proxy traffic over pure IPv6 to your internal backend VPS cluster.
What happens when an application attempts to connect to a raw, hardcoded IPv4 address?
Because DNS64 operates during the DNS resolution phase, applications connecting directly to literal IPv4 addresses (e.g. 198.51.100.10:443) bypass DNS synthesis and fail on pure IPv6 sockets. To support raw IPv4 literals without assigning dual-stack addresses, implement a 464XLAT CLAT daemon (such as clatd) on the client nodes, which maps local IPv4 socket calls into synthesized IPv6 packets via a local virtual interface.
Does NAT64 degrade throughput or add measurable latency?
Kernel-space implementations like Jool incur negligible overhead, typically adding under 0.3 milliseconds of latency per packet. Because the translation involves rewriting fixed-length header fields without re-serializing payloads, a standard dual-core VPS gateway running Jool can effortlessly translate 10 Gbps+ of sustained line-rate traffic.
How does IPv6-only clustering affect APT and package updates?
Modern Linux distributions (Debian, Ubuntu, AlmaLinux, Rocky Linux) host their official package repositories on dual-stack servers with native AAAA records. For mirrors that remain IPv4-only, your local DNS64 and NAT64 setup seamlessly translates the repository domains, allowing apt update or dnf update to function without manual repository configuration.
Ready to Deploy High-Performance Infrastructure?
Experience blazing-fast NVMe storage, unmetered bandwidth, and enterprise LiteSpeed caching on CpanelFree.