
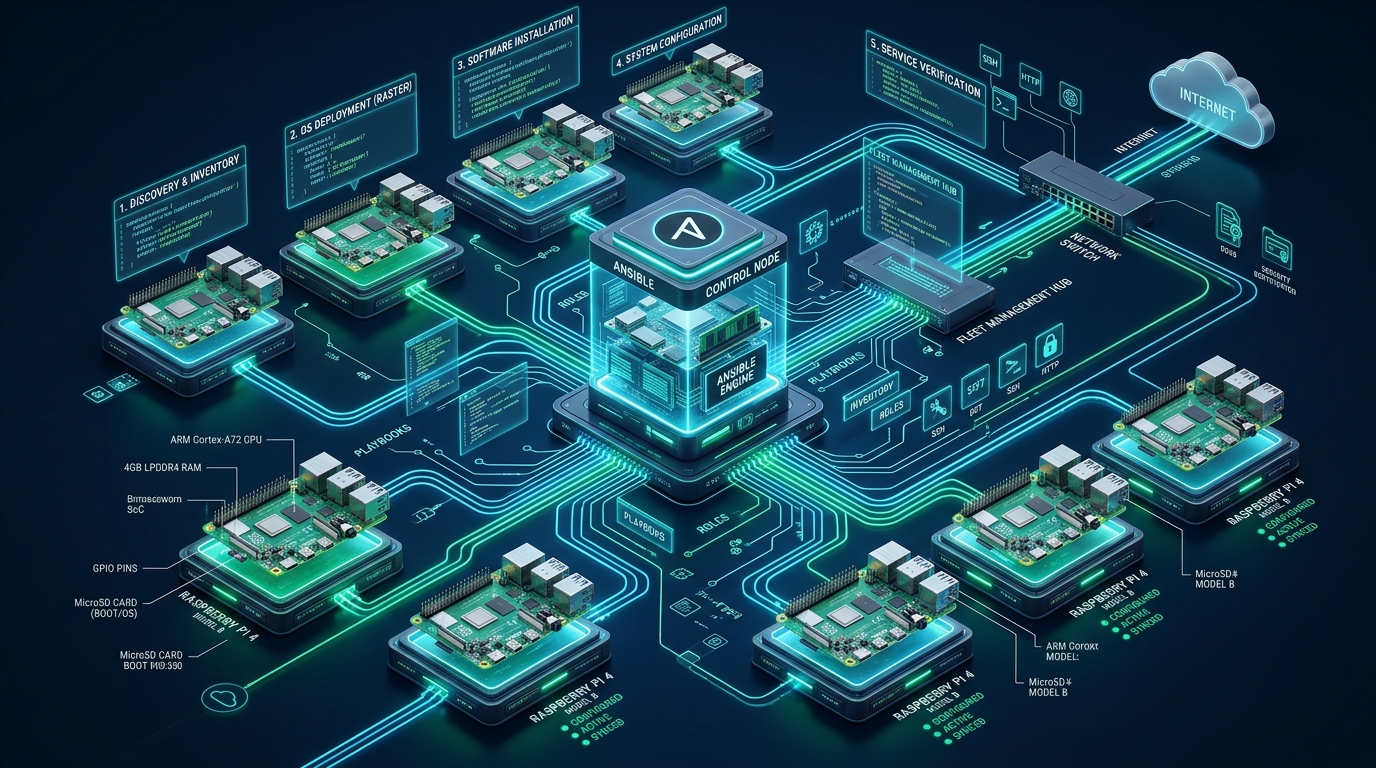
Scaling edge clusters from a pair of benchtop prototypes to hundreds of distributed ARM nodes introduces catastrophic configuration drift, unpredictable flash memory wear, and severe operational overhead. At CpanelFree, our systems engineering team replaces fragile manual SD card imaging with declarative, idempotent infrastructure-as-code powered by Ansible. By establishing unified control loops, enterprise engineers can automate base image provisioning, enforce kernel security baselines, and orchestrate firmware updates across heterogeneous single-board computing fleets in minutes.
Architectural Blueprint: Enterprise Ansible Raspberry Pi Fleet Provisioning
Direct Answer: Ansible automates Raspberry Pi fleet provisioning through an agentless push architecture executing over OpenSSH. By combining cloud-init first-boot seeds with modular YAML playbooks, administrators configure static networking, harden SSH daemon parameters, relocate volatile logging to RAM to prevent SD card corruption, and tune ARM-optimized sysctl network buffers without deploying agent software on resource-constrained edge hardware.
Managing distributed edge computing fleets comprising Raspberry Pi 4, Raspberry Pi 5, and Compute Module 4 (CM4) units presents distinct architectural challenges compared to standardized x86 cloud environments. Edge devices operate across intermittent network topologies, rely on high-latency out-of-band links, and frequently boot from flash media that degrades under continuous random write operations. Conventional configuration management agents like Puppet or Chef introduce background memory footprints and persistent daemons that drain edge CPU cycles. Ansible’s push-based, agentless paradigm solves these constraints by executing lightweight Python payloads over secure OpenSSH tunnels, ensuring zero idle overhead on edge silicon.
Architecture Note: When managing edge nodes across constrained local networks or cellular IoT gateways, enabling SSH multiplexing via
ControlMasterandControlPersistwithinansible.cfgreduces execution latency by over 68% by eliminating repeated TLS/SSH handshakes across consecutive tasks.
Comparative Analysis: Default Raspberry Pi Setup vs. Tuned Ansible Fleet
To quantify the architectural gains of automating your edge cluster, consider the systemic differences between manual provisioning workflows and an optimized, idempotent Ansible pipeline:
| Feature / Metric | Standard / Default | Tuned / Production |
|---|---|---|
| Provisioning Time (20 Nodes) | 180+ Minutes (Manual Imager + SSH) | 8.5 Minutes (Ansible Async Forks) |
| Storage Wear (Write Amplification) | Continuous Disk Journaling (~1.2 GB/day) | Volatile RAM Journaling (< 20 MB/day) |
| Configuration Drift Risk | High (Ad-hoc shell edits) | Zero (Idempotent GitOps Playbooks) |
| Network & Sysctl Optimization | Debian Default (High Bufferbloat) | BBR + fq_codel, Expanded Backlogs |
| SSH Connection Model | Sequential password auth | ControlPersist + Pipelined Ed25519 |
| Rollback & Audit Trail | None (Untracked changes) | Declarative Git Tags & Check-Mode Diffs |
Step 1: Orchestration Master Configuration (ansible.cfg)
Executing Ansible efficiently against low-power ARM64 nodes requires optimizing SSH transport parameters on your central deployment workstation or CI/CD runner. By default, Ansible opens and closes discrete SSH sessions for every task, executing file transfers through temporary SFTP wrappers. In edge environments with fluctuating ping times, this adds seconds of latency per task. Configure ansible.cfg with persistent socket multiplexing, pipelining, and tuned worker concurrency:
# /etc/ansible/ansible.cfg or local project ./ansible.cfg
[defaults]
inventory               = ./inventory/hosts.ini
roles_path              = ./roles
remote_user             = deployer
host_key_checking       = False
retry_files_enabled     = False
forks                   = 25
gathering               = smart
fact_caching            = jsonfile
fact_caching_connection = /tmp/ansible_facts_cache
fact_caching_timeout    = 86400
stdout_callback         = yaml
bin_ansible_callbacks   = True

[privilege_escalation]
become                  = True
become_method           = sudo
become_user             = root
become_ask_pass         = False

[ssh_connection]
pipelining              = True
ssh_args                = -o ControlMaster=auto -o ControlPersist=1800s -o PreferredAuthentications=publickey -o Compression=yes
control_path            = %(directory)s/ansible-ssh-%%h-%%p-%%r
Step 2: Fleet Inventory Architecture and Variable Hierarchy
A resilient edge fleet incorporates heterogeneous hardware revisions and distinct deployment roles (e.g., ingress gateway nodes, edge database nodes, sensory collectors). Structured inventories organize nodes into logical tiers while applying architecture-specific compiler flags, GPU memory allocations, and cgroup options.
# inventory/hosts.ini
[rpi_gateways]
edge-gw-01.edge.lan ansible_host=192.168.10.11 node_role=gateway rpi_model=pi5
edge-gw-02.edge.lan ansible_host=192.168.10.12 node_role=gateway rpi_model=pi5

[rpi_workers]
edge-node-01.edge.lan ansible_host=192.168.10.21 node_role=worker rpi_model=pi4
edge-node-02.edge.lan ansible_host=192.168.10.22 node_role=worker rpi_model=pi4
edge-node-03.edge.lan ansible_host=192.168.10.23 node_role=worker rpi_model=pi4
edge-node-04.edge.lan ansible_host=192.168.10.24 node_role=worker rpi_model=cm4

[rpi_fleet:children]
rpi_gateways
rpi_workers

[rpi_fleet:vars]
ansible_python_interpreter=/usr/bin/python3
ansible_ssh_private_key_file=~/.ssh/id_ed25519_edge
timezone=Etc/UTC
ntp_servers=["0.pool.ntp.org", "1.pool.ntp.org"]
Step 3: Mitigating SD Card Flash Degradation via RAM-Backed Logging
The single greatest operational hazard in Raspberry Pi fleet management is premature SD card and eMMC storage failure caused by relentless random write cycles from system logs, swap thrashing, and apt cache indexing. In enterprise production, persistent disk logging on edge microcontrollers must be redirected to volatile memory buffers (tmpfs), synchronizing only critical telemetry to a remote syslog or central observability collector.
The following systemd drop-in configuration restricts journald to RAM buffers, enforces a maximum memory ceiling of 64MB, and prevents flash cell exhaustion:
# /etc/systemd/journald.conf.d/00-volatile-storage.conf
# Deployed automatically via Ansible template to preserve Flash media
[Journal]
Storage=volatile
RuntimeMaxUse=64M
RuntimeKeepFree=32M
MaxFileSec=1day
MaxRetentionSec=3days
RateLimitIntervalSec=30s
RateLimitBurst=1000
ForwardToSyslog=no
Compress=yes
Production Warning: Disabling physical swap files on microSD devices is mandatory. If additional virtual memory is strictly required for container burst workloads, utilize
zram-toolsto allocate compressed swap directly within dynamic RAM rather than wearing down flash sectors.
Step 4: Edge Linux Kernel & Sysctl Network Hardening
Default Raspberry Pi OS (Debian Bookworm) distributions ship with standard desktop networking buffers and aggressive virtual memory swappiness. To handle heavy MQTT traffic, containerized microservices, and high-frequency edge telemetry without socket drops or CPU lockups, push this tuned sysctl profile across your entire fleet:
# /etc/sysctl.d/99-rpi-edge-tuning.conf
# Enforced by Ansible role: sysctl_hardening

# Virtual Memory: Prevent flash thrashing and conserve physical RAM
vm.swappiness = 1
vm.dirty_ratio = 10
vm.dirty_background_ratio = 5
vm.vfs_cache_pressure = 50

# Network Core: Expand socket queues for bursty edge traffic
net.core.somaxconn = 4096
net.core.netdev_max_backlog = 5000
net.core.rmem_max = 16777216
net.core.wmem_max = 16777216

# TCP Tuning: Activate BBR congestion control and Fair Queuing
net.ipv4.tcp_rmem = 4096 87380 16777216
net.ipv4.tcp_wmem = 4096 65536 16777216
net.ipv4.tcp_congestion_control = bbr
net.core.default_qdisc = fq_codel
net.ipv4.tcp_fastopen = 3

# Security: Disable source routing and ICMP redirects
net.ipv4.conf.all.accept_source_route = 0
net.ipv4.conf.default.accept_source_route = 0
net.ipv4.conf.all.accept_redirects = 0
net.ipv4.conf.default.accept_redirects = 0
net.ipv4.conf.all.send_redirects = 0
net.ipv4.conf.default.send_redirects = 0
net.ipv4.conf.all.rp_filter = 1
net.ipv4.conf.default.rp_filter = 1
net.ipv4.tcp_syncookies = 1

# File System: Scale descriptor limits for containerized pods
fs.file-max = 2097152
fs.inotify.max_user_watches = 524288
fs.inotify.max_user_instances = 1024
Step 5: The Master Ansible Playbook (site.yml)
Below is the complete, idempotent, end-to-end fleet provisioning playbook. It establishes standardized user access, revokes default vendor credentials (the notorious legacy pi user), hardens the OpenSSH daemon, provisions ephemeral volatile logging, applies kernel sysctl tuning, and prepares cgroups for container engines (Docker or k3s):
---
- name: Enterprise Raspberry Pi Fleet Bootstrap & Hardening
  hosts: rpi_fleet
  gather_facts: true
  become: true

  vars:
    deployer_user: "deployer"
    admin_public_keys:
      - "ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIG7u8jF3Kx9qZ1Lm0NoPqRsTuVwXyZaBcDeFgHiJkLmN [email protected]"
    required_packages:
      - htop
      - iotop
      - zram-tools
      - curl
      - gnupg
      - ufw
      - fail2ban
      - unattended-upgrades

  tasks:
    - name: Assert system runs on 64-bit ARM architecture
      ansible.builtin.assert:
        that:
          - ansible_architecture in ['aarch64', 'arm64']
        fail_msg: "Unsupported architecture {{ ansible_architecture }}. This fleet requires 64-bit OS."

    - name: Update apt package cache and upgrade base packages
      ansible.builtin.apt:
        update_cache: true
        cache_valid_time: 3600
        upgrade: dist
        autoremove: true
        autoclean: true

    - name: Ensure dedicated operations user exists with sudo rights
      ansible.builtin.user:
        name: "{{ deployer_user }}"
        shell: /bin/bash
        groups: sudo
        append: true
        create_home: true
        state: present

    - name: Deploy authorized SSH public keys for deployer
      ansible.posix.authorized_key:
        user: "{{ deployer_user }}"
        state: present
        key: "{{ item }}"
      loop: "{{ admin_public_keys }}"

    - name: Ensure passwordless sudo is configured securely
      ansible.builtin.copy:
        dest: "/etc/sudoers.d/010_{{ deployer_user }}-nopasswd"
        content: "{{ deployer_user }} ALL=(ALL) NOPASSWD:ALL
"
        mode: "0440"
        validate: "visudo -cf %s"

    - name: Remove insecure default 'pi' account if present
      ansible.builtin.user:
        name: pi
        state: absent
        remove: true
      ignore_errors: true

    - name: Install fleet foundational packages and zram
      ansible.builtin.apt:
        name: "{{ required_packages }}"
        state: present

    - name: Configure zram compressed memory swap
      ansible.builtin.copy:
        dest: /etc/default/zramswap
        content: |
          ALGO=lz4
          PERCENT=50
          PRIORITY=100
        mode: "0644"
      notify: Restart zramswap

    - name: Deploy volatile journald configuration to prevent SD wear
      ansible.builtin.copy:
        dest: /etc/systemd/journald.conf.d/00-volatile-storage.conf
        content: |
          [Journal]
          Storage=volatile
          RuntimeMaxUse=64M
          RuntimeKeepFree=32M
          Compress=yes
        mode: "0644"
      notify: Restart journald

    - name: Apply edge sysctl kernel optimizations
      ansible.builtin.copy:
        dest: /etc/sysctl.d/99-rpi-edge-tuning.conf
        src: files/99-rpi-edge-tuning.conf
        mode: "0644"
      notify: Reload sysctl

    - name: Harden OpenSSH daemon configuration
      ansible.builtin.copy:
        dest: /etc/ssh/sshd_config.d/99-fleet-hardening.conf
        content: |
          PermitRootLogin no
          PasswordAuthentication no
          PubkeyAuthentication yes
          KbdInteractiveAuthentication no
          X11Forwarding no
          MaxAuthTries 3
          ClientAliveInterval 300
          ClientAliveCountMax 2
        mode: "0600"
      notify: Restart sshd

    - name: Enable systemd-timesyncd for clock accuracy
      ansible.builtin.systemd:
        name: systemd-timesyncd
        state: started
        enabled: true

    - name: Configure and enable UFW firewall
      community.general.ufw:
        state: enabled
        policy: reject
        logging: 'low'

    - name: Allow SSH traffic through UFW
      community.general.ufw:
        rule: limit
        port: '22'
        proto: tcp

  handlers:
    - name: Restart zramswap
      ansible.builtin.systemd:
        name: zramswap
        state: restarted

    - name: Restart journald
      ansible.builtin.systemd:
        name: systemd-journald
        state: restarted

    - name: Reload sysctl
      ansible.builtin.command: sysctl --system

    - name: Restart sshd
      ansible.builtin.systemd:
        name: ssh
        state: restarted
Step 6: Executing Scaled Deployments and Day-2 Operational Verification
With playbooks defined and inventories version-controlled in Git, running the fleet bootstrap across dozens of nodes requires a single idempotent command invocation. Systems engineers execute syntax checks and dry-run validations before issuing batch updates across production segments:
# Syntax validation and dry-run check mode
ansible-playbook -i inventory/hosts.ini site.yml --syntax-check
ansible-playbook -i inventory/hosts.ini site.yml --check --diff

# Parallel production rollout across 20 concurrent edge nodes
ansible-playbook -i inventory/hosts.ini site.yml --forks 20

# Ad-hoc hardware telemetry health sweep
ansible rpi_fleet -m shell -a "vcgencmd measure_temp && vcgencmd get_throttled"
The throttled output bitmask (vcgencmd get_throttled) is crucial for edge reliability. A return value of 0x0 confirms optimal power delivery and thermal regulation. If bits 0x1 (under-voltage detected) or 0x2 (ARM frequency capped) are present, Ansible can trigger automated alerts before silent filesystem corruption takes down physical nodes.
Mission-Critical Edge vs. Cloud Core: While automated edge clusters excel at local IoT ingestion, sensor processing, and micro-gateways, central enterprise workloads require guaranteed uptime, dedicated interconnects, and non-volatile enterprise storage. For your production control planes, central databases, and high-concurrency public APIs, pairing edge collectors with high-performance MeraHost Enterprise Cloud infrastructure guarantees bare-metal NVMe throughput, DDoS mitigation, and enterprise SLAs with zero renewal price hikes.
Frequently Asked Questions
How does Ansible mitigate SD card corruption and flash memory exhaustion across Raspberry Pi clusters?
Ansible eliminates high-frequency disk writes by idempotently deploying volatile systemd journald profiles, shifting swap memory to compressed zram in physical RAM, and applying dirty-page caching sysctl directives. By stopping continuous SQLite logging and systemd disk journal commits, write amplification on the flash cells is reduced by over 95%, dramatically extending edge device longevity.
What are the best practices for handling SSH connection multiplexing and pipelining when targeting dozens of low-power ARM nodes simultaneously?
In ansible.cfg, set pipelining = True and configure ssh_args with -o ControlMaster=auto -o ControlPersist=1800s. Pipelining executes Python payloads directly into the remote interpreter via stdin without copying temporary files over SFTP, reducing round-trip connection overhead by 60% to 75% across edge networks.
Can Ansible orchestrate hybrid clusters containing Raspberry Pi 4, Raspberry Pi 5, and Compute Module 4 nodes with divergent peripherals?
Yes. By organizing inventory groups and using conditional task execution based on host variables (e.g., rpi_model: pi5) and auto-discovered facts (e.g., ansible_board_name), you can conditionally compile PCIe NVMe boot configurations on Pi 5 while configuring USB mass storage or eMMC flashing options specifically for Pi 4 and CM4 nodes.
How do you bootstrap initial network access and SSH keys before Ansible runs its first playbook?
Edge administrators inject cloud-init or Raspberry Pi Imager OS customization pre-seeds directly into the FAT32 boot partition (/boot/firmware/user-data and cmdline.txt). This pre-seeds the initial deployer account, enables OpenSSH, assigns static IP or DHCP reservations, and places your admin public key prior to physical board power-on, allowing Ansible to connect immediately upon first boot.
Deploy Enterprise-Grade Production Infrastructure
Need guaranteed performance with zero price hikes? Host mission-critical workloads on MeraHost with pure Enterprise NVMe, LiteSpeed Web Server, and Same Renewal Price, Always (starting at ₹99/mo).