
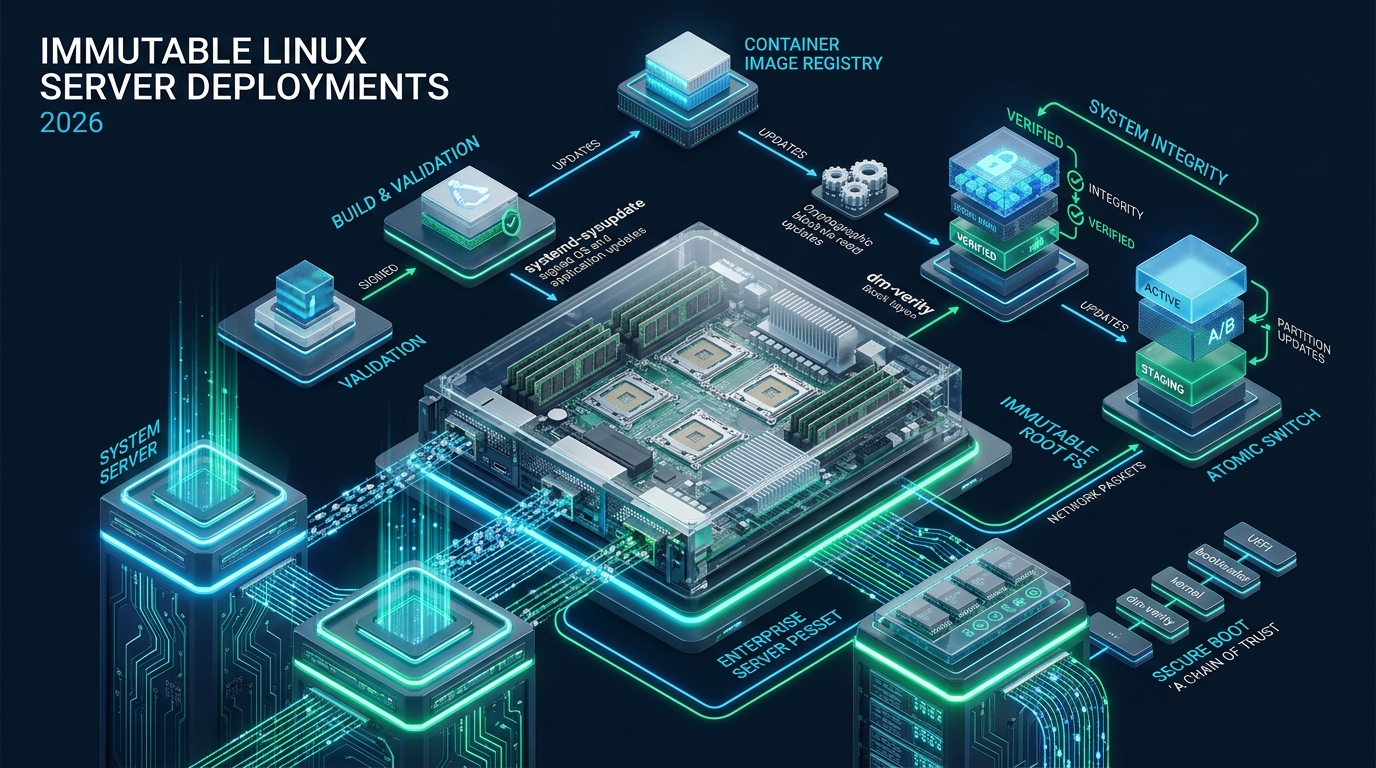
Managing production Linux fleets across bare-metal and cloud infrastructure has historically been plagued by silent configuration drift, corrupted package manager state, and fragile runtime patching cycles. In 2026, forward-thinking engineering organizations eliminate mutable runtime vulnerability by adopting cryptographically verifiable, image-based architectures hosted on high-performance cloud foundations like CpanelFree. By pairing systemd-sysupdate with cryptographic block-level verification through dm-verity, infrastructure engineers can orchestrate fully atomic, zero-drift A/B operating system upgrades with automated rollback guarantees and hardware-rooted integrity.
Understanding Immutable Linux Deployments with systemd-sysupdate and dm-verity
Direct Answer: An immutable Linux server deployment using systemd-sysupdate and dm-verity combines a read-only, cryptographically hashed operating system partition with atomic A/B slot updates. The Linux kernel’s dm-verity target verifies every filesystem block against a signed Merkle root hash at read time, while systemd-sysupdate fetches, cryptographically validates, and writes raw OS updates directly to passive disk partitions with zero runtime drift.
The Architectural Foundations: DPS, Merkle Trees, and Dual A/B Partitioning
Traditional Linux distributions manage server health through mutable package managers (such as apt, dnf, or pacman) that unpack files directly into a live, shared filesystem tree. This legacy pattern introduces non-deterministic state, incomplete transaction vulnerabilities during unexpected power cycles, and post-exploitation rootkit persistence. In contrast, modern 2026 immutable deployments enforce a strict boundary between three distinct filesystem lifecycles:
- Immutable System Layer (
/usr): The entire operating system binary tree, core libraries, and kernel runtime are packaged into a read-only partition image. No daemon or root privilege can alter these binaries at runtime. - Transient Configuration Layer (
/etc): System configurations are dynamically provisioned via stateless defaults, transient overlays, orsystemd-confextconfiguration extensions. - Persistent Stateful Layer (
/varand/home): Dedicated LUKS2-encrypted partitions store database entries, container storage, and audit logs, decoupled from the core OS lifecycle.
This model is unified by the Discoverable Partitions Specification (DPS), which assigns globally unique partition type GUIDs to automatically discover and mount partitions without relying on static /etc/fstab configurations.
4f68bce3-e8cd-4db1-96e7-fbcaf984b709, while matching dm-verity hash partitions use GUID 2c7357ed-ebd2-46d9-ba11-66a305d7443b. systemd-gpt-auto-generator automatically correlates the root and verity partitions by matching partition label identifiers.
Cryptographic Block-Level Attestation via dm-verity
While mounting filesystems read-only (mount -o ro) prevents benign accidental writes, it offers zero defense against direct block-level tampering, malicious storage device drivers, or memory corruption. dm-verity (device-mapper verity) resolves this by organizing all data blocks on the root partition into a cryptographic Merkle tree:
+-------------------------------------------------------------------------+
|                 Root Hash (Authenticated in Kernel / UKI)               |
+------------------------------------+------------------------------------+
                                     |
                  +------------------+------------------+
                  |                                     |
         +--------v--------+                   +--------v--------+
         | Level 1 Hash A  |                   | Level 1 Hash B  |
         +--------+--------+                   +--------+--------+
                  |                                     |
         +--------+--------+                   +--------+--------+
         | Level 0 Hashes  |                   | Level 0 Hashes  |
         +--------+--------+                   +--------+--------+
                  |                                     |
+-----------------v-------------------------------------v-----------------+
|  Data Block 0  |  Data Block 1  |  Data Block 2  |  Data Block 3 (4KB)  |
+-------------------------------------------------------------------------+
When an application reads a 4KB filesystem block, the Linux kernel computes its cryptographic hash, walks up the Merkle tree, and verifies the calculation against the top-level Root Hash. If even a single bit has been altered, the read call immediately triggers an I/O error (-EIO) or halts the system, neutralizing unauthorized modifications before code execution can occur.
Architectural Comparison: Mutable vs. Container-Only vs. systemd-sysupdate + dm-verity
Evaluating update mechanisms across fleet-scale infrastructure reveals stark differences in reliability, security verification, and recovery overhead. The table below highlights production engineering metrics across modern deployment models:
Production Configuration Files: sysupdate and systemd Hardening
To establish an autonomous, drift-free deployment pipeline, configure systemd-sysupdate to track remote image repositories, stream versioned raw partitions into passive A/B slots, and verify cryptographic integrity signatures.
1. Defining the A/B Root Target: /etc/sysupdate.d/50-root.conf
This configuration defines the remote source URL, version matching expression, target partition class, and validation requirements for the root OS partition:
# /etc/sysupdate.d/50-root.conf
[Transfer]
ProtectVersion=%v
Verify=signature

[Source]
Type=url-file
Path=https://updates.internal.infra.net/os/x86-64/
[email protected]

[Target]
Type=partition
Path=auto
MatchPattern=production-os_@v
MatchPartitionType=root
PartitionUUID=4f68bce3-e8cd-4db1-96e7-fbcaf984b709
ReadOnly=true
Mode=0444
InstancesMax=2
2. Companion Verity Hash Target: /etc/sysupdate.d/55-root-verity.conf
In tandem with the root filesystem, the companion dm-verity Merkle tree partition must be synchronized to ensure cryptographic validation matches the target build:
# /etc/sysupdate.d/55-root-verity.conf
[Transfer]
ProtectVersion=%v
Verify=signature

[Source]
Type=url-file
Path=https://updates.internal.infra.net/os/x86-64/
[email protected]

[Target]
Type=partition
Path=auto
[email protected]
MatchPartitionType=root-verity
PartitionUUID=2c7357ed-ebd2-46d9-ba11-66a305d7443b
ReadOnly=true
Mode=0444
InstancesMax=2
3. Automated Update Staging via systemd Timer
Schedule periodic update discovery and background staging without interrupting active production services:
# /etc/systemd/system/systemd-sysupdate.timer
[Unit]
Description=Daily Immutable OS A/B Staging Poll
Documentation=man:systemd-sysupdate(8)

[Timer]
OnCalendar=*-*-* 03:30:00 UTC
RandomizedDelaySec=1800
Persistent=true

[Install]
WantedBy=timers.target
4. Production Kernel Hardening: /etc/sysctl.d/99-immutable-hardening.conf
Enforce kernel-level execution lockdowns to complement the read-only dm-verity storage layer:
# /etc/sysctl.d/99-immutable-hardening.conf
# Disable unprivileged BPF execution to prevent kernel memory tampering
kernel.unprivileged_bpf_disabled = 1
net.core.bpf_jit_harden = 2

# Restrict kernel pointer leaks in /proc and dmesg
kernel.kptr_restrict = 2
kernel.dmesg_restrict = 1

# Disable module loading once the system reaches multi-user target
# (Set dynamically via systemd service or sysctl after boot completion)
kernel.modules_disabled = 0

# Protect symlink and hardlink traversal
fs.protected_symlinks = 1
fs.protected_hardlinks = 1
fs.protected_fifos = 2
fs.protected_regular = 2

# Immediate panic on uncorrectable dm-verity corruption errors
kernel.panic_on_oops = 1
kernel.panic = 10
Step-by-Step Deployment Guide: Generating, Verifying, and Rolling Out Images
Implementing immutable Linux server deployments requires a robust build system capable of producing reproducible root partition artifacts, computing deterministic Merkle trees, and signing distribution payloads.
Step 1: Build the Deterministic Root Filesystem Image
Using modern tooling such as systemd-repart or mkosi, construct a clean, reproducible OS root filesystem image formatted with Ext4 or EROFS:
# Generate raw root partition image
mkosi --format=disk --image-id=production-os --image-version=2026.04.1 build

# Inspect generated image partitions
systemd-dissect --list-parts production-os_2026.04.1.raw
Step 2: Generate the Merkle Tree with veritysetup
Compute the cryptographic hash tree and obtain the definitive Root Hash:
# Generate Merkle tree and extract verification metadata
veritysetup format production-os_2026.04.1.root.raw production-os_2026.04.1.verity \
  --hash=sha256 \
  --data-block-size=4096 \
  --hash-block-size=4096 \
  --salt=auto \
  --restart-on-corruption \
  > verity-metadata.txt

# Extract the generated Root Hash
ROOT_HASH=$(awk '/Root hash:/ {print $3}' verity-metadata.txt)
echo "Target Root Hash: ${ROOT_HASH}"--restart-on-corruption flag. If a storage cell degrades or malicious memory injection alters on-disk bytes, the Linux kernel refuses to serve corrupt data and triggers an immediate reboot into the healthy passive partition slot.
Step 3: Cryptographically Sign the Artifacts
To satisfy systemd-sysupdate‘s Verify=signature requirement, sign both the raw filesystem and the verity tree using minisign or enterprise PKI keys:
# Sign the compressed raw root image
minisign -Sm production-os_2026.04.1.raw.xz -s /etc/pki/infra-release.key

# Sign the companion verity tree
minisign -Sm production-os_2026.04.1.verity.xz -s /etc/pki/infra-release.key

# Upload signed bundles to internal artifact registry
rsync -avP production-os_2026.04.1.* updates.internal.infra.net:/var/www/os/x86-64/
Step 4: Execute Staged Update and Slot Validation
On running nodes, audit available updates, stream the bits into the passive partition slot, and verify the transaction:
# List current and newly discovered target versions
systemd-sysupdate list

# Execute atomic download and raw partition write
systemd-sysupdate update

# Verify bootloader entries and mark next boot attempt
bootctl list
Step 5: Automated Rollback Safeguards with systemd-boot
Deployments leverage boot assessment counters configured in systemd-boot. When a new partition slot boots, it begins with an evaluation counter (e.g. 3 attempts). Once services successfully start, the node runs bootctl mark-good to finalize the slot. If a kernel panic occurs or health checks fail, the counter decrements until the bootloader automatically reverts to the known-good passive slot.
Operational Runbook: Production Diagnostics and State Management
When operating immutable servers at scale, infrastructure teams must adapt standard debugging and state persistence workflows to align with read-only filesystems.
Dynamic Runtime Customization with systemd-sysext
If ad-hoc debugging tools (such as bpftrace, perf, or gdb) are required during incident triage, do not attempt to bypass filesystem immutability. Instead, mount temporary system extensions via systemd-sysext:
# Download authenticated diagnostic sysext image
curl -fsSL https://updates.internal.infra.net/sysext/diagnostics-2026.raw -o /var/lib/extensions/diagnostics.raw

# Merge extension into /usr hierarchy via live overlay
systemd-sysext refresh

# Confirm tooling availability
which bpftrace

# Unmerge extension following incident resolution
rm /var/lib/extensions/diagnostics.raw
systemd-sysext refresh
Investigating dm-verity Block Faults
If a storage medium experiences silent bit rot or underlying block corruption, inspect the kernel ring buffer to identify degraded blocks:
# Filter journal for device-mapper integrity events
journalctl -k -g "device-mapper: verity"

# Query current dm-verity device status
dmsetup status root-verity-active

# Example output indicating hardware read degradation:
# root-verity-active: 0 4194304 verity V 2048 0 - 0
Frequently Asked Questions
How do stateful applications store data when the root filesystem is mounted with dm-verity?
Stateful applications (such as PostgreSQL, Redis, or Docker/Podman runtimes) write strictly to dedicated persistent partitions mounted at /var, /srv, or /opt. The root filesystem (/usr and base directories) remains read-only and cryptographically verified, completely separating application state from the operating system lifecycle.
What happens if a block becomes corrupted while the server is actively running?
When dm-verity detects a hash mismatch upon reading a 4KB block, it blocks the read call and returns an -EIO error. If the kernel was booted with --restart-on-corruption or panic_on_corruption, the kernel halts immediately and reboots into the secondary passive slot, preventing compromised or corrupted binaries from executing.
Can systemd-sysupdate perform delta updates to reduce network bandwidth?
Yes. systemd-sysupdate supports Casync and block-level transfer protocols. By combining chunk-based HTTP range queries with zstandard or xz compression, only modified partition blocks are transferred over the wire, drastically reducing update bandwidth across multi-thousand node fleets.
How does systemd-sysupdate differ from rpm-ostree or OSTree-based distributions?
While OSTree operates like a git tree for filesystem files with a mutable 3-way merge on /etc, systemd-sysupdate operates directly on disk partitions and raw disk images according to the Discoverable Partitions Specification (DPS). This enables native block-level dm-verity cryptographic verification that OSTree’s userspace file trees cannot match.
Ready to Deploy High-Performance Infrastructure?
Experience blazing-fast NVMe storage, unmetered bandwidth, and enterprise LiteSpeed caching on CpanelFree.