
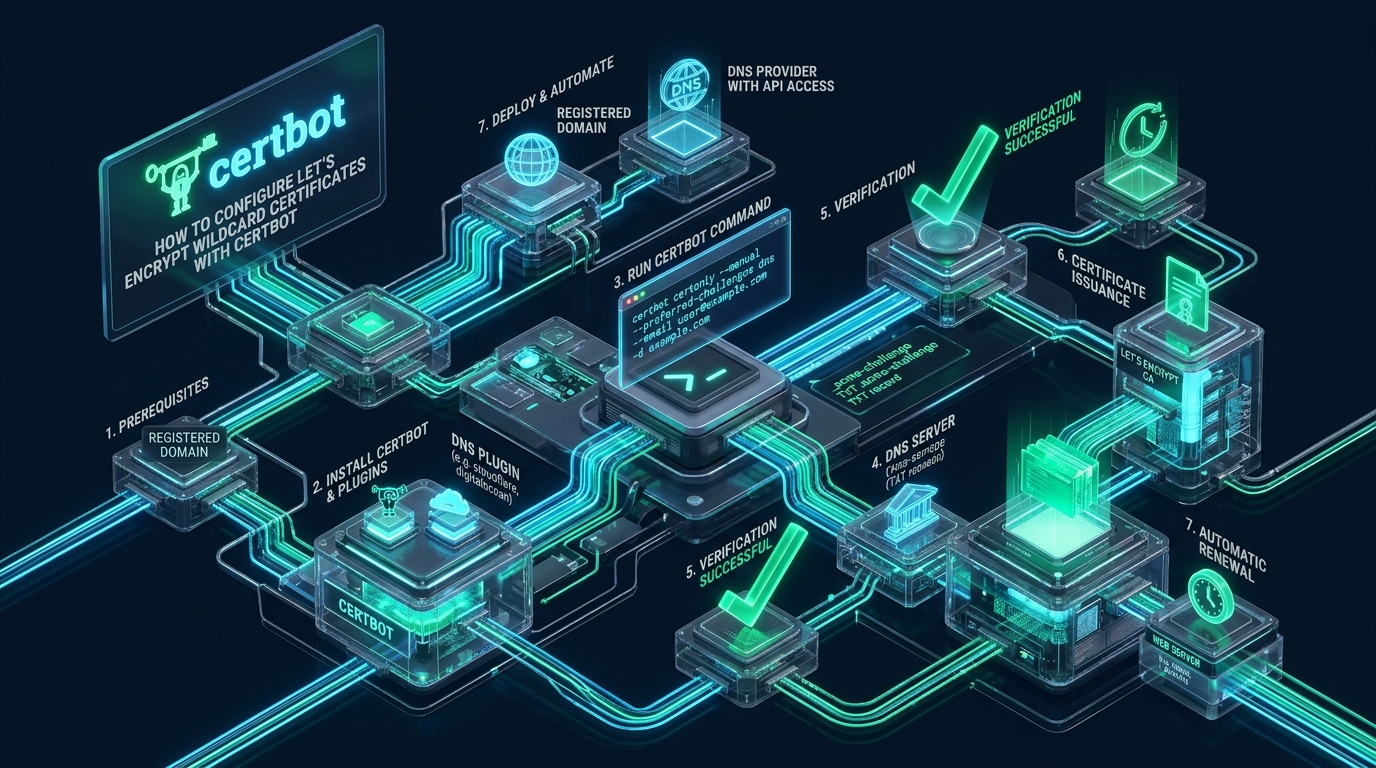
Managing dynamic multi-tenant architectures, ephemeral microservices, and customer staging environments often leads to administrative friction when provisioning individual SSL/TLS certificates for dozens of subdomains. Traditional HTTP-01 ACME challenges fail at scale because they necessitate exposed ingress ports, individual certificate renewals, and fragile webroot path routing. By deploying wildcard certificates via CpanelFree and Certbot, systems engineers consolidate cryptographic overhead into a single, high-performance TLS asset that automatically secures both root apex domains and any arbitrary child subdomain without service disruption.
What Is Required to Configure Let’s Encrypt Wildcard Certificates with Certbot?
Direct Answer: Configuring Let’s Encrypt wildcard certificates (*.example.com) with Certbot requires passing the ACME DNS-01 challenge by validating domain ownership via DNS TXT records. Install Certbot along with your DNS provider’s plugin (e.g., Cloudflare, Route53, or RFC 2136), store restricted API credentials in a 0600 configuration file, and execute Certbot with both apex and wildcard flags. This enables completely automated, zero-touch certificate renewals.
Wildcard TLS certificates represent a foundational building block for modern cloud infrastructure. Whether you are running containerized Kubernetes ingress controllers, dynamic development environments, or SaaS platforms serving on-demand tenant portals, provisioning a distinct certificate for every new hostname introduces exponential complexity. Individual certificates consume rate limits against Let’s Encrypt certificate authority (CA) endpoints, increase storage footprint in edge proxies, and multiply renewal failure points.
Under the Automated Certificate Management Environment (ACME) protocol defined in RFC 8555, Let’s Encrypt strictly mandates DNS-01 validation for all wildcard identifier requests. This guide provides an end-to-end, enterprise-ready walkthrough of architecting, deploying, and maintaining automated Let’s Encrypt wildcard certificates using Certbot and authoritative DNS provider APIs.
ACME Challenge Protocols: DNS-01 vs. HTTP-01 Under the Hood
To understand why wildcard certificates require specialized tooling, engineers must examine the cryptographic mechanics of ACME challenge types. The standard HTTP-01 challenge relies on placing a calculated token at a specific URI under /.well-known/acme-challenge/<TOKEN> over HTTP port 80. While convenient for single web servers, HTTP-01 proves ownership of only one specific fully qualified domain name (FQDN). It cannot prove administrative control over the entire parent DNS zone.
Conversely, the DNS-01 challenge requires provisioning a computed cryptographic digest as a TXT record at _acme-challenge.<YOUR_DOMAIN>. Because modifying the zone’s authoritative nameservers demonstrates complete administrative authority over the entire namespace, Let’s Encrypt accepts DNS-01 as proof of control for the wildcard pattern *.example.com.
| Feature / Metric | Standard / Default | Tuned / Production |
|---|---|---|
| Validation Challenge | HTTP-01 (Port 80 Webroot) | DNS-01 TXT Record API |
| Wildcard Coverage (*.domain) | Unsupported (Single SANs only) | Full Subdomain Coverage |
| Internal / Edge Routing Exposure | Requires Public Ingress Port 80 | Zero Public Firewall Openings |
| Renewal Automation Latency | Manual DNS Intervention (15+ min) | Automated Systemd Cron (<30s) |
| Certificate Maintenance Overhead | High (10-50 standalone certs) | Single Wildcard Pair / Origin |
Architecture Note: A wildcard entry like
*.example.comprotects only direct first-level subdomains (such asapp.example.comorapi.example.com). It does not validate nested multi-level subdomains likedev.api.example.com, nor does it cover the apex domainexample.comitself. You must always pass both-d example.comand-d "*.example.com"during request execution to ensure complete coverage.
Prerequisites and Securing DNS API Access Credentials
Automating DNS-01 validation requires granting Certbot programmatic write access to your authoritative DNS zone to create and destroy transient _acme-challenge TXT records. Never use global account credentials or master administrative keys. Modern DNS providers like Cloudflare, AWS Route53, and DigitalOcean provide granular, scoped API tokens designed specifically for this purpose.
When provisioning a Cloudflare API token for Let’s Encrypt wildcard management, configure the following least-privilege policy parameters:
- Permissions:
Zone - DNS - Edit(Read and Write access to DNS records). - Zone Resources:
Include - Specific Zone - example.com(Never apply “All Zones” unless operating a multi-tenant DNS gateway). - Client IP Address Filtering: Restrict token authorization strictly to the egress static IP address of your primary certificate manager node.
- TTL / Expiration: Set operational review cycles or periodic key rotation schedules aligned with organizational compliance.
Create a dedicated configuration directory and secure credential file on your production host with strict POSIX file permissions to prevent unauthorized lateral privilege reading:
# Create Let's Encrypt secure configuration store
sudo mkdir -p /etc/letsencrypt/credentials
sudo touch /etc/letsencrypt/credentials/cloudflare.ini

# Apply strict owner-only read/write permissions (0600)
sudo chmod 600 /etc/letsencrypt/credentials/cloudflare.ini
sudo chown root:root /etc/letsencrypt/credentials/cloudflare.ini

# Populate the scoped Cloudflare API token
cat << 'EOF' | sudo tee /etc/letsencrypt/credentials/cloudflare.ini
# Cloudflare API token with Zone:DNS:Edit permissions
dns_cloudflare_api_token = 0123456789abcdef0123456789abcdef01234567
EOF
Installing Certbot and the DNS Cloudflare Plugin
The Electronic Frontier Foundation (EFF) officially recommends installing Certbot and its official DNS plugins via Snapd to ensure consistent Python dependencies and rapid receipt of upstream ACME RFC updates. On modern Debian, Ubuntu, AlmaLinux, and Rocky Linux systems, follow the standardized snap execution path:
# Remove legacy system packages if present
sudo apt remove certbot -y 2>/dev/null || sudo dnf remove certbot -y 2>/dev/null

# Install core snap daemon and refresh
sudo snap install core && sudo snap refresh core

# Install Certbot via Snap with classic confinement
sudo snap install --classic certbot
sudo ln -sf /snap/bin/certbot /usr/bin/certbot

# Install DNS Cloudflare plugin and grant required capabilities
sudo snap install certbot-dns-cloudflare
sudo snap set certbot trust-plugin-with-root=ok
sudo snap connect certbot:plugin certbot-dns-cloudflare

# Verify installation and plugin discovery
certbot plugins
Executing certbot plugins should clearly output dns-cloudflare in the discovered plugin registry, confirming that Certbot’s runtime engine can interface directly with Cloudflare’s upstream REST endpoints.
Issuing the Wildcard Certificate: Production Command and Flags
With credentials and plugins locked down, execute the certificate request. Notice the inclusion of both the apex domain (example.com) and the wildcard domain (*.example.com). The --dns-cloudflare-propagation-seconds flag specifies how long Certbot pauses after creating the _acme-challenge TXT record before notifying the Let’s Encrypt validation server.
sudo certbot certonly \
  --dns-cloudflare \
  --dns-cloudflare-credentials /etc/letsencrypt/credentials/cloudflare.ini \
  --dns-cloudflare-propagation-seconds 60 \
  -d example.com \
  -d "*.example.com" \
  --agree-tos \
  --email [email protected] \
  --no-eff-email \
  --key-type ecdsa \
  --elliptic-curve secp384r1
Architecture Note: Let’s Encrypt uses Multi-Perspective Validation (MPV), querying your authoritative nameservers from multiple geographically distributed vantage points to prevent BGP hijacking and localized DNS spoofing. Setting
--dns-cloudflare-propagation-seconds 60ensures changes propagate globally across all authoritative nodes before validation begins.
Notice also the flag --key-type ecdsa --elliptic-curve secp384r1. Modern systems architects favor Elliptic Curve Cryptography (ECDSA) over legacy RSA 2048/4096. ECDSA keys provide significantly higher cryptographic strength per bit, reduce TLS handshake packet sizes, lower CPU overhead during TLS negotiation, and optimize Time to First Byte (TTFB) across high-throughput connections.
Automating Zero-Downtime Service Reloads with Deploy Hooks
A renewed certificate written to disk is inert until your active edge proxies, load balancers, and web servers reload the updated PEM files into memory. Never restart daemons abruptly during renewals, which disrupts active TCP connections. Instead, configure an atomic Certbot post-deployment hook that triggers graceful configuration reloads.
Place an executable shell script inside Certbot’s standardized renewal hooks directory at /etc/letsencrypt/renewal-hooks/deploy/:
#!/usr/bin/env bash
# /etc/letsencrypt/renewal-hooks/deploy/01-reload-edge-services.sh
set -euo pipefail

# Log renewal event to syslog
logger -t certbot-deploy-hook "Certificate renewal detected for domains: ${RENEWED_DOMAINS:-unknown}"

# Test and gracefully reload Nginx web server
if systemctl is-active --quiet nginx; then
    if nginx -t >/dev/null 2>&1; then
        systemctl reload nginx
        logger -t certbot-deploy-hook "Nginx gracefully reloaded successfully."
    else
        logger -s -t certbot-deploy-hook "Nginx configuration syntax test failed! Aborting reload."
        exit 1
    fi
fi

# Reload HAProxy if running
if systemctl is-active --quiet haproxy; then
    systemctl reload haproxy
    logger -t certbot-deploy-hook "HAProxy reloaded successfully."
fi

exit 0
Set POSIX execution rights on the hook script:
sudo chmod +x /etc/letsencrypt/renewal-hooks/deploy/01-reload-edge-services.sh
sudo chown root:root /etc/letsencrypt/renewal-hooks/deploy/01-reload-edge-services.sh
Whenever Certbot renews a certificate, it iterates through scripts located in renewal-hooks/deploy/, passing context environment variables like $RENEWED_DOMAINS and $RENEWED_LINEAGE, ensuring zero-downtime hot reloading across your edge layer.
Configuring Nginx for Production Wildcard TLS Termination
Now that your wildcard keypair is securely generated at /etc/letsencrypt/live/example.com/, configure your edge reverse proxy. Below is a hardened, production-tuned Nginx virtual host block leveraging modern TLS 1.3 ciphers, HTTP/2, OCSP stapling, and dynamic subdomain routing:
# /etc/nginx/conf.d/wildcard-production.conf
server {
    listen 80;
    listen [::]:80;
    server_name example.com *.example.com;

    # Redirect all plain HTTP traffic to hardened HTTPS
    return 301 https://$host$request_uri;
}

server {
    listen 443 ssl http2;
    listen [::]:443 ssl http2;
    server_name example.com *.example.com;

    # Let's Encrypt Wildcard Certificate Chains
    ssl_certificate /etc/letsencrypt/live/example.com/fullchain.pem;
    ssl_certificate_key /etc/letsencrypt/live/example.com/privkey.pem;

    # Cryptographic Protocols and Ciphers
    ssl_protocols TLSv1.2 TLSv1.3;
    ssl_prefer_server_ciphers off;
    ssl_ciphers 'ECDHE-ECDSA-AES128-GCM-SHA256:ECDHE-RSA-AES128-GCM-SHA256:ECDHE-ECDSA-AES256-GCM-SHA384:ECDHE-RSA-AES256-GCM-SHA384:DHE-RSA-AES128-GCM-SHA256:DHE-RSA-AES256-GCM-SHA384';

    # TLS Session Caching and Resumption
    ssl_session_cache shared:SSL:10m;
    ssl_session_timeout 1d;
    ssl_session_tickets off;

    # OCSP Stapling for Ultra-Fast Client Handshakes
    ssl_stapling on;
    ssl_stapling_verify on;
    ssl_trusted_certificate /etc/letsencrypt/live/example.com/chain.pem;
    resolver 1.1.1.1 1.0.0.1 8.8.8.8 valid=300s;
    resolver_timeout 5s;

    # Enterprise Security Headers
    add_header Strict-Transport-Security "max-age=63072000; includeSubDomains; preload" always;
    add_header X-Content-Type-Options "nosniff" always;
    add_header X-Frame-Options "SAMEORIGIN" always;
    add_header Referrer-Policy "strict-origin-when-cross-origin" always;

    # Dynamic backend upstream routing
    location / {
        proxy_pass http://127.0.0.1:8080;
        proxy_set_header Host $host;
        proxy_set_header X-Real-IP $remote_addr;
        proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
        proxy_set_header X-Forwarded-Proto $scheme;
    }
}
For production enterprise workloads requiring zero-latency TLS handshakes, dedicated IPv4/IPv6 subnets, and mission-critical reliability, deploying wildcard certificates on MeraHost Enterprise Cloud pairs seamless Let’s Encrypt automation with ultra-fast LiteSpeed Web Server and pure enterprise NVMe storage.
Verifying Automated Renewals and Systemd Timers
When Certbot is installed via snap, it automatically provisions an active systemd timer (certbot.timer) that executes twice daily at randomized jitter windows. This prevents stampeding herds against Let’s Encrypt certificate authorities. Certbot evaluates existing certificates and triggers renewal only when a certificate is within 30 days of its 90-day expiration window.
Always verify the health and schedule of your systemd timer:
# Inspect systemd timer status and next trigger window
systemctl status certbot.timer

# View active timers across the system
systemctl list-timers certbot.timer

# Perform a non-destructive dry-run simulation
sudo certbot renew --dry-run
A successful dry-run simulation produces the following output confirmation:
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Processing /etc/letsencrypt/renewal/example.com.conf
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Simulating renewal of an existing certificate for example.com and *.example.com
The dry run was successful.
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Enterprise Troubleshooting and Architectural Edge Cases
Even seasoned systems architects encounter specific edge-case scenarios when configuring wildcard SSL infrastructure. Keep these battle-tested operational rules in mind:
- DNS CAA Records: If your domain enforces Certificate Authority Authorization (CAA) records, verify that
issueandissuewilddirectives explicitly permit Let’s Encrypt. For example:example.com. IN CAA 0 issuewild "letsencrypt.org". Ifissuewildis absent, Let’s Encrypt falls back to standardissuetags, but if misconfigured, renewals fail with an unauthorized error. - CNAME Delegation for Split-Horizon / Internal Zones: If your origin servers reside inside a private air-gapped VPC or internal network without direct access to production Cloudflare tokens, configure CNAME alias delegation. Point
_acme-challenge.example.comvia CNAME to a dedicated validation zone (e.g.,auth.acme-infra.net). Certbot can then manage TXT records strictly on the validation zone without exposing primary domain DNS credentials. - Rate Limit Mitigation: Let’s Encrypt enforces strict limits: 50 certificates per registered domain per week, and 5 duplicate certificates per week. Wildcard certificates dramatically conserve these quotas by replacing tens of distinct single-name certificates with one comprehensive pair.
Frequently Asked Questions
Does a Let’s Encrypt wildcard certificate protect nested subdomains like api.v1.example.com?
No. Standard RFC 6125 wildcard matching specifies that an asterisk (*) matches exactly one DNS label. A certificate issued for *.example.com validates api.example.com and staging.example.com, but will produce a certificate name mismatch error on nested subdomains like v1.api.example.com. If you require multi-level subdomain protection, you must explicitly request an additional SAN identifier such as -d "*.api.example.com" or provision dedicated certificates for nested tiers.
Why does Let’s Encrypt disallow HTTP-01 validation for wildcard certificates?
HTTP-01 validation relies on answering an HTTP GET request on port 80 at a single IP address. However, different subdomains under a domain might point to entirely separate physical servers, geographic clusters, or third-party SaaS vendors. Fulfilling an HTTP challenge on one server does not prove administrative ownership over the entire parent DNS namespace. The DNS-01 challenge requires writing authoritative zone records, providing cryptographically sound proof of complete administrative domain control.
Can I use Certbot wildcard certificates on private or internal-only servers?
Yes, absolutely. This is one of the greatest operational advantages of the DNS-01 challenge. Because Let’s Encrypt verifies domain ownership by querying public authoritative DNS servers rather than contacting your host server directly, your origin web server does not require public internet ingress, exposed port 80/443 firewalls, or public IP addresses. Internal development boxes, intranet portals, and private VPN endpoints can easily obtain fully trusted, valid certificates.
How do I prevent DNS API token compromise on multi-user servers?
Always create scoped, single-purpose API tokens rather than using global account keys. Restrict the token permissions solely to DNS:Edit on the specific zone, bind the token to your server’s static egress IP, and store the credential file in an access-restricted directory owned by root with 0600 permissions. For shared environments, consider delegating _acme-challenge via CNAME to a dedicated validation zone or using an ACME proxy such as acme-dns to eliminate direct cloud provider API credentials from edge nodes.
Deploy Enterprise-Grade Production Infrastructure
Need guaranteed performance with zero price hikes? Host mission-critical workloads on MeraHost with pure Enterprise NVMe, LiteSpeed Web Server, and Same Renewal Price, Always (starting at ₹99/mo).