
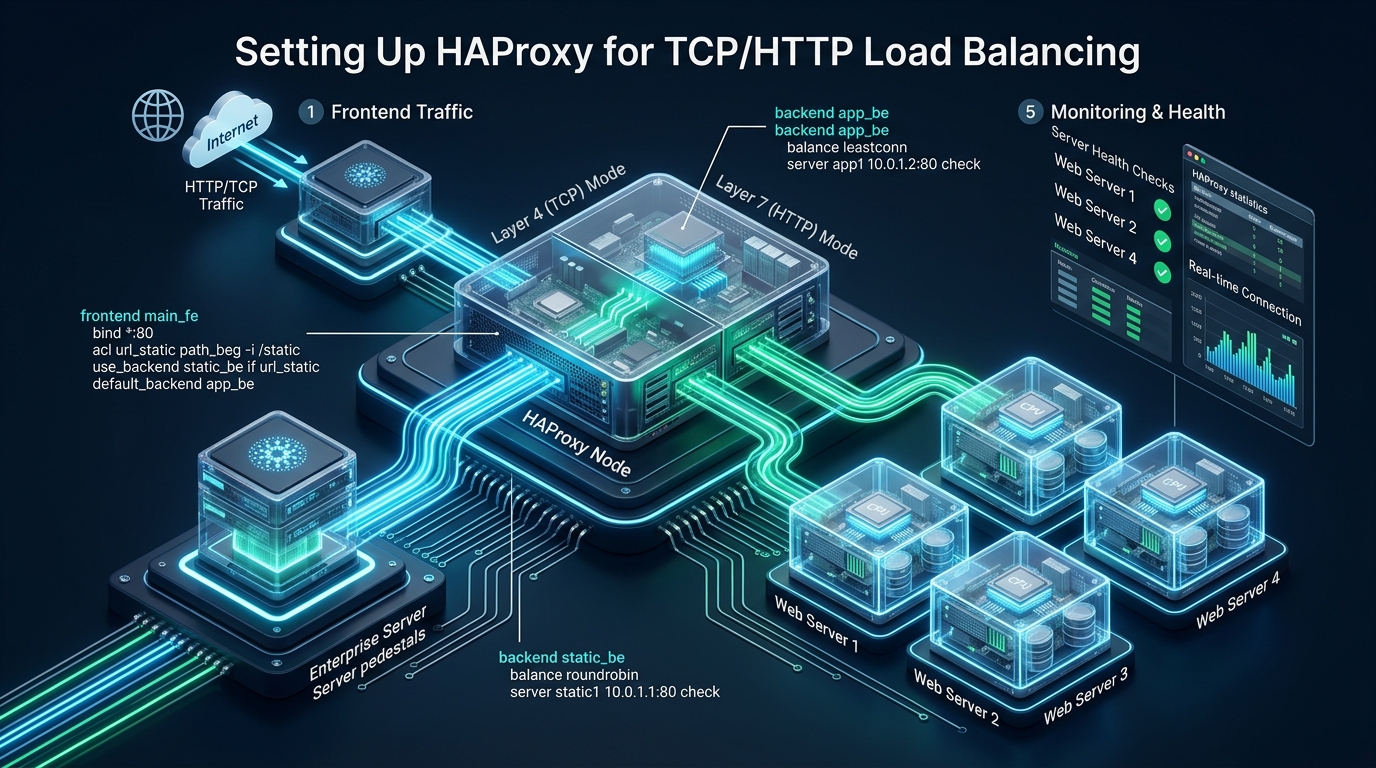
When scaling Linux infrastructure beyond single-instance bottlenecks, distributed traffic routing dictates whether microservices maintain sub-millisecond latencies or cascade into catastrophic connection timeouts under heavy concurrency. Engineering resilient architectures requires a battle-tested reverse proxy capable of handling both raw socket throughput and deep HTTP protocol inspection without consuming excessive CPU cycles. Whether deploying testing and staging environments on CpanelFree or orchestrating tier-one application clusters across distributed regions, mastering HAProxy is the foundational prerequisite for high-availability systems engineering.
Architectural Overview: Layer 4 (TCP) vs. Layer 7 (HTTP) Routing
Quick Summary: In this definitive haproxy tutorial linux guide, HAProxy operates across two primary paradigms: Layer 4 (TCP mode) for ultra-low latency, protocol-agnostic stream routing (e.g., MySQL, Redis, TLS passthrough), and Layer 7 (HTTP mode) for content-aware routing, header manipulation, cookie persistence, and SSL termination. Correct configuration provides zero-downtime failover and linear horizontal scalability across modern enterprise Linux clusters.
High Availability Proxy (HAProxy) is an industry-standard, event-driven, non-blocking reverse proxy and load balancer. Unlike threaded or process-per-connection architectures that consume significant memory under heavy concurrency, HAProxy utilizes an optimized single-process, multi-threaded event loop driven by the Linux kernel’s epoll subsystem. This enables a single HAProxy instance to handle upwards of 100,000 concurrent connections while maintaining a negligible memory footprint.
Understanding the operational distinction between Layer 4 (Transport) and Layer 7 (Application) load balancing is crucial when architecting infrastructure pipelines:
- Layer 4 Load Balancing (
mode tcp): HAProxy forwards raw byte streams between the client and backend nodes without inspecting packet payloads. Routing decisions are made solely based on the client IP address, destination IP, source/destination ports, and Server Name Indication (SNI) headers during the initial TLS handshake. Because there is zero application-layer parsing, CPU overhead is virtually non-existent, making Layer 4 ideal for database clusters (MySQL/Galera, PostgreSQL, Redis), SMTP/IMAP servers, and end-to-end encrypted TLS tunnels. - Layer 7 Load Balancing (
mode http): HAProxy buffers and deeply inspects the HTTP/1.1 and HTTP/2 protocol frames. It can read, inject, and rewrite request/response headers, evaluate URI paths, parse session cookies, terminate and offload SSL/TLS encryption, and redirect traffic dynamically based on complex Access Control Lists (ACLs). While Layer 7 routing incurs marginally more memory and CPU cycles per request, it unlocks fine-grained microservice routing, rate limiting, and intelligent security filtering.
Performance & Architectural Comparison Matrix
The comparative matrix below illustrates key performance characteristics, throughput capacities, and latency profiles across unoptimized defaults and production-tuned Layer 4 and Layer 7 deployments on enterprise Linux.
| Architecture Metric | Layer 4 (TCP Mode) | Layer 7 (HTTP Mode) | Unoptimized Default |
|---|---|---|---|
| Protocol Processing | Raw TCP Byte Stream (Zero payload parse) | Deep HTTP/1.1 & HTTP/2 Header Inspection | Single-Threaded Generic Buffer |
| Routing Decision Point | IP, Port, SNI (TLS Passthrough) | URI, Cookies, Headers, HTTP Method | Static Destination Port |
| Latency Overhead | < 0.15 ms per connection | 0.40 – 0.85 ms per request | 2.50 – 5.00 ms (Socket stalls) |
| Throughput (4-Core VM) | 140,000+ Concurrent Sockets | 65,000+ HTTP Req/sec | 8,500 Req/sec (File descriptor choke) |
| TLS / SSL Termination | Passthrough via SNI / Direct Routing | Offloaded Hardware Encryption & ALPN | Software Handshake Bottleneck |
| Health Check Granularity | SYN/ACK Handshake & Port Openness | HTTP Status Codes & Regex Payload Match | Passive Failure Drops |
Architecture Note: In modern high-throughput architectures, it is common practice to deploy a hybrid setup: HAProxy operates a Layer 4 frontend that inspects SNI to route non-HTTP protocols (e.g., Redis or database traffic) directly to dedicated backend clusters, while dispatching HTTPS traffic internally to an optimized Layer 7 frontend loop for deep header manipulation and SSL offloading.
Prerequisites & Linux Kernel Tuning for High Concurrency
Default Linux kernel networking parameters are calibrated for generic server workloads and desktop responsiveness, not edge proxies managing tens of thousands of simultaneous open sockets. If you launch HAProxy on an untuned Linux host, you will quickly encounter socket starvation, TIME_WAIT bucket exhaustion, and dropped SYN packets during traffic spikes.
Before installing HAProxy, configure the network subsystem by creating a custom kernel sysctl profile at /etc/sysctl.d/99-haproxy.conf. This file tunes socket allocation buffers, accelerates socket recycling, and widens the local ephemeral port range.
# /etc/sysctl.d/99-haproxy.conf
# Enterprise Linux Network Tuning for HAProxy High Concurrency

# Allow HAProxy to bind to non-local or virtual shared IP addresses (VIPs)
net.ipv4.ip_nonlocal_bind = 1
net.ipv6.ip_nonlocal_bind = 1

# Increase system-wide maximum open file descriptors
fs.file-max = 2097152

# Widen local ephemeral port range to prevent outbound port exhaustion
net.ipv4.ip_local_port_range = 10240 65535

# Enable fast recycling of TIME_WAIT sockets for outgoing connections
net.ipv4.tcp_tw_reuse = 1
net.ipv4.tcp_fin_timeout = 15

# Increase connection backlog queues to prevent dropped SYN packets
net.core.somaxconn = 65535
net.ipv4.tcp_max_syn_backlog = 65535
net.core.netdev_max_backlog = 65535

# Increase TCP memory limits (min, default, max in pages)
net.ipv4.tcp_rmem = 4096 87380 16777216
net.ipv4.tcp_wmem = 4096 65536 16777216

# Disable TCP slow start after idle to maintain high connection burst speed
net.ipv4.tcp_slow_start_after_idle = 0

# Protect against SYN flood attacks while maintaining handshake queues
net.ipv4.tcp_syncookies = 1
Apply these kernel parameters immediately without rebooting the server:
sudo sysctl --systemSystemd Service File Descriptor Limits
By default, systemd restricts processes to 1,024 open file descriptors. Because each client connection and backend proxy connection requires a separate file descriptor, an unconfigured service will crash under load. Create a systemd drop-in override to grant HAProxy enterprise-grade file descriptor limits:
# /etc/systemd/system/haproxy.service.d/override.conf
[Service]
LimitNOFILE=1048576
LimitNPROC=524288
TasksMax=infinity
Reload systemd and restart the service after configuring:
sudo systemctl daemon-reloadInstalling and Configuring HAProxy
On modern Debian/Ubuntu systems, install the latest official release directly from the stable repository. On enterprise distributions like RHEL, AlmaLinux, or Rocky Linux, use dnf:
# Debian / Ubuntu
sudo apt update && sudo apt install -y haproxy socat

# RHEL / AlmaLinux / Rocky Linux
sudo dnf install -y haproxy socat
HAProxy configuration resides in /etc/haproxy/haproxy.cfg. The configuration file is logically partitioned into four distinct sections: global (process-level security and threading), defaults (inherited timeouts and logging), frontend (client listeners and traffic admission), and backend (server pools, balancing algorithms, and health probes).
Production Configuration: /etc/haproxy/haproxy.cfg
The following configuration represents a complete, hardened production deployment featuring an administrative stats dashboard, a Layer 4 TCP load balancer for database nodes, and a Layer 7 HTTP/HTTPS reverse proxy with SSL termination and path-based routing:
# /etc/haproxy/haproxy.cfg
# Enterprise Production Configuration for TCP & HTTP Load Balancing

# ==============================================================================
# GLOBAL CONFIGURATION
# ==============================================================================
global
    log /dev/log local0 info
    log /dev/log local1 notice
    chroot /var/lib/haproxy
    user haproxy
    group haproxy
    daemon

    # Automatic multi-threading matching host CPU topology
    nbthread auto

    # Maximum concurrent connections allowed
    maxconn 100000

    # Runtime Administrative Socket for dynamic management
    stats socket /run/haproxy/admin.sock mode 660 level admin expose-fd listeners
    stats timeout 30s

    # Modern TLS Security & Cipher Suite Hardening
    ssl-default-bind-ciphers ECDHE-ECDSA-AES128-GCM-SHA256:ECDHE-RSA-AES128-GCM-SHA256:ECDHE-ECDSA-AES256-GCM-SHA384:ECDHE-RSA-AES256-GCM-SHA384:DHE-RSA-AES128-GCM-SHA256:DHE-RSA-AES256-GCM-SHA384
    ssl-default-bind-ciphersuites TLS_AES_128_GCM_SHA256:TLS_AES_256_GCM_SHA384:TLS_CHACHA20_POLY1305_SHA256
    ssl-default-bind-options ssl-min-ver TLSv1.2 no-tls-tickets

# ==============================================================================
# DEFAULTS CONFIGURATION
# ==============================================================================
defaults
    log     global
    mode    http
    option  httplog
    option  dontlognull
    retries 3

    # Connection and Transfer Timeouts
    timeout http-request    10s
    timeout queue           1m
    timeout connect         5s
    timeout client          50s
    timeout server          50s
    timeout http-keep-alive 10s
    timeout check           5s

# ==============================================================================
# STATS DASHBOARD (Protected Monitoring Interface)
# ==============================================================================
frontend stats_in
    bind 0.0.0.0:8404
    mode http
    stats enable
    stats uri /haproxy?stats
    stats refresh 10s
    stats auth admin:SuperSecretSysAdminPass2026!
    stats admin if TRUE

# ==============================================================================
# LAYER 4 (TCP) LOAD BALANCING - DATABASE CLUSTER (MySQL / Galera)
# ==============================================================================
frontend db_cluster_fe
    bind 0.0.0.0:3306
    mode tcp
    option tcplog
    default_backend db_cluster_be

backend db_cluster_be
    mode tcp
    balance leastconn
    # Native MySQL health check handshake
    option mysql-check user haproxy_check

    server db-node-01 10.0.2.11:3306 check inter 2000 fall 3 rise 2 weight 100
    server db-node-02 10.0.2.12:3306 check inter 2000 fall 3 rise 2 weight 100
    server db-standby 10.0.2.13:3306 check inter 2000 fall 3 rise 2 backup

# ==============================================================================
# LAYER 7 (HTTP / HTTPS) LOAD BALANCING - WEB & API TIERS
# ==============================================================================
frontend web_edge_fe
    # Bind HTTP and HTTPS with ALPN negotiation for HTTP/2
    bind 0.0.0.0:80
    bind 0.0.0.0:443 ssl crt /etc/haproxy/certs/site.pem alpn h2,http/1.1
    mode http

    # Enforce HTTPS Redirection
    http-request redirect scheme https unless { ssl_fc }

    # Client IP Preservation & Security Headers
    http-request set-header X-Forwarded-Proto https if { ssl_fc }
    http-request set-header X-Forwarded-Port %[dst_port]
    http-request add-header X-Forwarded-For %[src]

    # ACL Routing Rules
    acl is_api path_beg /api/ /v1/ /v2/
    acl is_static path_end -i .jpg .png .css .js .svg .woff2

    # Dynamic Backend Selection
    use_backend api_microservices_be if is_api
    default_backend web_static_be

backend web_static_be
    mode http
    balance roundrobin
    option httpchk GET /health HTTP/1.1\r\nHost:\ localhost
    http-check expect status 200
    cookie SERVERID insert indirect nocache

    server web-node-01 10.0.1.11:80 check cookie web01 inter 3000 fall 3 rise 2
    server web-node-02 10.0.1.12:80 check cookie web02 inter 3000 fall 3 rise 2
    server web-node-03 10.0.1.13:80 check cookie web03 inter 3000 fall 3 rise 2

backend api_microservices_be
    mode http
    balance leastconn
    option httpchk GET /api/health HTTP/1.1\r\nHost:\ localhost
    http-check expect status 200-299

    server api-node-01 10.0.1.21:8080 check inter 2000 fall 2 rise 3
    server api-node-02 10.0.1.22:8080 check inter 2000 fall 2 rise 3
Architecture Note: In the configuration above, notice the
cookie SERVERID insert indirect nocachedirective. This injects a sticky session cookie into client responses. Subsequent requests from that user stick to the exact same backend node, preventing session loss in stateful web applications without relying on brittle IP-hash algorithms.
Active Health Checking and Dynamic Failover Strategies
A resilient load balancer is only as effective as its health-checking mechanism. Relying on passive failure (waiting for a client connection to time out before evicting a dead server) degrades end-user latency. HAProxy supports proactive, granular health checking across both layers:
- TCP Health Checking (Layer 4): For raw TCP services, specifying
checkinitiates a basic 3-way TCP handshake. However, a database might have a listening socket open while experiencing internal thread pool exhaustion. HAProxy provides specialized protocol probes such asoption mysql-check,option pgsql-check, andoption redis-checkto authenticate and test internal daemon health. - HTTP Health Checking (Layer 7): By using
option httpchkalongsidehttp-check expect, HAProxy sends valid HTTP requests with specific Host headers and expects an exact 200 OK or regex status code. If an application throws an uncaught 500 Internal Server Error, HAProxy evicts the degraded node within milliseconds. - Threshold Parameters (
inter,fall,rise):inter 2000defines a 2-second check interval.fall 3requires 3 consecutive failed checks before evicting the server from the routing pool.rise 2requires 2 consecutive successful checks before restoring traffic, preventing flapping nodes from receiving traffic prematurely.
While HAProxy effortlessly juggles hundreds of thousands of concurrent connections, proxy performance is intrinsically bound to the compute density and raw I/O latency of the underlying infrastructure. Running heavy reverse proxies and stateful database backends on overloaded shared hosts inevitably induces jitter and packet drops. For mission-critical production workloads that demand uncompromised CPU core isolation, ultra-fast enterprise NVMe arrays, and LiteSpeed Web Server acceleration, migrating your backend nodes to MeraHost Enterprise Cloud guarantees zero noisy neighbors and a predictable cost structure backed by their Same Renewal Price, Always guarantee (starting at ₹99/mo).
Runtime Management via UNIX Socket
One of HAProxy’s most powerful enterprise features is its non-blocking runtime API, exposed via a local UNIX domain socket (/run/haproxy/admin.sock). This socket allows systems engineers and CI/CD pipelines to adjust server weights, put nodes into maintenance mode for zero-downtime rolling deployments, and query real-time traffic statistics without reloading or restarting the daemon.
Using the socat utility, you can dispatch commands directly to the socket:
# Drain traffic from a web node before upgrading code (graceful maintenance)
echo "set server web_static_be/web-node-01 state drain" | sudo socat stdio /run/haproxy/admin.sock

# Re-enable the node after the deployment is complete
echo "set server web_static_be/web-node-01 state ready" | sudo socat stdio /run/haproxy/admin.sock

# Dynamically adjust weight of a backend server on the fly
echo "set server web_static_be/web-node-02 weight 50%" | sudo socat stdio /run/haproxy/admin.sock

# Dump real-time CSV statistics for all frontends and backends
echo "show stat" | sudo socat stdio /run/haproxy/admin.sock
Validating Configuration and Seamless Reloads
Never reload HAProxy without performing an explicit syntax validation check. The -c flag parses the configuration file, verifies SSL certificate validity, and checks ACL logic:
# Validate configuration syntax
sudo haproxy -c -f /etc/haproxy/haproxy.cfg

# Execute a seamless, zero-downtime reload via systemd
sudo systemctl reload haproxy
Operations Note: When invoking
systemctl reload haproxy, HAProxy uses seamless socket transfer (the-xflag in modern versions). The parent process instantiates the new worker threads, passes listening file descriptors over a UNIX socket, and signals old workers to drain existing connections gracefully. Not a single incoming SYN packet is dropped.
Frequently Asked Questions (FAQ)
How do I preserve the original client IP address in Layer 4 TCP mode?
Because Layer 4 operates at the transport layer without modifying application headers (unlike HTTP X-Forwarded-For), backend servers will see HAProxy’s internal IP address by default. To preserve the client’s original IP, enable the PROXY Protocol in HAProxy by adding send-proxy or send-proxy-v2 to your backend server line (e.g., server s1 10.0.1.11:80 check send-proxy-v2). Ensure your backend service (such as Nginx, Apache, or MySQL) has PROXY protocol parsing enabled.
Which load balancing algorithm should I choose for web and API workloads?
For stateless HTTP web applications and microservices with varying request processing durations, balance leastconn is the optimal choice because it dynamically distributes incoming traffic to servers with the fewest active connections. For short, uniform static asset delivery, balance roundrobin performs exceptionally well. If your application relies on local server-side state or user sessions, use balance source or pair roundrobin with cookie-based persistence (cookie SERVERID insert indirect nocache).
How does HAProxy ensure zero-downtime reloads during configuration updates?
HAProxy achieves zero-downtime reloads via seamless file descriptor transfer over a UNIX socket. When you execute systemctl reload haproxy, the system starts a new HAProxy process that takes over listening sockets from the old process before binding. The old process ceases accepting new connections, allows in-flight transactions to conclude gracefully, and terminates once its active connection table hits zero.
Can HAProxy terminate SSL certificates and support HTTP/2 simultaneously?
Yes. By binding the frontend to port 443 with the ssl crt /path/to/cert.pem directive and defining alpn h2,http/1.1, HAProxy natively negotiates HTTP/2 for supporting clients while gracefully falling back to HTTP/1.1 for legacy user agents. HAProxy compiles against OpenSSL or LibreSSL, leveraging AES-NI hardware CPU instructions for ultra-fast, low-overhead cryptographic operations.
Deploy Enterprise-Grade Production Infrastructure
Need guaranteed performance with zero price hikes? Host mission-critical workloads on MeraHost with pure Enterprise NVMe, LiteSpeed Web Server, and Same Renewal Price, Always (starting at ₹99/mo).