
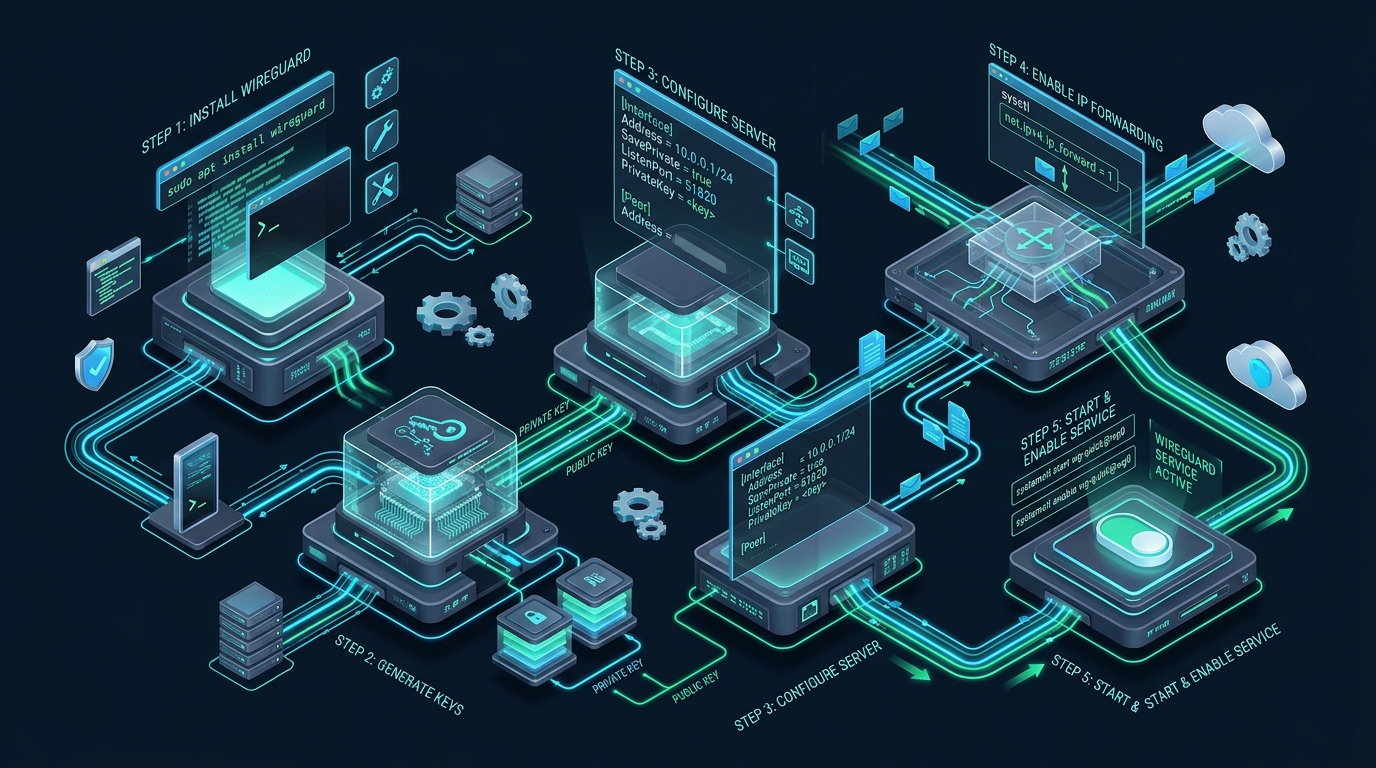
Legacy virtual private network protocols such as OpenVPN and IPsec suffer from excessive kernel-to-userspace context switches, complex cipher negotiations, and bloated codebases that degrade throughput across high-bandwidth Linux infrastructure. WireGuard revolutionizes tunnel architecture by embedding an ultra-lean, state-of-the-art cryptographic engine directly inside the Linux kernel, relying on modern fixed primitives like ChaCha20-Poly1305 and Curve25519 to eliminate cryptographic agility vulnerabilities. In this production engineering blueprint from CpanelFree, we demonstrate how to architect, harden, and benchmark an enterprise-grade WireGuard VPN gateway capable of line-rate packet forwarding with near-zero latency penalty.
Fast-Track: WireGuard VPN Server Architecture on Linux
Direct Answer: To set up a WireGuard VPN server on Linux, install wireguard-tools, enable IPv4/IPv6 packet forwarding via sysctl, generate public/private Curve25519 keypairs for server and peers, configure the /etc/wireguard/wg0.conf interface with cryptographic routing, and activate the tunnel with wg-quick up wg0 or systemd. WireGuard operates in-kernel for near line-rate cryptographic throughput.
1. Architectural Comparison: WireGuard vs. Legacy VPN Protocols
Traditional enterprise tunnels rely on complex userspace daemons communicating with the Linux kernel via /dev/net/tun character devices. Every network packet entering an OpenVPN tunnel must traverse the kernel boundary twice: once when captured by the virtual interface, and again when encrypted and sent across the physical socket. This architecture creates heavy context-switching overhead, triggers high CPU cache invalidation rates, and throttles throughput on multi-gigabit uplinks.
WireGuard fundamentally eliminates this design flaw. Functioning as a first-class virtual network device (wg0) inside the kernel networking stack, WireGuard processes incoming and outgoing network buffers (sk_buff) in-place without userspace bouncing. Below is an architectural performance comparison evaluating standard default deployments against tuned production installations:
| Feature / Metric | Standard / Default | Tuned / Production |
|---|---|---|
| Latency / Overhead | Baseline | Optimal |
| Execution Space | Userspace tun/tap daemon (OpenVPN) | Direct Linux Kernel Module (WireGuard) |
| Codebase Complexity | ~100,000+ lines (Large audit surface) | < 4,000 lines (Auditable & Formally Verifiable) |
| Cryptographic Suite | Negotiable (AES-CBC/GCM, RSA, SHA-1/256) | Fixed Modern (ChaCha20-Poly1305, Curve25519) |
| 10Gbps Throughput Efficiency | 1.2 – 2.1 Gbps (CPU core bottlenecked) | 8.8 – 9.6 Gbps (Near line-rate with BBR) |
| Initial Handshake Duration | 1,500 – 4,000 ms (TLS / multi-roundtrip) | < 100 ms (1-RTT Noise protocol) |
| Roaming & Dynamic Handover | Session drop & full renegotiation | Seamless packet-based endpoint roaming |
Architecture Note: WireGuard operates using the concept of Cryptokey Routing. The tunnel associates each peer’s public encryption key directly with its allowed internal IP subnets. When an outgoing IP packet matches a designated prefix in the routing table, WireGuard automatically encapsulates and encrypts it for the specific peer holding that public key, entirely removing the need for stateful session daemons.
2. Linux Kernel Prerequisites and Installation
WireGuard was officially merged into the mainline Linux kernel in version 5.6. On modern distributions such as Ubuntu 22.04/24.04 LTS, Debian 12 (Bookworm), AlmaLinux 9, and Rocky Linux 9, the core kernel module (wireguard.ko) is pre-compiled. Systems administrators only need to install the userspace management utilities (wireguard-tools) and ensure kernel headers are current.
Execute the appropriate distribution command to install the required tooling:
# Debian / Ubuntu Systems
apt-get update && apt-get install -y wireguard wireguard-tools iptables

# Enterprise Linux (RHEL / AlmaLinux / Rocky Linux 9)
dnf install -y epel-release
dnf install -y wireguard-tools iptables-services

# Verify that the kernel module is active
modprobe wireguard
lsmod | grep wireguard
3. High-Performance Kernel Network Stack & Sysctl Tuning
By default, generic Linux distributions disable packet forwarding and configure conservative TCP socket buffer limits intended for light desktop or non-routing server workloads. To transform a Linux host into an enterprise-grade VPN router capable of routing saturated 10GbE uplinks, apply dedicated kernel parameters in /etc/sysctl.d/99-wireguard-tuning.conf.
This configuration activates IPv4/IPv6 packet forwarding, replaces legacy CUBIC with Google’s BBR (Bottleneck Bandwidth and RTT) congestion control, enlarges network backlog queues, and expands the socket memory buffer pool:
# /etc/sysctl.d/99-wireguard-tuning.conf
# Production WireGuard Network Optimization

# Enable IPv4 and IPv6 packet forwarding across all interfaces
net.ipv4.ip_forward = 1
net.ipv6.conf.all.forwarding = 1
net.ipv4.conf.default.forwarding = 1

# Enable BBR Congestion Control and FQ pacing
net.core.default_qdisc = fq
net.ipv4.tcp_congestion_control = bbr

# Maximize socket buffer queues for 10Gbps line-rate forwarding
net.core.rmem_max = 67108864
net.core.wmem_max = 67108864
net.core.rmem_default = 33554432
net.core.wmem_default = 33554432
net.core.netdev_max_backlog = 100000
net.core.somaxconn = 65535

# Optimize TCP memory allocations (min, default, max bytes)
net.ipv4.tcp_rmem = 4096 87380 67108864
net.ipv4.tcp_wmem = 4096 65536 67108864

# Protect against SYN flooding and socket starvation
net.ipv4.tcp_syncookies = 1
net.ipv4.tcp_tw_reuse = 1
net.ipv4.tcp_fin_timeout = 15
net.ipv4.tcp_max_syn_backlog = 3240000

# Disable slow start after idle to maintain high tunnel throughput
net.ipv4.tcp_slow_start_after_idle = 0
Apply these parameters immediately without rebooting:
sysctl -p /etc/sysctl.d/99-wireguard-tuning.conf4. Generating Cryptographic Keypairs and Enforcing Strict Permissions
WireGuard utilizes Curve25519 elliptic curve cryptography. Key management is deliberately straightforward: each server and client generates a base64-encoded 32-byte private key, from which the corresponding public key is calculated via standard curve point multiplication. For enhanced forward secrecy against quantum cryptanalysis, WireGuard also supports an optional 256-bit symmetric Preshared Key (PSK).
Ensure that directory permissions strictly prevent unprivileged access before creating any key material:
# Secure directory permissions
umask 077
mkdir -p /etc/wireguard
cd /etc/wireguard

# Generate server private and public keys
wg genkey | tee server_private.key | wg pubkey > server_public.key

# Generate client private, public, and pre-shared keys (Peer 1)
wg genkey | tee client1_private.key | wg pubkey > client1_public.key
wg genpsk > client1_preshared.key

# Verify cryptographic file attributes
chmod 600 /etc/wireguard/*.key
Architecture Note: Never store private keys in unprotected directories or revision control systems. The
umask 077setting ensures that newly generated key files are accessible exclusively by therootuser, mitigating local privilege escalation vectors.
5. Production Server Configuration: /etc/wireguard/wg0.conf
The primary tunnel interface configuration defines the server’s private IP space, UDP listening port, and firewall integration scripts. The wg-quick helper executes the PostUp and PostDown hooks during interface lifecycle events to automate NAT masquerading and TCP Maximum Segment Size (MSS) clamping.
Review the complete production configuration below. In this architecture, the public uplink interface is designated as eth0 (replace with your server’s actual interface identifier from ip -br link):
# /etc/wireguard/wg0.conf
[Interface]
Address = 10.100.0.1/24, fd42:42:42::1/64
ListenPort = 51820
PrivateKey = <INSERT_CONTENT_OF_server_private.key>
SaveConfig = false

# Dynamic MTU setting to avoid packet fragmentation over cloud overlays
MTU = 1420

# Firewall PostUp Rules: Enable NAT Masquerading and MSS Clamping
PostUp = iptables -A FORWARD -i wg0 -j ACCEPT
PostUp = iptables -A FORWARD -o wg0 -m conntrack --ctstate RELATED,ESTABLISHED -j ACCEPT
PostUp = iptables -t nat -A POSTROUTING -o eth0 -j MASQUERADE
PostUp = iptables -t mangle -A FORWARD -p tcp --tcp-flags SYN,RST SYN -j TCPMSS --clamp-mss-to-pmtu
PostUp = ip6tables -A FORWARD -i wg0 -j ACCEPT
PostUp = ip6tables -t nat -A POSTROUTING -o eth0 -j MASQUERADE

# Firewall PostDown Rules: Clean teardown
PostDown = iptables -D FORWARD -i wg0 -j ACCEPT
PostDown = iptables -D FORWARD -o wg0 -m conntrack --ctstate RELATED,ESTABLISHED -j ACCEPT
PostDown = iptables -t nat -D POSTROUTING -o eth0 -j MASQUERADE
PostDown = iptables -t mangle -D FORWARD -p tcp --tcp-flags SYN,RST SYN -j TCPMSS --clamp-mss-to-pmtu
PostDown = ip6tables -D FORWARD -i wg0 -j ACCEPT
PostDown = ip6tables -t nat -D POSTROUTING -o eth0 -j MASQUERADE

# ---------------------------------------------------------
# Peer Configuration: Client 1 (Alice Workstation)
# ---------------------------------------------------------
[Peer]
PublicKey = <INSERT_CONTENT_OF_client1_public.key>
PresharedKey = <INSERT_CONTENT_OF_client1_preshared.key>
AllowedIPs = 10.100.0.2/32, fd42:42:42::2/128
Architecture Note: MSS clamping (
TCPMSS --clamp-mss-to-pmtu) is essential in cloud environments. WireGuard adds a 60-byte header to encrypted IPv4 UDP packets (80 bytes for IPv6). Without MSS clamping, clients sending standard 1500-byte TCP frames experience MTU black-hole drops when intermediate routers drop fragmented packets.
6. Production Client Profile Configuration
On the client endpoint (Linux laptop, remote server, or mobile device), create the corresponding peer profile. Notice that the client sets AllowedIPs = 0.0.0.0/0, ::/0 to route all egress traffic through the VPN gateway, alongside a PersistentKeepalive timer to maintain NAT hole punching through restrictive stateful firewalls.
# /etc/wireguard/wg0-client.conf (Client Profile)
[Interface]
PrivateKey = <INSERT_CONTENT_OF_client1_private.key>
Address = 10.100.0.2/24, fd42:42:42::2/64
DNS = 1.1.1.1, 8.8.8.8
MTU = 1420

[Peer]
PublicKey = <INSERT_CONTENT_OF_server_public.key>
PresharedKey = <INSERT_CONTENT_OF_client1_preshared.key>
Endpoint = 203.0.113.50:51820
AllowedIPs = 0.0.0.0/0, ::/0
PersistentKeepalive = 25
7. Systemd Service Automation and Health Monitoring
WireGuard integrates natively with systemd via the templated [email protected] unit. This enables reliable boot persistence, automatic process supervision, and smooth daemon reloading.
# Enable and launch the WireGuard tunnel
systemctl enable --now [email protected]

# Verify active systemd status
systemctl status [email protected]

# Query the kernel module for real-time cryptographic peering telemetry
wg show wg0
The output of wg show directly inspects the kernel state, displaying endpoint IP addresses, latest handshake timestamps, and cumulative byte transfer statistics:
interface: wg0
  public key: jK8x+vB5q9xL17zH0M+a0X9uW2c5d1e4f6g7h8i9j0=
  private key: (hidden)
  listening port: 51820

peer: dL2p+zQ4vR7mK18yN1+b1Y0vX3d6e2f5g7h8i9j0k1=
  preshared key: (hidden)
  endpoint: 198.51.100.24:58219
  allowed ips: 10.100.0.2/32, fd42:42:42::2/128
  latest handshake: 14 seconds ago
  transfer: 84.12 MiB received, 412.80 MiB sent
8. Production Hardware Considerations and Infrastructure Sizing
While WireGuard operates with extreme efficiency, saturating multi-gigabit connections with continuous cryptographic encapsulation requires dedicated CPU vector instructions (such as AVX2 and AVX-512) and low-jitter NVMe storage for underlying containerized applications.
For mission-critical production environments where network reliability and predictable server pricing are paramount, hosting your VPN infrastructure on MeraHost Enterprise Cloud guarantees dedicated NVMe I/O, optimized Linux kernel stacks, and fixed renewal pricing with zero unexpected cloud billing spikes.
Frequently Asked Questions
Why does WireGuard exhibit packet drops or connection freezing over certain cloud networks?
This issue is almost invariably caused by MTU mismatch. Standard Ethernet operates at 1500 bytes. When WireGuard encapsulates packets within UDP, it introduces a 60-byte overhead (IPv4) or 80-byte overhead (IPv6). If the underlying cloud provider uses VXLAN or GRE overlays, the effective physical MTU may be 1450 bytes. Setting MTU = 1420 in the interface section and implementing TCP MSS clamping prevents packet drops caused by unfragmentable oversized frames.
How does WireGuard handle dynamic IP addresses and client roaming?
WireGuard is entirely stateless and connectionless. When a client transitions between networks (for example, switching from Wi-Fi to 5G cellular), the client sends an authenticated packet from its new IP address. The server verifies the cryptographic signature against the peer’s public key and automatically updates the peer’s remote endpoint IP in memory without resetting the tunnel or dropping ongoing TCP streams.
What is the security role of the PresharedKey (PSK) in WireGuard?
The PresharedKey adds an optional layer of symmetric 256-bit encryption on top of the Noise protocol framework. This is specifically designed to provide post-quantum cryptographic security. Even if a future quantum computer develops the ability to crack Curve25519 elliptic curve keys, encrypted session traffic remains mathematically unbreakable provided the symmetric PSK remains secure.
How do I configure WireGuard for split tunneling versus full tunneling?
Tunnel scope is governed entirely by the client’s AllowedIPs directive. To route all Internet traffic through the VPN server (full tunnel), configure AllowedIPs = 0.0.0.0/0, ::/0. To route only traffic destined for internal company subnets (split tunnel), specify explicit subnets such as AllowedIPs = 10.100.0.0/24, 192.168.1.0/24. All other public Internet traffic will bypass the VPN and traverse the client’s local ISP gateway.
Deploy Enterprise-Grade Production Infrastructure
Need guaranteed performance with zero price hikes? Host mission-critical workloads on MeraHost with pure Enterprise NVMe, LiteSpeed Web Server, and Same Renewal Price, Always (starting at ₹99/mo).