
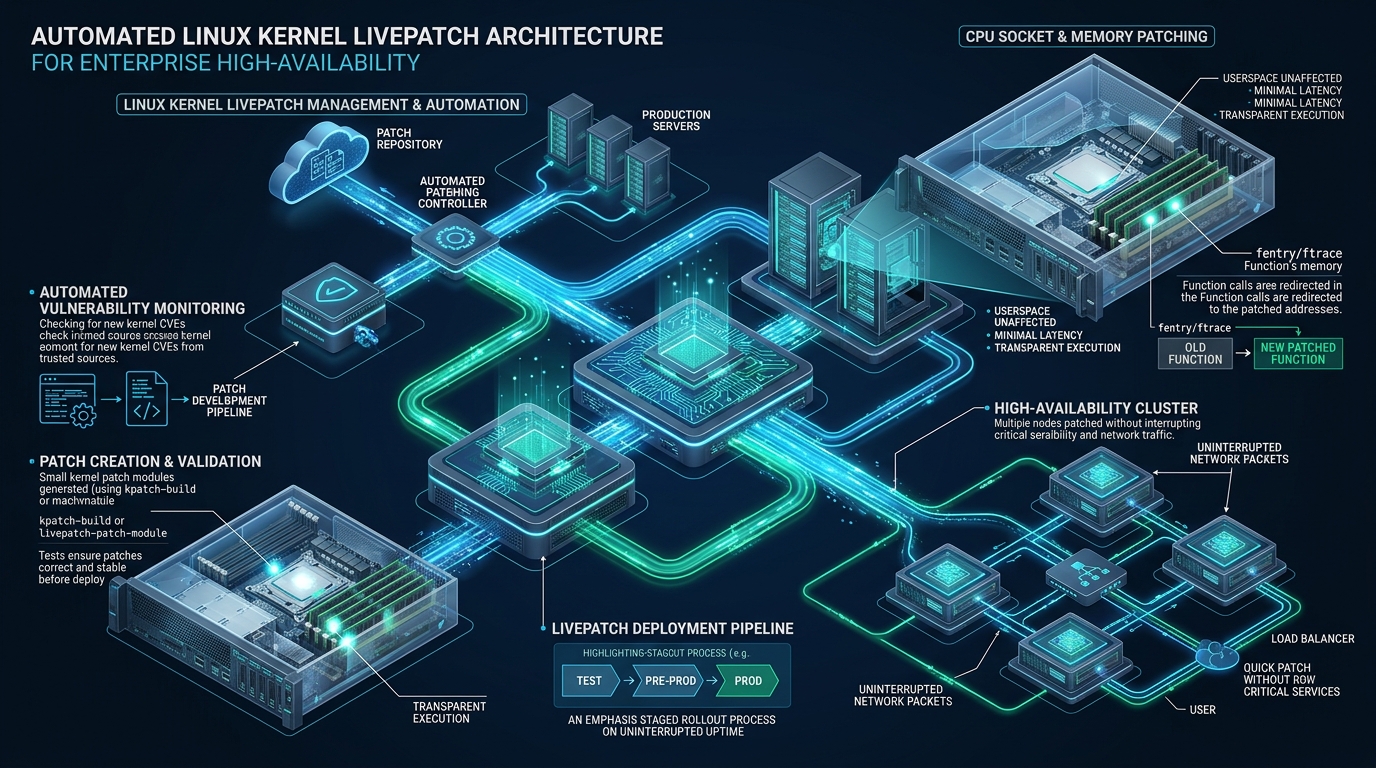
In the 2026 enterprise landscape, the concept of a ‘maintenance window’ has become an architectural relic. As global workloads demand 100% uptime, the linux kernel livepatch architecture has evolved from a niche experimental feature into a mandatory pillar of high-availability infrastructure, allowing sysadmins to remediate critical CVEs without a single second of service interruption. Explore more advanced infrastructure strategies at Mera Blogger.
The Architectural Shift: From Reboots to Runtime Redirection
Historically, patching a Linux kernel required a full system reboot to load the new binary into memory. In a distributed microservices environment, even a 5-minute reboot can trigger cascading failures, load balancer health-check flaps, and state synchronization issues. The modern linux kernel livepatch architecture solves this by utilizing the ftrace infrastructure to redirect function calls from vulnerable code to patched code in real-time.
The core mechanism relies on the livepatch subsystem (introduced in kernel 4.0 and matured significantly by 2026). When a patch is applied, the kernel doesn’t replace the entire image; instead, it loads a specialized kernel module containing the fixed function and uses a redirection pointer. This process is governed by a consistency model that ensures no process is currently executing the function being patched, preventing race conditions and memory corruption.
Implementing the Kpatch Workflow
For enterprise environments running RHEL, Ubuntu Pro, or Debian, the kpatch toolset is the industry standard for generating patch modules. The workflow involves taking a source code diff, the original kernel source, and the current configuration to compile a binary-to-binary comparison.
1. Environment Preparation
To begin, you must ensure your build node matches the target production node’s kernel version exactly. Install the necessary development headers and the kpatch-build utility.
# Install kpatch dependencies on a build server
sudo apt-get install kpatch kpatch-build build-essential libelf-dev

# Verify the running kernel supports livepatching
grep CONFIG_LIVEPATCH /boot/config-$(uname -r)
# Expected output: CONFIG_LIVEPATCH=y
2. Generating the Patch Module
Once you have your .patch file (e.g., a fix for a memory leak in the networking stack), you generate the kernel module that will perform the live redirection.
# Generate the livepatch module
kpatch-build -t vmlinux fix-network-leak.patch

# This creates a .ko (kernel object) file
# Example: kpatch-fix-network-leak.ko
Automating Deployment via Systemd
In a 2026 production environment, manual insmod commands are unacceptable. We utilize systemd units to ensure that livepatches are applied automatically upon boot and managed as first-class services. This ensures that even if a server is eventually rebooted, the livepatch is reapplied before the vulnerable code can be exploited.
[Unit]
Description=Apply Critical Kernel Livepatch for CVE-2026-XXXX
After=network.target

[Service]
Type=oneshot
RemainAfterExit=yes
ExecStart=/usr/bin/kpatch load /var/lib/kpatch/kpatch-fix-network-leak.ko
ExecStop=/usr/bin/kpatch unload /var/lib/kpatch/kpatch-fix-network-leak.ko
StandardOutput=journal

[Install]
WantedBy=multi-user.targetdmesg errors or performance degradation for 30 minutes, then roll out to the remaining 95%.Monitoring and Verification
The /sys/kernel/livepatch directory is the source of truth for the current state of applied patches. Enterprise monitoring tools like Prometheus or Zabbix should be configured to scrape this directory to ensure compliance across the fleet.
# Check the status of applied patches
cat /sys/kernel/livepatch/*/enabled

# Verify the transition state (0 = complete, 1 = in progress)
cat /sys/kernel/livepatch/*/transition
If the transition hangs at 1, it usually means a process is stuck in a system call within the function being patched. In 2026, modern kernels use ‘forced transition’ signals to nudge these processes into a safe state, but manual intervention may occasionally be required for legacy applications.
Frequently Asked Questions
Does livepatching impact system performance?
The performance overhead is negligible (typically < 1%). Since it uses ftrace's mcount/nop mechanism, the redirection is a simple jump instruction. However, patching extremely high-frequency functions in the scheduler or memory allocator should be done with caution.
Can I stack multiple livepatches?
Yes. The Linux kernel supports stacking multiple patches. Each new patch for the same function will take precedence. It is recommended to consolidate patches into a single cumulative module during monthly maintenance cycles to reduce complexity.
What happens if a livepatch fails to apply?
The livepatch subsystem is designed to be atomic. If the consistency model cannot be satisfied (e.g., a process never leaves the target function), the patch will remain in a ‘pending’ state and eventually time out, reverting the system to the unpatched state without crashing.
Ready for Zero-Downtime Infrastructure?
Don’t let security updates compromise your availability. Deploy your next-generation enterprise workloads on our high-performance Cloud VPS and leverage our pre-configured kernel optimization stacks.