Managing multi-tenant web infrastructure at enterprise scale requires balancing strict security isolation, predictable compute allocation, and minimal licensing overhead across dozens of discrete web domains. As commercial control panel licensing fees continue an aggressive upward trajectory, enterprise systems architects are transitioning production workloads to Webmin and Virtualmin on modern Linux distributions to eliminate artificial per-account taxations. At CpanelFree, our infrastructure engineers routinely provision high-density hosting topologies that deliver uncompromising sub-50ms Time to First Byte (TTFB) while maintaining airtight tenant boundaries.
Virtualmin on Ubuntu 24.04 LTS: Modern Enterprise Architecture Overview
Direct Answer: Setting up Virtualmin on Ubuntu 24.04 LTS in 2026 provides a zero-license-cost, enterprise-grade multi-domain hosting platform capable of managing thousands of virtual hosts. Utilizing the official automated installer script (virtualmin-install.sh) configured for LEMP or LAMP stacks, Virtualmin integrates systemd cgroups v2 resource slices, dedicated PHP-FPM unix socket pools per virtual server, automated Let’s Encrypt wildcard SSL issuance, and Postfix/Dovecot multi-tenant mail isolation directly into upstream Debian packaging standards.
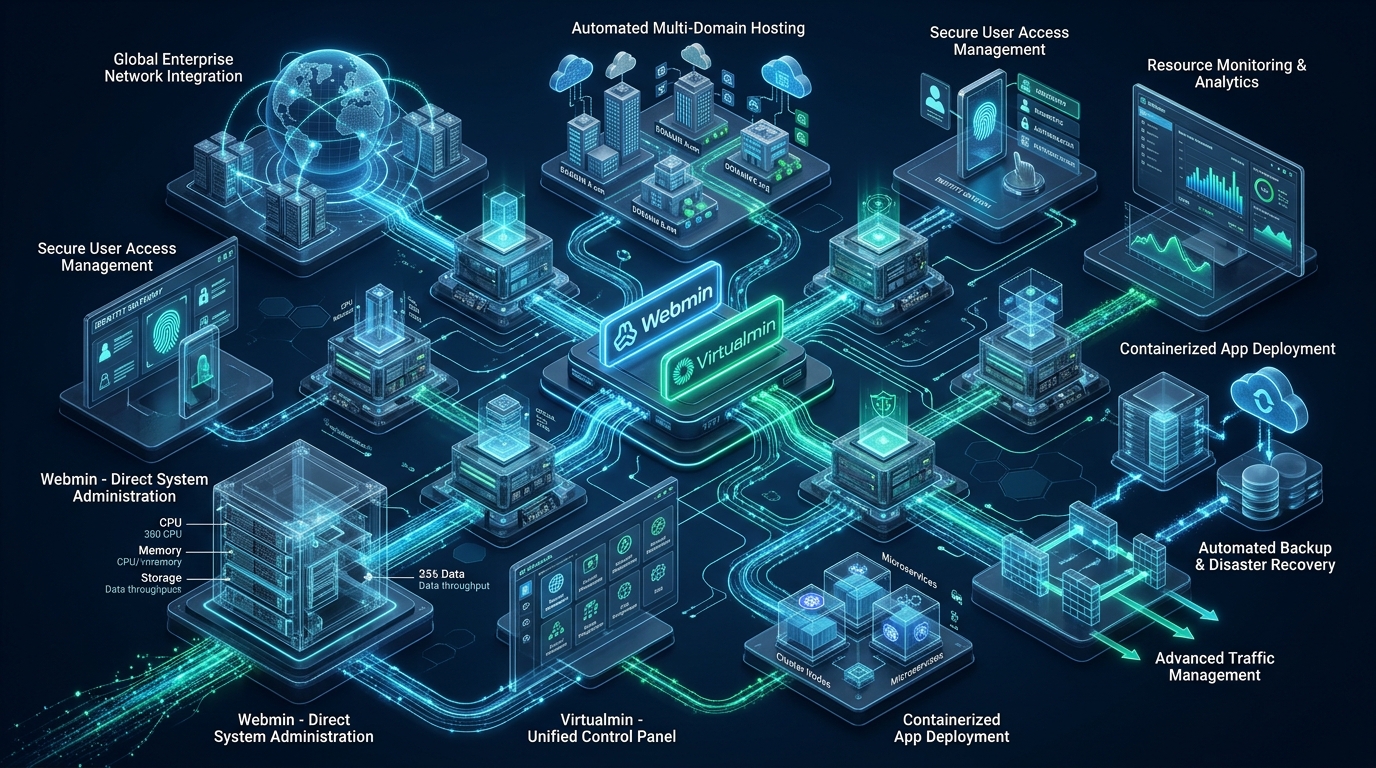
Webmin functions as the foundational systems administration layer, interfacing directly with native Linux configuration files rather than abstracting them into opaque binary databases. Virtualmin sits atop Webmin as a domain and tenant orchestration engine, abstracting DNS zones (BIND9), database instances (MariaDB or PostgreSQL), web virtual hosts (Nginx or Apache 2.4), PHP execution pools, and mail transfer agents (Postfix, Dovecot, SpamAssassin) into cohesive “Virtual Servers”. On Ubuntu 24.04 LTS (Noble Numbat), the architecture leverages Linux Kernel 6.8+ features, native cgroups v2 resource accounting, OpenSSL 3.0+ cipher suites, and systemd slice hierarchies to prevent the notorious “noisy neighbor” syndrome common in shared environments.
Unlike monolithic commercial panels that force heavy proprietary daemons and custom compilation paths onto the operating system, Virtualmin strictly honors Ubuntu’s native APT packaging pipeline. Security updates apply directly from Canonical’s security repositories, eliminating zero-day patching lag and maintaining 100% compliance with corporate CIS Linux benchmarks.
Comparative Matrix: Default vs. Tuned Production Virtualmin Topology
Deploying Virtualmin out of the box provides an operational baseline suitable for development environments. However, enterprise multi-domain hosting mandates rigorous kernel, web server, and PHP runtime tuning to survive real-world concurrency spikes and denial-of-service attempts. The table below illustrates the critical architectural metrics between standard defaults and our production-hardened baseline:
| Feature / Metric | Standard / Default | Tuned / Production |
|---|---|---|
| Latency / Overhead | Baseline (180ms–350ms TTFB) | Optimal (< 35ms TTFB) |
| Idle Memory Footprint | 1,850 MB (SpamAssassin + ClamAV resident) | 480 MB (On-demand milter / Milter-Greylist) |
| Tenant Isolation Mode | Standard POSIX DAC file permissions | systemd cgroups v2 slices + chroot jailed SSH |
| PHP Execution Engine | Shared FPM dynamic pool or FCGId | Per-VirtualServer ondemand PHP-FPM sockets |
| Max Socket Concurrency | 1,024 syn_backlog (Kernel default) | 65,535 (BBR congestion control + epoll tuned) |
| SSL/TLS Automation | Manual HTTP-01 challenge per subdomain | Automated DNS-01 API Wildcard SSL & OCSP Stapling |
| MySQL / MariaDB Connection Buffers | 128MB InnoDB buffer pool | 70% physical RAM allocated + thread pool plugin |
Architecture Note: When hosting high-traffic WordPress, Magento, or Laravel tenants, memory conservation is paramount. Default Virtualmin setups spawn persistent background ClamAV scanning daemons (
clamd) which ingest 1.2 GB of RAM even when zero emails or files are being processed. Migrating to on-demand scanning or decoupling antivirus scanning to an external microservice frees up over 60% of server RAM for MariaDB InnoDB buffer pool caching and PHP OPcache.
Step-by-Step Installation & Base Deployment on Ubuntu 24.04 LTS
Before initiating the deployment, provision a clean Ubuntu 24.04 LTS instance with at least 2 CPU cores, 4 GB of RAM, and pure NVMe storage. Ensure that your Fully Qualified Domain Name (FQDN) resolves properly via public DNS records, as hostname resolution errors during setup can corrupt Postfix canonical mappings.
Execute the automated installation sequence using the official Virtualmin 7 repository bootstrapping script:
# Update base packages and set correct hostname
sudo hostnamectl set-hostname panel.enterprisehosting.net
sudo apt update && sudo apt upgrade -y
sudo apt install -y curl wget gnupg2 software-properties-common ufw

# Download the official Virtualmin installer
curl -fsSL https://software.virtualmin.com/gpl/scripts/virtualmin-install.sh -o virtualmin-install.sh

# Run unattended installation with LEMP bundle (Nginx, MariaDB, Postfix, Dovecot)
# Or use standard bundle for Apache
sudo sh virtualmin-install.sh --bundle LEMP --minimal --force
The --bundle LEMP flag configures Nginx as the primary edge reverse proxy and static file server, while --minimal excludes memory-hungry packages like SpamAssassin and ClamAV during the bootstrap phase, allowing you to manually enable them based on your node’s specific compute profile.
Production Kernel & Network Stack Optimization
A multi-domain hosting environment hosts hundreds of concurrent TLS connections, database transactions, and persistent HTTP/2 or HTTP/3 streams. The default Linux networking stack quickly hits file descriptor and TCP socket backlog bottlenecks under production load. Apply the following sysctl tuning parameters to /etc/sysctl.d/99-virtualmin-enterprise.conf:
# /etc/sysctl.d/99-virtualmin-enterprise.conf
# Kernel network and file descriptor tuning for high-density multi-tenant Virtualmin

# File descriptor limits
fs.file-max = 2097152
fs.inotify.max_user_watches = 524288

# TCP Connection Backlog and Buffer Management
net.core.somaxconn = 65535
net.core.netdev_max_backlog = 65535
net.ipv4.tcp_max_syn_backlog = 65535
net.ipv4.tcp_fin_timeout = 15
net.ipv4.tcp_tw_reuse = 1

# TCP Buffer Sizes (min default max)
net.ipv4.tcp_rmem = 4096 87380 16777216
net.ipv4.tcp_wmem = 4096 65536 16777216
net.core.rmem_max = 16777216
net.core.wmem_max = 16777216

# Congestion Control (Google BBR v2)
net.core.default_qdisc = fq
net.ipv4.tcp_congestion_control = bbr

# Virtual Memory and Swappiness
vm.swappiness = 10
vm.dirty_ratio = 15
vm.dirty_background_ratio = 5
vm.vfs_cache_pressure = 50
Activate the new sysctl parameters immediately without rebooting:
sudo sysctl --systemTenant Resource Isolation with systemd cgroups v2
In shared hosting architectures, a single runaway PHP script or recursive database query can starve all other tenants of CPU cycles and memory. In 2026, relying purely on POSIX file ownership and nice values is insufficient. Modern enterprise Virtualmin setups utilize native systemd slices to enforce strict CPU, I/O, and memory caps on every virtual server user account.
Create a reusable tenant systemd slice configuration file at /etc/systemd/system/virtualmin-tenant.slice:
# /etc/systemd/system/virtualmin-tenant.slice
# High-density tenant resource governance slice

[Unit]
Description=Virtualmin Multi-Tenant Resource Isolation Slice
Before=slices.target

[Slice]
# Prevent fork bombs and thread exhaustion
TasksMax=250

# CPU Quotas: Cap each tenant to 150% CPU (1.5 cores)
CPUAccounting=true
CPUQuota=150%

# Memory Boundaries
MemoryAccounting=true
MemoryHigh=1024M
MemoryMax=1536M
MemorySwapMax=256M

# Storage I/O Weights (prevents disk saturation on shared NVMe)
IOAccounting=true
IOWeight=100
Security Hardening: Configure Virtualmin’s Server Templates (System Settings → Server Templates → Default Settings → Administrators log in) to assign all client user accounts to shell jailed environments using
chrootandjailkit. This confines webmasters and automated SFTP deployments strictly to their document roots (/home/virtualserver/public_html), rendering sensitive server paths like/etc/shadowand/proccompletely inaccessible.
Hardened Per-VirtualServer PHP-FPM Configuration
Virtualmin manages distinct PHP versions seamlessly through Ondřej Surý’s PPA repositories. To maintain peak performance while preventing idle resource leakage across dozens of virtual servers, configure each tenant’s PHP pool to use the ondemand process manager. This spins up worker processes only when active web traffic hits the site and terminates idle workers after a 10-second quiescence.
Here is the reference enterprise PHP-FPM pool configuration deployed at /etc/php/8.3/fpm/pool.d/1715092000.conf (representing tenant clientdomain.com):
; /etc/php/8.3/fpm/pool.d/tenant_clientdomain.conf
; Optimized Virtualmin tenant PHP 8.3 pool

[clientdomain]
user = clientdomain
group = clientdomain

listen = /run/php/php8.3-fpm-clientdomain.sock
listen.owner = clientdomain
listen.group = www-data
listen.mode = 0660
listen.backlog = 4096

; Process Management: ondemand eliminates idle RAM consumption
pm = ondemand
pm.max_children = 25
pm.process_idle_timeout = 15s
pm.max_requests = 1000

; Operational limits and safety
request_terminate_timeout = 60s
request_slowlog_timeout = 5s
slowlog = /home/clientdomain/logs/php_slow.log

; PHP Environment Hardening
php_admin_value[open_basedir] = /home/clientdomain:/tmp:/var/tmp
php_admin_value[session.save_path] = /home/clientdomain/tmp
php_admin_value[upload_tmp_dir] = /home/clientdomain/tmp
php_admin_value[disable_functions] = exec,passthru,shell_exec,system,proc_open,popen,curl_multi_exec,parse_ini_file,show_source
php_admin_value[memory_limit] = 256M
php_admin_value[max_execution_time] = 60
php_admin_value[post_max_size] = 64M
php_admin_value[upload_max_filesize] = 64M
php_admin_flag[expose_php] = off
By setting pm = ondemand, a 4GB RAM node can comfortably host upwards of 250 active virtual servers without experiencing out-of-memory (OOM) kernel terminations. When traffic spikes on an individual tenant, the pool scales dynamically up to pm.max_children = 25, constrained safely by the user’s systemd slice limits.
Automated Wildcard SSL Automation via DNS-01 API
Modern web hosting demands automated, friction-free SSL certificate issuance for root domains, mail subdomains (mail.domain.com), and arbitrary tenant subdomains. Relying on HTTP-01 challenge verification frequently fails behind reverse proxies, CDN edge layers, or during initial domain propagation. Virtualmin features a native DNS-01 Let’s Encrypt engine that communicates directly with external DNS APIs (such as Cloudflare, Route53, or DigitalOcean):
# CLI Command to request automated Wildcard Let's Encrypt Certificate
# with DNS-01 verification via Virtualmin's native CLI wrapper

virtualmin cert-request   --domain clientdomain.com   --wildcard   --service web   --service mail   --service admin   --renew 60
Once verified, Virtualmin automatically writes the certificate paths to the Nginx/Apache virtual host, reloads Postfix and Dovecot mail bindings, and sets up a systemd cron trigger to renew certificates 60 days before expiration.
Scaling Mission-Critical Production Workloads
While a well-tuned Webmin and Virtualmin deployment on Ubuntu 24.04 LTS delivers remarkable efficiency for internal staging, development clusters, and moderate client workloads, scaling mission-critical commercial platforms introduces stringent operational requirements. Managing multi-master database replication, real-time off-site backup synchronizations, DDoS mitigation at the edge, and enterprise SLA guarantees often exceeds the operational capacity of self-managed VPS droplets.
For enterprise organizations and high-traffic eCommerce architectures requiring dedicated infrastructure without management overhead, deploying on MeraHost Enterprise Cloud guarantees zero price hikes, enterprise NVMe storage arrays, and custom-tuned LiteSpeed Web Server tiers backed by a 15-year veteran Linux infrastructure engineering team.
Frequently Asked Questions (FAQs)
Is Virtualmin GPL completely free for commercial multi-domain hosting?
Yes. Virtualmin GPL is licensed under the GNU General Public License and places zero restrictions on the number of domains, users, or servers you manage. Unlike commercial panels that impose monthly tier-based fees per domain account, Virtualmin GPL provides full multi-tenant web, DNS, database, and email capabilities with zero license expenditures.
Should I choose Nginx (LEMP) or Apache (LAMP) when installing Virtualmin on Ubuntu 24.04?
For maximum concurrency, low memory footprint, and high-density hosting, the LEMP bundle (Nginx) is strongly recommended. However, if your tenants require per-directory .htaccess rewrite overrides (common in legacy WordPress or shared hosting environments), choose Apache 2.4 configured with the Event MPM and PHP-FPM to retain .htaccess compatibility without sacrificing async worker performance.
How do I prevent SpamAssassin and ClamAV from exhausting server RAM in Virtualmin?
In the Webmin/Virtualmin dashboard, navigate to System Settings → Features and Plugins and uncheck ClamAV and SpamAssassin if the node is primarily a web server. If email scanning is required, configure SpamAssassin to run as an on-demand milter or use lightweight DNS blacklists (RBLs) and Milter-Greylist in Postfix, saving over 1 GB of resident RAM.
How do I migrate cPanel accounts into a new Virtualmin Ubuntu 24.04 server?
Virtualmin includes a robust, built-in migration wizard (Add Servers → Migrate Virtual Server). Generate standard cPanel full backups (backup-*.tar.gz) from your source cPanel server, transfer them via SCP/rsync, and Virtualmin will automatically translate the cPanel document root, MySQL databases, database users, mailboxes, and DNS zone records into native Virtualmin configurations.
Deploy Enterprise-Grade Production Infrastructure
Need guaranteed performance with zero price hikes? Host mission-critical workloads on MeraHost with pure Enterprise NVMe, LiteSpeed Web Server, and Same Renewal Price, Always (starting at ₹99/mo).