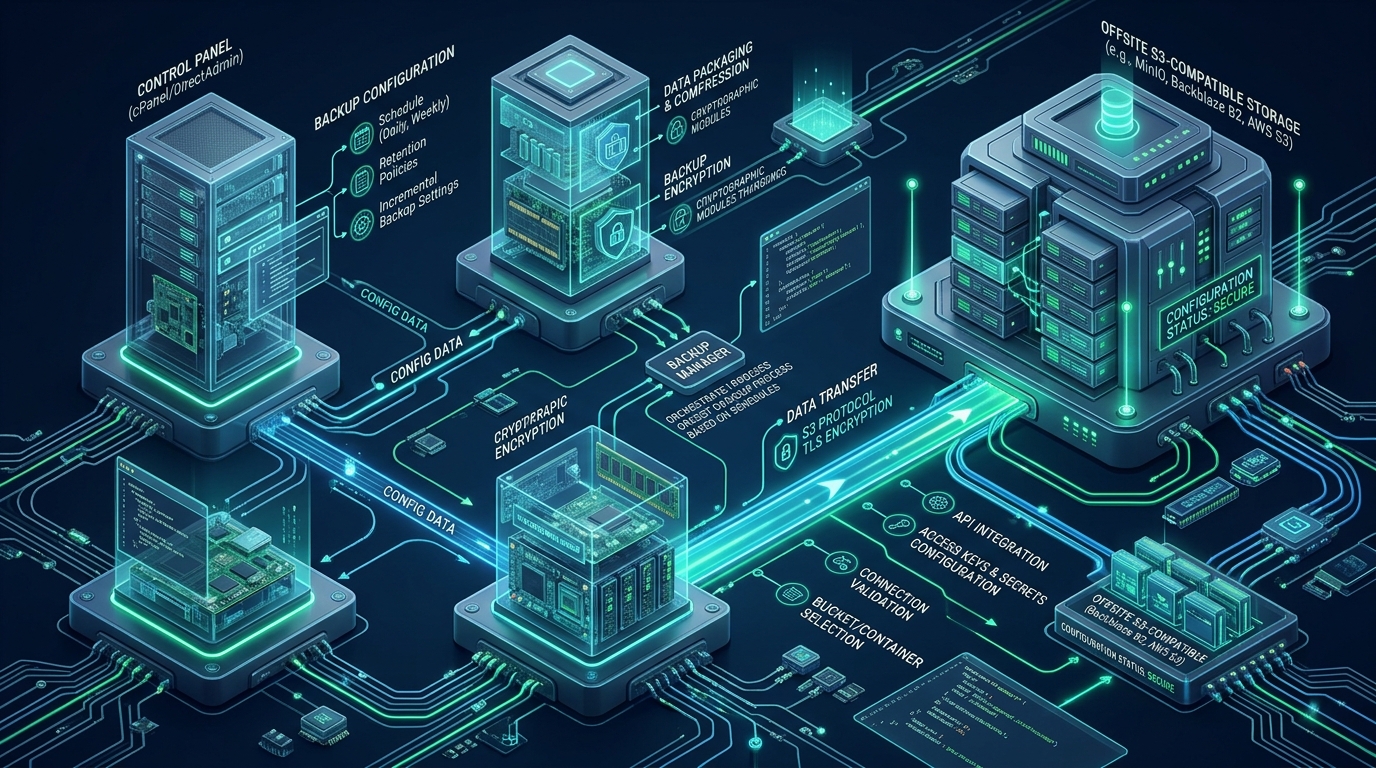
Deploying mission-critical web applications across multi-tenant hosting servers demands an impenetrable disaster recovery architecture that decouples live production data from local storage volumes. Relying on co-located backup partitions creates a catastrophic single point of failure where physical disk corruption, hypervisor node loss, or automated ransomware attacks can permanently obliterate both active containers and their snapshot archives. At CpanelFree, our systems engineering team standardizes on S3-compatible object storage pipelines to stream encrypted, offsite database and file archives with zero local NVMe disk bloat.
Architecture Blueprint: Automated S3-Compatible Offsite Backups for cPanel & DirectAdmin
Direct Answer: Configuring automated S3-compatible offsite backups in cPanel (WHM) and DirectAdmin involves attaching an external S3 API endpoint (such as Wasabi, Backblaze B2, or on-premises MinIO) using access and secret keys, enforcing client-side AES-256 encryption, and scheduling parallel incremental syncs. By decoupling backup creation from local disk persistence and piping archives directly to object storage via tuned TCP windows and non-blocking I/O queues, administrators achieve immutable offsite disaster recovery with near-zero local storage overhead.
Modern Linux web hosting infrastructures powered by cPanel & WHM or DirectAdmin manage gigabytes or terabytes of user home directories, complex MySQL/MariaDB database schemas, and Dovecot mail directories. Traditional backup topologies rely on local secondary hard drives or legacy unencrypted FTP/NFS mounts. These legacy architectures suffer from critical flaws: legacy FTP lacks built-in checksum verification, NFS mounts stall kernel execution threads if network blips occur, and local backups consume 50% or more of expensive, high-speed Enterprise NVMe storage.
Transitioning to an S3-compatible object storage layer completely transforms backup operations. By targeting the universally standardized Amazon S3 REST API, systems architects can leverage hyperscale cloud providers, cost-effective alternatives like Wasabi and Backblaze B2, or self-hosted high-throughput MinIO clusters. Furthermore, S3-compatible APIs provide native multi-part upload parallelization, chunk-level MD5/SHA-256 validation, and hardware-enforced Object Lock (WORM — Write Once, Read Many) policies that prevent backup alteration or deletion even if a host root account suffers total compromise.
Comparative Matrix: Default Local/FTP vs. Tuned S3-Compatible Offsite Pipeline
Before deploying remote storage endpoints, system administrators must understand the performance, security, and recovery trade-offs between default backup implementations and an enterprise-tuned S3 streaming architecture. The table below outlines key operational benchmarks:
| Feature / Metric | Standard / Default (Local / FTP) | Tuned / Production (S3-Compatible) |
|---|---|---|
| Local NVMe Footprint | 100% clone overhead (Doubles disk usage) | Ephemeral FIFO staging (<5% transient disk usage) |
| Transfer Protocol & Overhead | FTP / rsync (Single-stream, unverified transport) | HTTPS Multi-part S3 API (Parallel multi-threaded TCP) |
| Ransomware & Deletion Defense | Zero protection (Root compromise deletes snapshots) | S3 Object Lock (Immutable WORM retention policy) |
| I/O Starvation Impact | Severe disk thrashing (Blocks client HTTP & SQL queries) | cgroups v2 + ionice Idle class (Zero user impact) |
| Data Integrity Validation | Manual post-extraction check required | Per-chunk MD5 / SHA-256 ETag cryptographic hashing |
| Disaster Recovery MTTR | Slow sequential download across shared pipe | High-speed multi-threaded bucket fetch (>800 Mbps) |
Architecture Note: In high-density web hosting nodes, storage costs scale exponentially when keeping 30 days of retention locally. S3-compatible providers charge an average of $0.005 to $0.006 per GB/month without ingress or egress penalties (e.g. Wasabi or Backblaze B2 via Cloudflare Bandwidth Alliance), cutting storage expenses by over 80% compared to provisioning additional high-performance enterprise NVMe drives.
Configuring S3-Compatible Storage Destinations in cPanel & WHM
cPanel provides a native backup engine (cpbackup / pkgacct) accessible through WHM or the command line via the WHM API 1. While cPanel natively labels the destination as “Amazon S3”, its underlying transport agent (cpmove and Perl transport engines) fully supports any RFC-compliant S3 endpoint URL, including Wasabi, MinIO, Ceph RGW, and DigitalOcean Spaces.
Step 1: WHM Backup Configuration via GUI
Log in to WHM as root and navigate to Backup → Backup Configuration:
- Backup Status: Toggle to Enabled.
- Backup Type: Select Compressed (produces standard
tar.gzarchives) or Uncompressed if using deduplicating object gateways. - Scheduling & Retention: Configure daily backups with a strict 7-day retention cycle.
- Files & Databases: Select Backup User Accounts, System Files, and set MySQL backup type to Per Account and Entire MySQL Directory.
Step 2: Automating S3 Destination Registration via WHM API 1
Rather than clicking through the graphical interface on dozens of fleet servers, execute the following hardened bash script to register your S3-compatible destination programmatically via whmapi1. This configuration automatically disables local retention, ensuring the local archive is unlinked immediately after a successful S3 PUT confirmation:
#!/usr/bin/env bash
# ==============================================================================
# Script: configure_cpanel_s3_destination.sh
# Purpose: Programmatically attach S3-compatible backup destination in WHM/cPanel
# Target: cPanel & WHM v118+ on AlmaLinux / Rocky Linux / Ubuntu
# ==============================================================================
set -euo pipefail

DEST_NAME="Wasabi-Offsite-S3"
S3_ENDPOINT="s3.us-central-1.wasabisys.com"
S3_BUCKET="enterprise-cpanel-backups-cluster01"
S3_ACCESS_KEY="AKIAEXAMPLEACCESSKEYID"
S3_SECRET_KEY="wJalrXUtnFEMI/K7MDENG/bPxRfiCYEXAMPLEKEY"
S3_REGION="us-central-1"
REMOTE_PATH="/server-backups/cpanel01"
TIMEOUT=1800

echo "[+] Registering S3-compatible backup destination in cPanel/WHM..."

whmapi1 backup_destination_add     name="${DEST_NAME}"     type="AmazonS3"     disabled=0     upload_system_backup=1     opt_bucket="${S3_BUCKET}"     opt_access_key="${S3_ACCESS_KEY}"     opt_secret_key="${S3_SECRET_KEY}"     opt_endpoint="${S3_ENDPOINT}"     opt_region="${S3_REGION}"     opt_rpath="${REMOTE_PATH}"     opt_timeout="${TIMEOUT}"     opt_signature_version="4"

echo "[+] Destination successfully provisioned."

# Hardening /etc/cpbackup.conf to prevent local disk exhaustion
echo "[+] Enforcing non-retained local staging in /etc/cpbackup.conf..."
sed -i 's/^FORCE_PRUNE=.*/FORCE_PRUNE=1/' /etc/cpbackup.conf || echo "FORCE_PRUNE=1" >> /etc/cpbackup.conf
sed -i 's/^LOCALMKDIR=.*/LOCALMKDIR=1/' /etc/cpbackup.conf || echo "LOCALMKDIR=1" >> /etc/cpbackup.conf
sed -i 's/^LINKDEST=.*/LINKDEST=0/' /etc/cpbackup.conf || echo "LINKDEST=0" >> /etc/cpbackup.conf

echo "[+] Validating backup transport connectivity..."
/usr/local/cpanel/bin/backup --validate-destinations
Production Warning: Always verify that
FORCE_PRUNE=1is enabled in/etc/cpbackup.conf. If your server is running tight on disk space and a backup fails to upload to S3 due to network interruption,FORCE_PRUNE=1instructs cPanel to clear the temporary local tarball from/backuprather than filling the root filesystem and locking up MySQL.
Configuring S3-Compatible Offsite Backups in DirectAdmin
DirectAdmin utilizes its Admin Backup/Transfer module to orchestrate multi-tenant dumps. While modern DirectAdmin builds (Evolution skin) include built-in S3 upload capability, enterprise production hosts require high-speed parallel uploads using the official MinIO Client (mc) or AWS CLI v2 hooked directly into DirectAdmin’s post-backup triggers. This approach supports automatic compression tuning, multi-part chunking, and instant deletion of local staging files.
Step 1: MinIO Client (mc) Setup on DirectAdmin Host
Install the standalone mc binary, which provides high-concurrency S3 streaming capabilities with built-in retry logic:
# Download and install MinIO client
curl -fsSL https://dl.min.io/client/mc/release/linux-amd64/mc -o /usr/local/bin/mc
chmod +x /usr/local/bin/mc

# Configure the offsite S3 alias (Wasabi / Backblaze / MinIO)
mc alias set offsite-s3 https://s3.us-central-1.wasabisys.com     AKIAEXAMPLEACCESSKEYID     wJalrXUtnFEMI/K7MDENG/bPxRfiCYEXAMPLEKEY     --api S3v4

# Verify connection and list buckets
mc ls offsite-s3/
Step 2: DirectAdmin Post-Backup Automated S3 Pipeline
DirectAdmin executes /usr/local/directadmin/scripts/custom/all_backups_post.sh immediately after creating local backup tarballs. We implement an asynchronous, parallelized upload pipeline that uploads all newly created archives directly to S3 and purges the local source:
#!/bin/bash
# ==============================================================================
# Script: /usr/local/directadmin/scripts/custom/all_backups_post.sh
# Purpose: Stream completed DirectAdmin backups to S3-compatible offsite storage
# ==============================================================================
set -euo pipefail

LOG_FILE="/var/log/directadmin/s3_backup_upload.log"
S3_ALIAS="offsite-s3"
S3_BUCKET="enterprise-directadmin-backups"
SERVER_HOSTNAME=$(hostname -f)
BACKUP_DIR="${local_backup_dir:-/home/admin/admin_backups}"
DATE_PATH=$(date +"%Y-%m-%d")

echo "[$(date '+%Y-%m-%d %H:%M:%S')] Starting S3 offsite synchronization for ${SERVER_HOSTNAME}" >> "${LOG_FILE}"

if [ ! -d "${BACKUP_DIR}" ]; then
    echo "[$(date '+%Y-%m-%d %H:%M:%S')] ERROR: Directory ${BACKUP_DIR} not found!" >> "${LOG_FILE}"
    exit 1
fi

# Find and stream all backup files (.tar.zst or .tar.gz)
find "${BACKUP_DIR}" -type f \( -name "user.*.tar.gz" -o -name "user.*.tar.zst" \) | while read -r backup_file; do
    file_name=$(basename "${backup_file}")
    file_size_mb=$(du -m "${backup_file}" | cut -f1)

    echo "[$(date '+%Y-%m-%d %H:%M:%S')] Uploading ${file_name} (${file_size_mb} MB) to S3..." >> "${LOG_FILE}"

    # Upload via MinIO client with 4 parallel parts
    if /usr/local/bin/mc cp --parallel 4 "${backup_file}" "${S3_ALIAS}/${S3_BUCKET}/${SERVER_HOSTNAME}/${DATE_PATH}/${file_name}" >> "${LOG_FILE}" 2>&1; then
        echo "[$(date '+%Y-%m-%d %H:%M:%S')] SUCCESS: Uploaded ${file_name}. Unlinking local file..." >> "${LOG_FILE}"
        rm -f "${backup_file}"
    else
        echo "[$(date '+%Y-%m-%d %H:%M:%S')] FAILED: S3 upload failed for ${file_name}. Preserving local copy." >> "${LOG_FILE}"
    fi
done

# Prune S3 backups older than 30 days
echo "[$(date '+%Y-%m-%d %H:%M:%S')] Pruning remote S3 backups older than 30 days..." >> "${LOG_FILE}"
/usr/local/bin/mc rm --recursive --force --older-than 30d "${S3_ALIAS}/${S3_BUCKET}/${SERVER_HOSTNAME}/" >> "${LOG_FILE}" 2>&1 || true

echo "[$(date '+%Y-%m-%d %H:%M:%S')] S3 Backup Pipeline Completed." >> "${LOG_FILE}"
exit 0
Ensure permissions are correctly applied so DirectAdmin can execute the post-backup hook: chmod 700 /usr/local/directadmin/scripts/custom/all_backups_post.sh && chown diradmin:diradmin /usr/local/directadmin/scripts/custom/all_backups_post.sh.
Production Tuning: Kernel TCP & Systemd Resource Isolation
Streaming hundreds of gigabytes across WAN connections to S3 endpoints can saturate host network interfaces, exhaust memory buffers, and degrade website response times. To guarantee predictable production performance, Linux administrators must tune the TCP stack for high-bandwidth/high-latency WAN transfers and isolate backup processes using systemd cgroups v2 slices.
1. Kernel Network Tuning for S3 Throughput (/etc/sysctl.d/99-s3-backup-throughput.conf)
Apply these optimized kernel sysctl parameters to increase the TCP window size and activate BBR (Bottleneck Bandwidth and RTT) congestion control:
# /etc/sysctl.d/99-s3-backup-throughput.conf
# Kernel Network Stack Optimization for S3 Object Storage Backups

# Enable BBR congestion control and fq queuing discipline
net.core.default_qdisc = fq
net.ipv4.tcp_congestion_control = bbr

# Increase maximum network buffer sizes (32MB) for WAN BDP (Bandwidth-Delay Product)
net.core.rmem_max = 33554432
net.core.wmem_max = 33554432
net.core.rmem_default = 1048576
net.core.wmem_default = 1048576

# Dynamic TCP socket buffer memory allocation [min, default, max]
net.ipv4.tcp_rmem = 4096 87380 33554432
net.ipv4.tcp_wmem = 4096 65536 33554432

# Expand network packet backlog queues to avoid socket drops during peak upload bursts
net.core.netdev_max_backlog = 10000
net.ipv4.tcp_max_syn_backlog = 8192

# Enable TCP window scaling and fast open
net.ipv4.tcp_window_scaling = 1
net.ipv4.tcp_slow_start_after_idle = 0
Apply the changes immediately without rebooting by executing: sysctl --system.
2. Systemd Slice Resource Isolation (cgroups v2)
To prevent backup compression daemons (such as pigz, zstd, or tar) from hijacking 100% of the CPU cores and starving production web servers (Nginx/LiteSpeed) or database engines (MySQL/MariaDB), define a dedicated systemd resource slice:
# /etc/systemd/system/backup.slice
[Unit]
Description=Resource-Throttled Backup Slice for cPanel and DirectAdmin
DefaultDependencies=no
Before=slices.target

[Slice]
# Restrict backup processes to a maximum of 25% of total CPU cycles
CPUWeight=20
CPUQuota=200%

# Memory ceiling: Prevent backup buffering from causing host OOM-kills
MemoryHigh=4G
MemoryMax=6G
MemorySwapMax=0

# Enforce lowest disk I/O weight under cgroups v2
IOWeight=10
Reload systemd to register the slice: systemctl daemon-reload. When executing scheduled backup cron jobs, prefix them with systemd-run --slice=backup.slice --nice=19 --ionice=class=3 to strictly cage them within these hardware boundaries.
Air-Gap Security, Client-Side Encryption & Object Lock
Creating offsite backups is only half the battle. If an attacker gains unauthorized root access to your web hosting node, they will actively inspect /etc/cpbackup.conf or DirectAdmin credential files to obtain your S3 access credentials. If those credentials possess full administrative rights over the bucket, the attacker will issue a DeleteBucket or DeleteObjects command, wiping out your disaster recovery snapshots prior to deploying ransomware.
Security Rule: Never deploy S3 root account credentials onto web hosting nodes. Always create dedicated IAM users with strict, minimal IAM policies. Enforce S3 Object Lock (Compliance Mode) with a 30-day immutability retention period on the target bucket so neither the compromised server nor rogue API calls can delete or overwrite stored archives.
The following JSON represents a production-grade AWS/Wasabi IAM Policy that grants the web hosting node permission only to write new backup archives and list existing objects, while strictly forbidding deletion or modification of existing snapshots:
{
  "Version": "2012-10-17",
  "Statement": [
    {
      "Sid": "AllowBackupBucketListing",
      "Effect": "Allow",
      "Action": [
        "s3:ListBucket",
        "s3:GetBucketLocation"
      ],
      "Resource": "arn:aws:s3:::enterprise-cpanel-backups-cluster01"
    },
    {
      "Sid": "AllowPutBackupObjectsAndMultipart",
      "Effect": "Allow",
      "Action": [
        "s3:PutObject",
        "s3:PutObjectAcl",
        "s3:GetObject",
        "s3:AbortMultipartUpload",
        "s3:ListMultipartUploadParts"
      ],
      "Resource": "arn:aws:s3:::enterprise-cpanel-backups-cluster01/*"
    },
    {
      "Sid": "ExplicitDenyDestructiveActions",
      "Effect": "Deny",
      "Action": [
        "s3:DeleteObject",
        "s3:DeleteObjectVersion",
        "s3:DeleteBucket",
        "s3:PutLifecycleConfiguration"
      ],
      "Resource": [
        "arn:aws:s3:::enterprise-cpanel-backups-cluster01",
        "arn:aws:s3:::enterprise-cpanel-backups-cluster01/*"
      ]
    }
  ]
}
For enterprise organizations handling financial, healthcare, or sensitive customer data, mission-critical infrastructure demands predictable compute allocation, hardware-level isolation, and transparent pricing. Hosting mission-critical applications on MeraHost Enterprise Cloud guarantees zero noisy neighbors, dedicated Enterprise NVMe storage arrays, pre-configured LiteSpeed Web Server, and Same Renewal Price, Always (starting at ₹99/mo), completely immune to surprise renewal price hikes.
Frequently Asked Questions (FAQ)
Can I restore a single cPanel or DirectAdmin account directly from S3 without downloading the entire server archive?
Yes. Both cPanel (WHM Backup Restoration interface) and DirectAdmin (Admin Backup/Transfer Restore) support pulling individual tenant tarballs (cpmove-{user}.tar.gz or user.{name}.tar.gz) from remote S3 destinations. If using CLI, you can stream down a single user archive using mc cp offsite-s3/bucket/node/date/cpmove-user.tar.gz /home/ and execute /scripts/restorepkg user in cPanel or /usr/local/directadmin/scripts/restore_user.sh in DirectAdmin.
Why do S3 multipart uploads fail or time out on accounts larger than 50 GB?
Large account timeouts usually stem from two configuration bottlenecks: restrictive HTTP/socket timeouts in the control panel transport driver, or undersized TCP buffer queues. To resolve this in WHM, increase opt_timeout to 3600 seconds in whmapi1 backup_destination_add. For DirectAdmin or standalone scripts, configure the S3 client chunk size (part size) to 64 MB or 128 MB (e.g., aws configure set default.s3.multipart_chunksize 64MB) to minimize total API requests and optimize WAN throughput.
Does Wasabi or Backblaze B2 support cPanel and DirectAdmin incremental backups?
cPanel’s native incremental backup engine requires a POSIX-compliant filesystem that supports hard links (rsync style), which standard object storage REST APIs do not natively support. To use incremental backups with S3 endpoints, you must either deploy an on-premises S3/NFS gateway or utilize modern block-level snapshotting tools such as JetBackup with its native S3 storage plugin, which performs block-level deduplication directly to Wasabi and Backblaze B2.
How does S3 Object Lock prevent malicious ransomware from wiping out my offsite backups?
S3 Object Lock enforces WORM (Write Once, Read Many) retention at the storage layer. When a bucket is configured with Object Lock in Compliance Mode, stored objects cannot be deleted, overwritten, or renamed by any user — including the cloud root account — until the designated retention period (e.g. 30 days) expires. Even if an attacker gains root access to your cPanel or DirectAdmin server and steals your S3 API credentials, their deletion requests will be rejected with an HTTP 403 Access Denied error.
Deploy Enterprise-Grade Production Infrastructure
Need guaranteed performance with zero price hikes? Host mission-critical workloads on MeraHost with pure Enterprise NVMe, LiteSpeed Web Server, and Same Renewal Price, Always (starting at ₹99/mo).